Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
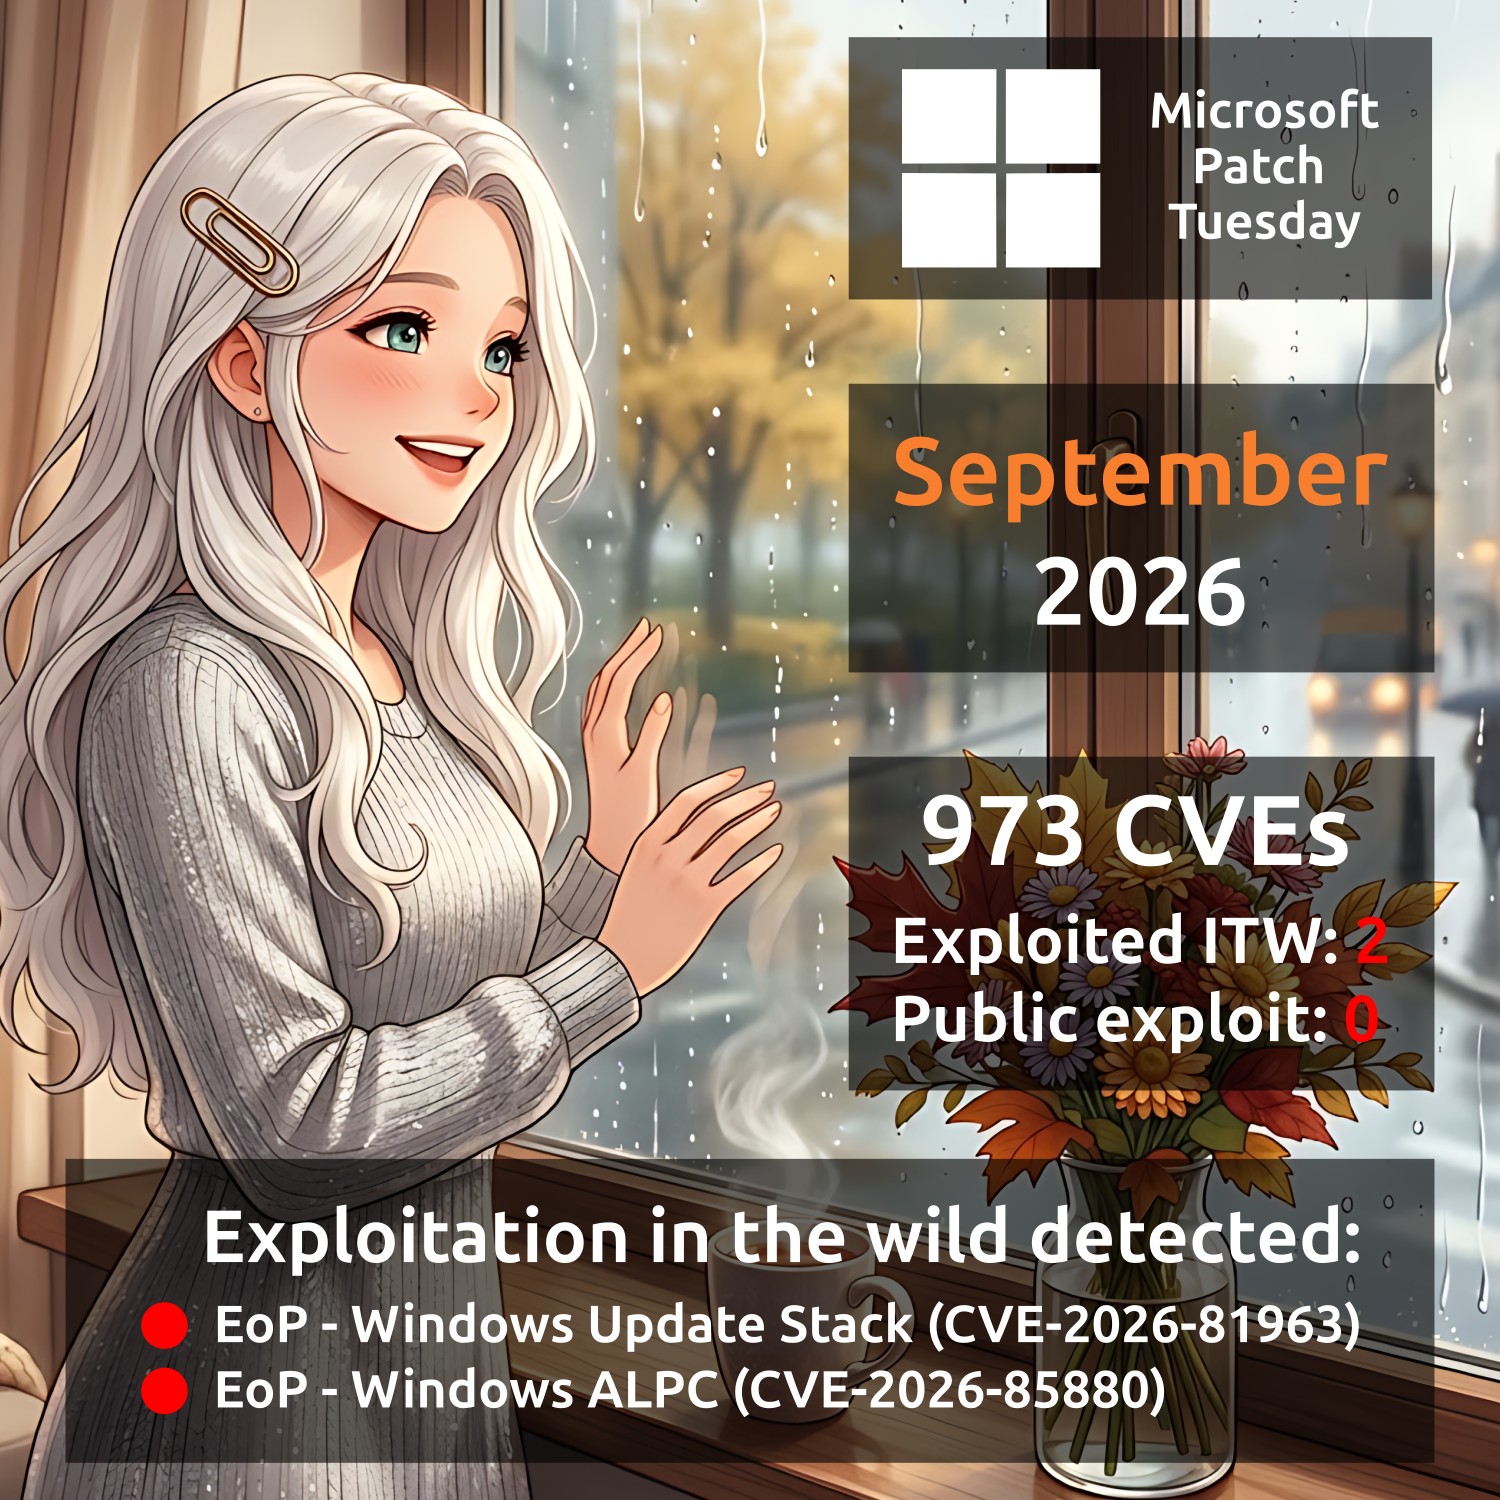
A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLa...
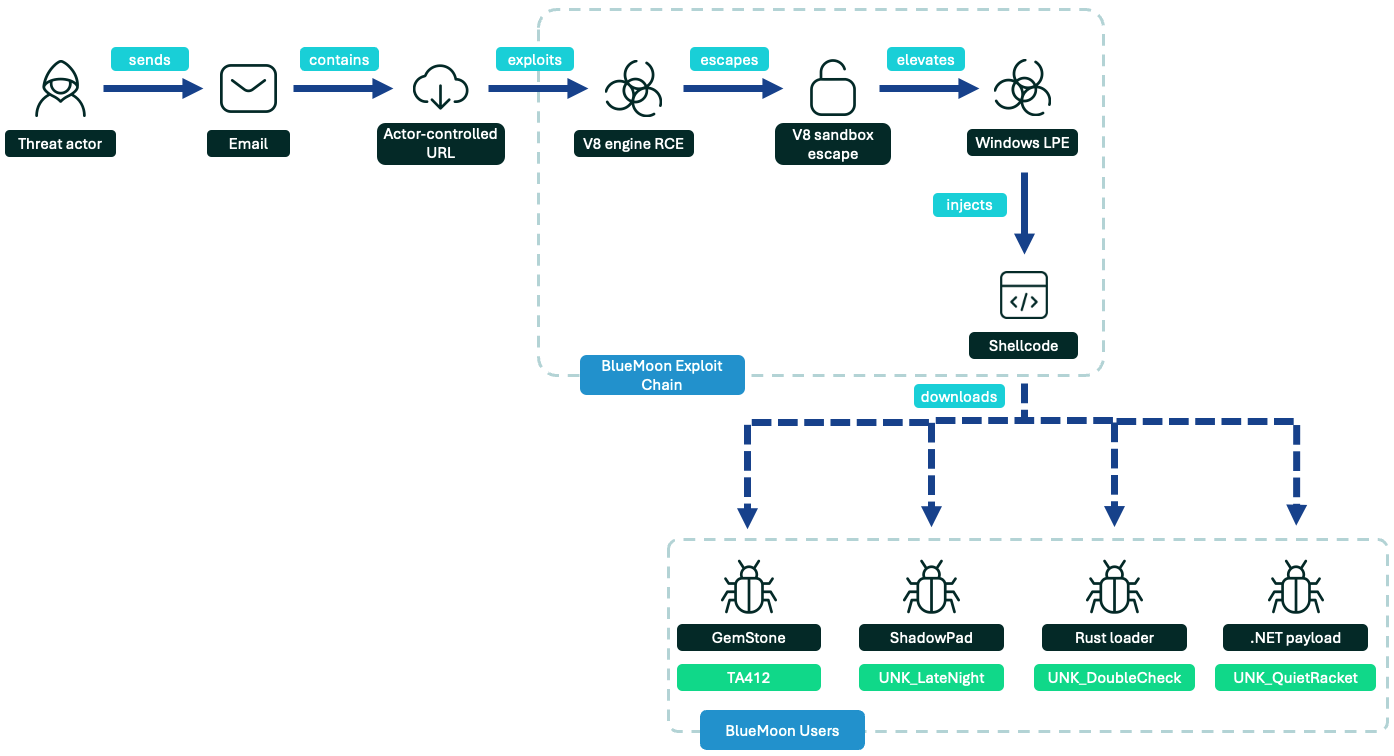
A new exploit kit named BlueMoon has been rapidly adopted by at least four espionage groups, primarily linked to China, exploiting vulnerabilities in Google Chrome and Microsoft Windows. The first observed use of BlueMoon was on August 28, 2026, by the China-aligned threat actor TA412, with subseque...
On September 1, 2026, Chinese threat actors UTA0560 and JungleBamboo executed phishing campaigns targeting NGOs, exploiting zero-day vulnerabilities in Google Chrome and Microsoft Windows. The attack utilized a spear-phishing email that redirected victims to a compromised U.S.-based university websi...
On September 8, 2026, Microsoft released a security update addressing critical vulnerabilities in its products, notably CVE-2026-85880 and CVE-2026-81963, both of which were confirmed to be actively exploited before the update was issued. The vulnerabilities involve privilege escalation in Windows A...