Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code...
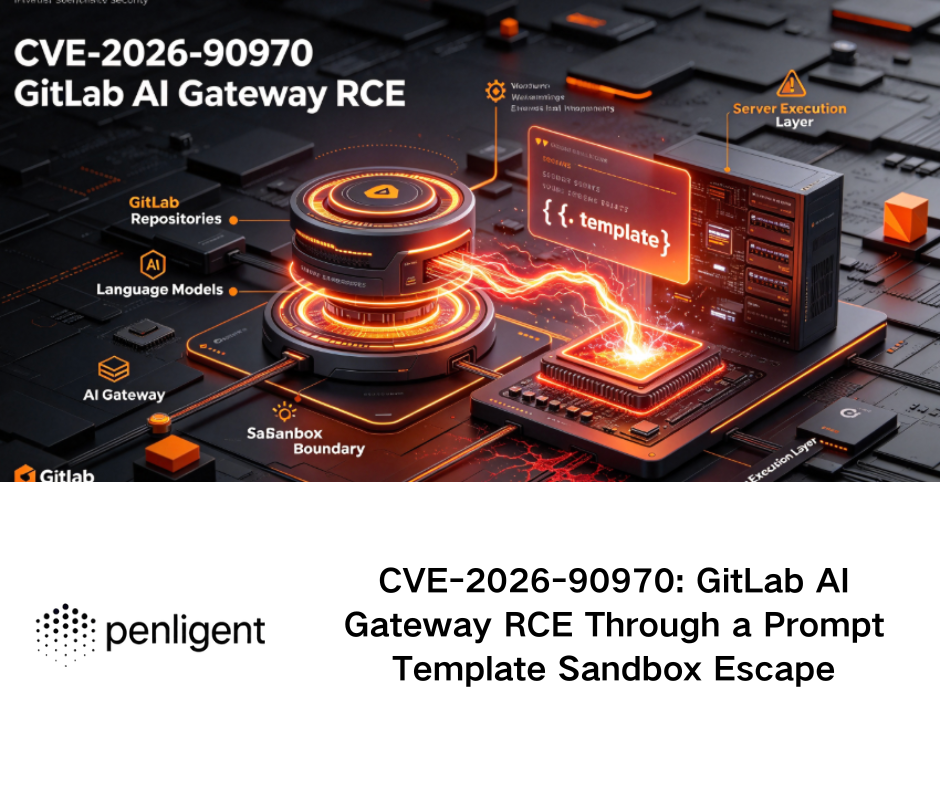
GitLab has disclosed a critical remote code execution vulnerability, CVE-2026-90970, affecting self-hosted AI Gateways. The flaw allows authenticated users with Duo Agent Platform access to escape a prompt template sandbox and execute arbitrary commands on the gateway. GitLab released patches in ver...
GitLab and Dell released critical patches for remote code execution vulnerabilities on October 3, 2026. GitLab's AI Gateway vulnerability (CVE-2026-90970) allows arbitrary command execution on self-hosted instances, with a CVSS score of 9.9. Dell's Container Storage Modules have critical flaws (CVSS...
On October 2, 2026, GitLab disclosed a critical vulnerability (CVE-2026-90970) in its AI Gateway component, affecting self-hosted deployments with Duo AI features. The vulnerability, which has a CVSS score of 9.9, allows authenticated users with low privileges to execute arbitrary commands on the ho...