Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
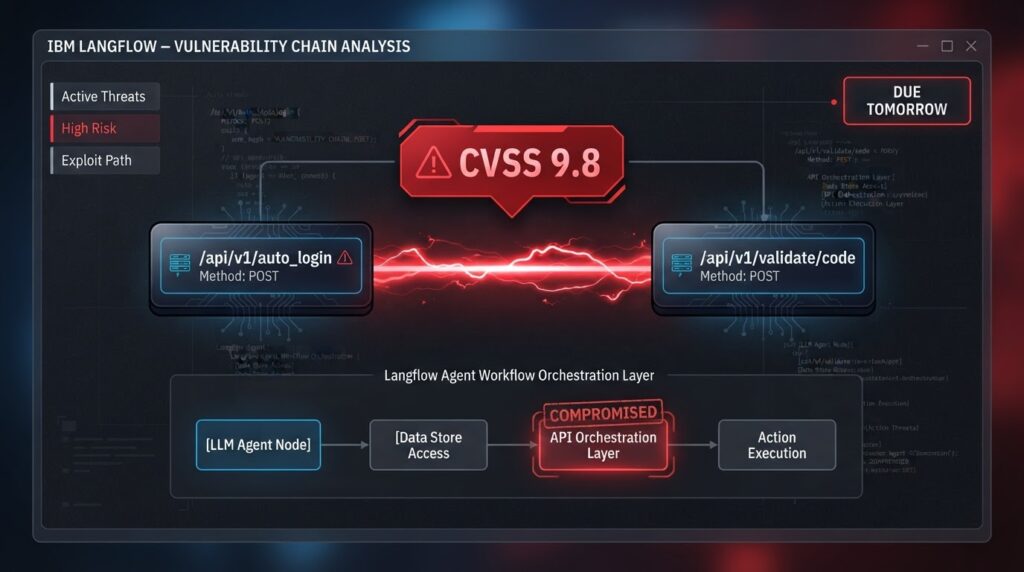
IBM Langflow OSS is facing a critical remote code execution (RCE) vulnerability, tracked as CVE-2026-9198, which allows unauthenticated attackers to execute arbitrary code on default deployments. The vulnerability combines an authentication bypass with a code execution flaw, enabling attackers to ga...
CISA has added critical vulnerabilities in IBM Langflow, Apache Tomcat, and N-able N-central to its Known Exploited Vulnerabilities catalog, with a deadline for federal agencies to patch by August 7, 2026. The Langflow flaw (CVE-2026-9198) allows remote code execution, while the Tomcat flaw (CVE-202...
BeyondTrust has issued a warning regarding a critical remote code execution (RCE) vulnerability in its Remote Support and Privileged Remote Access software. The flaw, tracked as CVE-2026-1731, allows unauthenticated attackers to execute arbitrary code remotely and affects versions 25.3.1 or earlier...