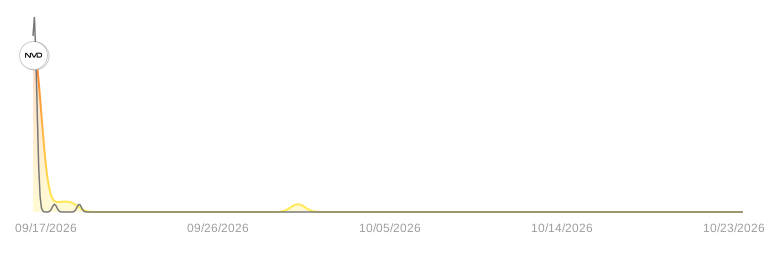
Frequency
3
occurrences
First Seen
September 17, 2026
Last Seen
September 18, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A critical path traversal vulnerability (CVE-2026-92355) has been identified in affected versions of Octopus Server, allowing authenticated users with permissions to modify non built-in external feeds to overwrite arbitrary files. This flaw could potentially lead to remote code execution depending o...
Public Exploits
Checking GitHub for proof-of-concept code…