Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
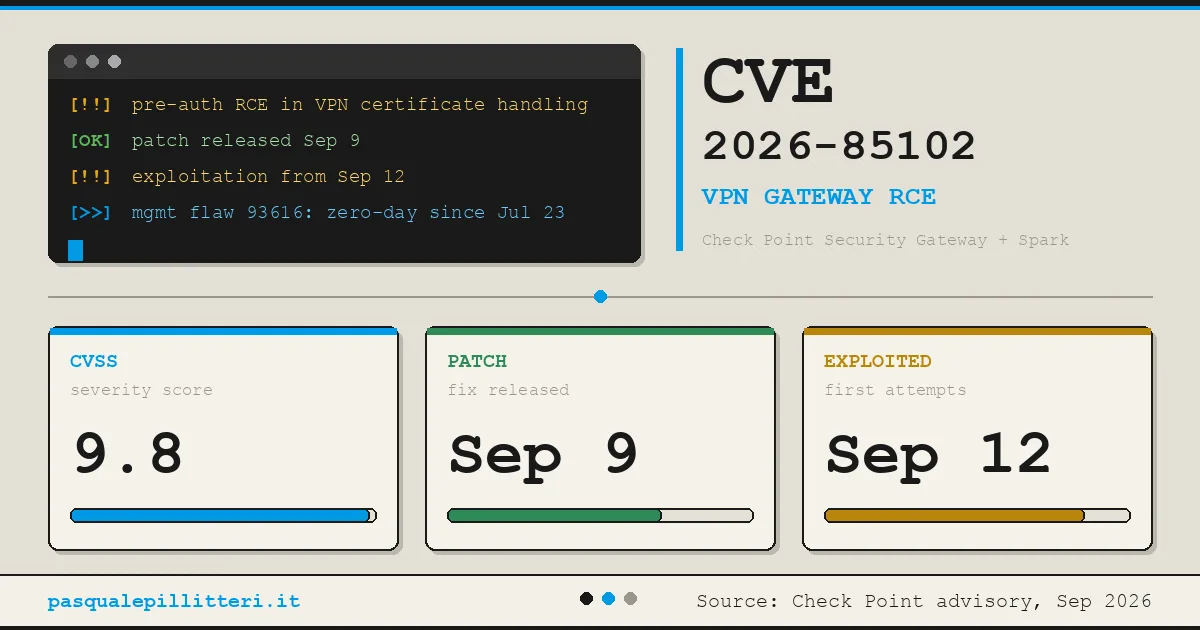
F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Chec...
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, with a CVSS score of 9.8. This path traversal vulnerability allows unauthenticated attackers to write arbitrary files on affected systems via crafted HTTP or HTTPS requests. The flaw has been confirmed to be ac...
A critical vulnerability, CVE-2026-93952, has been identified in Arista Networks' VeloCloud Orchestrator (VCO), allowing unauthenticated remote access to privileged internal functionalities. This flaw, rated CVSS 3.1 10.0 and CVSS 4.0 9.5, affects on-premises deployments configured with certificate-...
Arista Networks has patched a critical SQL injection vulnerability, CVE-2026-114625, in its VeloCloud Orchestrator (VCO) that allows authenticated users to escalate privileges to superuser status. The flaw, rated 9.9 on the CVSS scale, has been actively exploited in the wild, affecting on-premises d...