Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
SonicWall disclosed two critical vulnerabilities in its SMA1000 series appliances, CVE-2026-83548 and CVE-2026-83549, which are being actively exploited. CVE-2026-83548 is a pre-authentication server-side request forgery (SSRF) vulnerability rated 10.0 on the CVSS scale, allowing unauthenticated att...
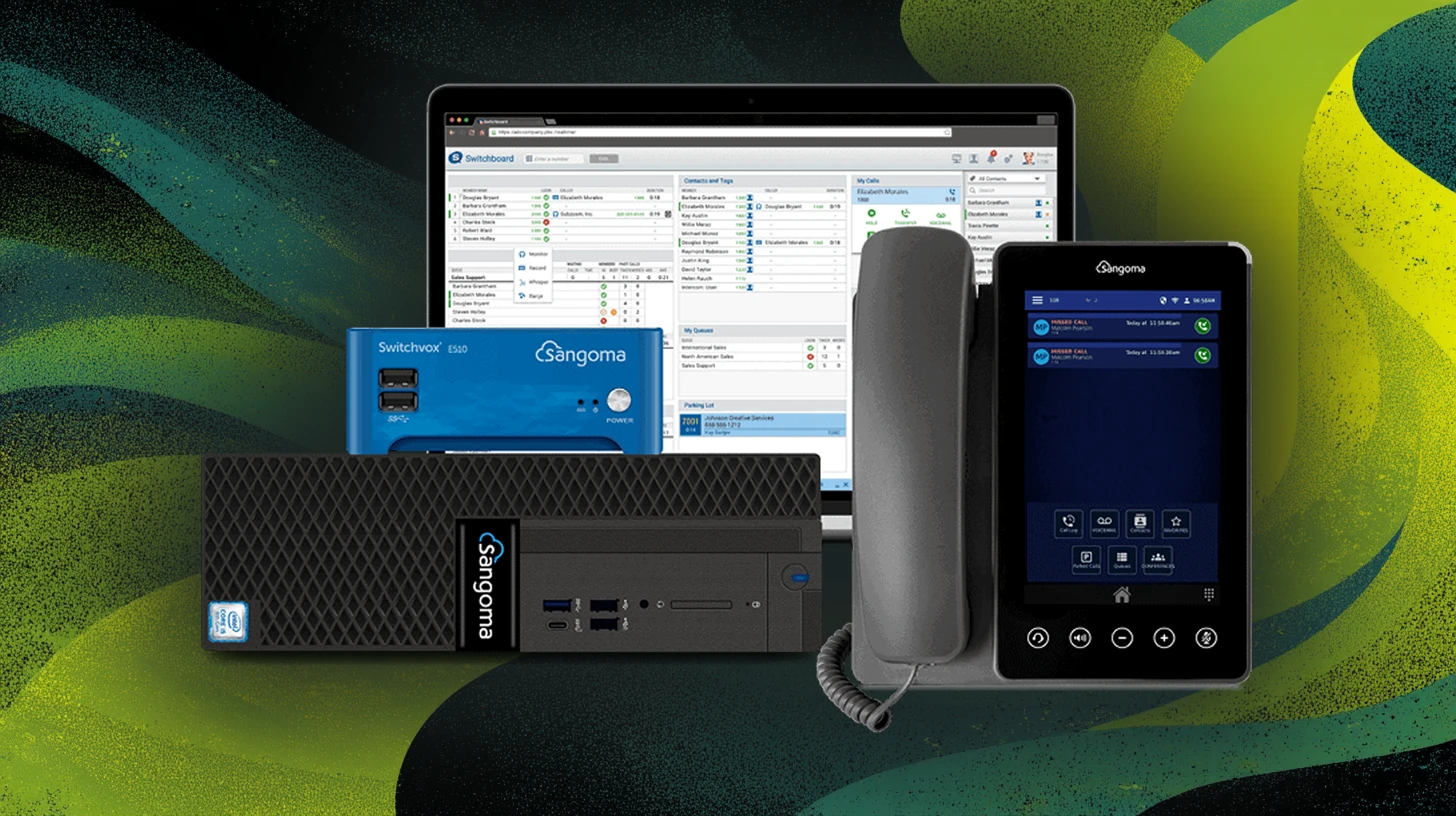
Sangoma Switchvox SMB Edition 8.3 is facing active exploitation of multiple vulnerabilities, particularly CVE-2026-9586, which allows unauthenticated SQL injection leading to remote code execution. The flaw can be exploited by sending crafted HTTP POST requests to the /pa endpoint, enabling attacker...
CISA has added seven new vulnerabilities to its Known Exploited Vulnerabilities Catalog, including CVE-2026-9586, a SQL injection vulnerability in Sangoma Switchvox, and several others affecting SonicWall and JFrog products. These vulnerabilities pose significant risks due to active exploitation. Co...
On September 8, 2026, Microsoft released a record-breaking 974 patches for vulnerabilities across its products, including two actively exploited zero-day vulnerabilities: CVE-2026-81963 and CVE-2026-85880. These vulnerabilities allow local attackers to escalate privileges to SYSTEM level, posing sig...