Skip to content
Product
Use it
Threat intelligence API
Free key, 70+ endpoints, OpenAPI. The product.
Get started
Pick your stack, make your first call.
Live feed
The console: incidents, filters, entities, search.
Recipes
Runnable examples for the free key.
Free feeds
RSS, ransomware feed, IOC blocklist, MISP — no key.
CLI & agents
tc from a terminal; agent keys with scoped budgets.
The data
Incident records
900 articles a day become ~70 scored incidents.
Dark web
First-party leak-site collection: victims, groups, markets.
Validated IOCs
Indicators with a false-positive gate; STIX, MISP, CSV.
Vulnerabilities
CVEs with EPSS, KEV and exploit status.
Entity graph
Actors, malware, CVEs, companies — pivotable.
For teams
For service providers
Per-client feeds, alerts and branded digests.
Use cases
How teams and builders use the corpus.
About ThreatCluster
What it is and how it is built.
Pricing
Docs
Reference
OpenAPI (Swagger)
Every endpoint, parameter and response model.
ReDoc
The same reference, long-form.
Examples on GitHub
curl, Python and Node quickstarts; daily spec snapshot.
Guides
Quickstart & plans
Key, scopes, budgets, tiers.
Integrations
Splunk, Sentinel, Elastic, agents and terminals, step by step
Export formats
STIX 2.1, MISP, CSV, text.
CLI setup
Install, log in, wire an agent.
No results found
Sign in
Get a free key
No results found
Product
Threat intelligence API
Get started
Live feed
Recipes
Free feeds
CLI & agents
The data
Incident records
Dark web
Validated IOCs
Vulnerabilities
Entity graph
For teams
For service providers
Use cases
About ThreatCluster
Docs
OpenAPI (Swagger)
ReDoc
Examples on GitHub
Quickstart & plans
Integrations
Export formats
CLI setup
Pricing
Contact
Get a free key
Sign in
Back
CWE-59 - Improper Link Resolution Before File Access
CWE Weakness
Threat entity extracted from intelligence sources
Sep 25: 0 mentions
Sep 26: 0 mentions
Sep 27: 0 mentions
Sep 28: 0 mentions
Sep 29: 3 mentions
Sep 30: 0 mentions
Oct 1: 0 mentions
Sep 25
Sep 28
Oct 1
Entities
›
cwe
›
CWE-59 - Improper Link Resolution Before File Access
Frequency
14
occurrences
First Seen
April 27, 2026
Last Seen
September 29, 2026
API
Overview
Recent Events
Profile
Profile
MITRE ATT&CK
1 / 2
Tools
Decompress
Docker
Node.js
CVEs
CVE-2026-20313
CVE-2026-33694
CVE-2026-33825
CVE-2026-49176
CVE-2026-50656
CVE-2026-52806
CVE-2026-52811
CVE-2026-52813
Regions
United States
-
REC
Recon
No techniques detected
-
RD
Resource Dev
No techniques detected
1
IA
Initial Access
T1566.001 - Spearphishing Attachment
2
EX
Execution
T1059 - Command and Scripting Interpreter
T1203 - Exploitation for Client Execution
1
PE
Persistence
T1543.003 - Windows Service
2
PE
Priv Esc
T1068 - Exploitation for Privilege Escalation
T1055 - Process Injection
-
DE
Defense Evasion
No techniques detected
-
CA
Cred Access
No techniques detected
-
DI
Discovery
No techniques detected
1
LM
Lateral Mov
T1021 - Remote Services
-
CO
Collection
No techniques detected
-
C2
C2
No techniques detected
-
EX
Exfil
No techniques detected
-
IM
Impact
No techniques detected
7
techniques detected across
5
tactics
Related Clusters (7)
Critical Vulnerability CVE-2026-101894 Exploited via Node.js Archive Extraction
2d ago
·
2 sources
74
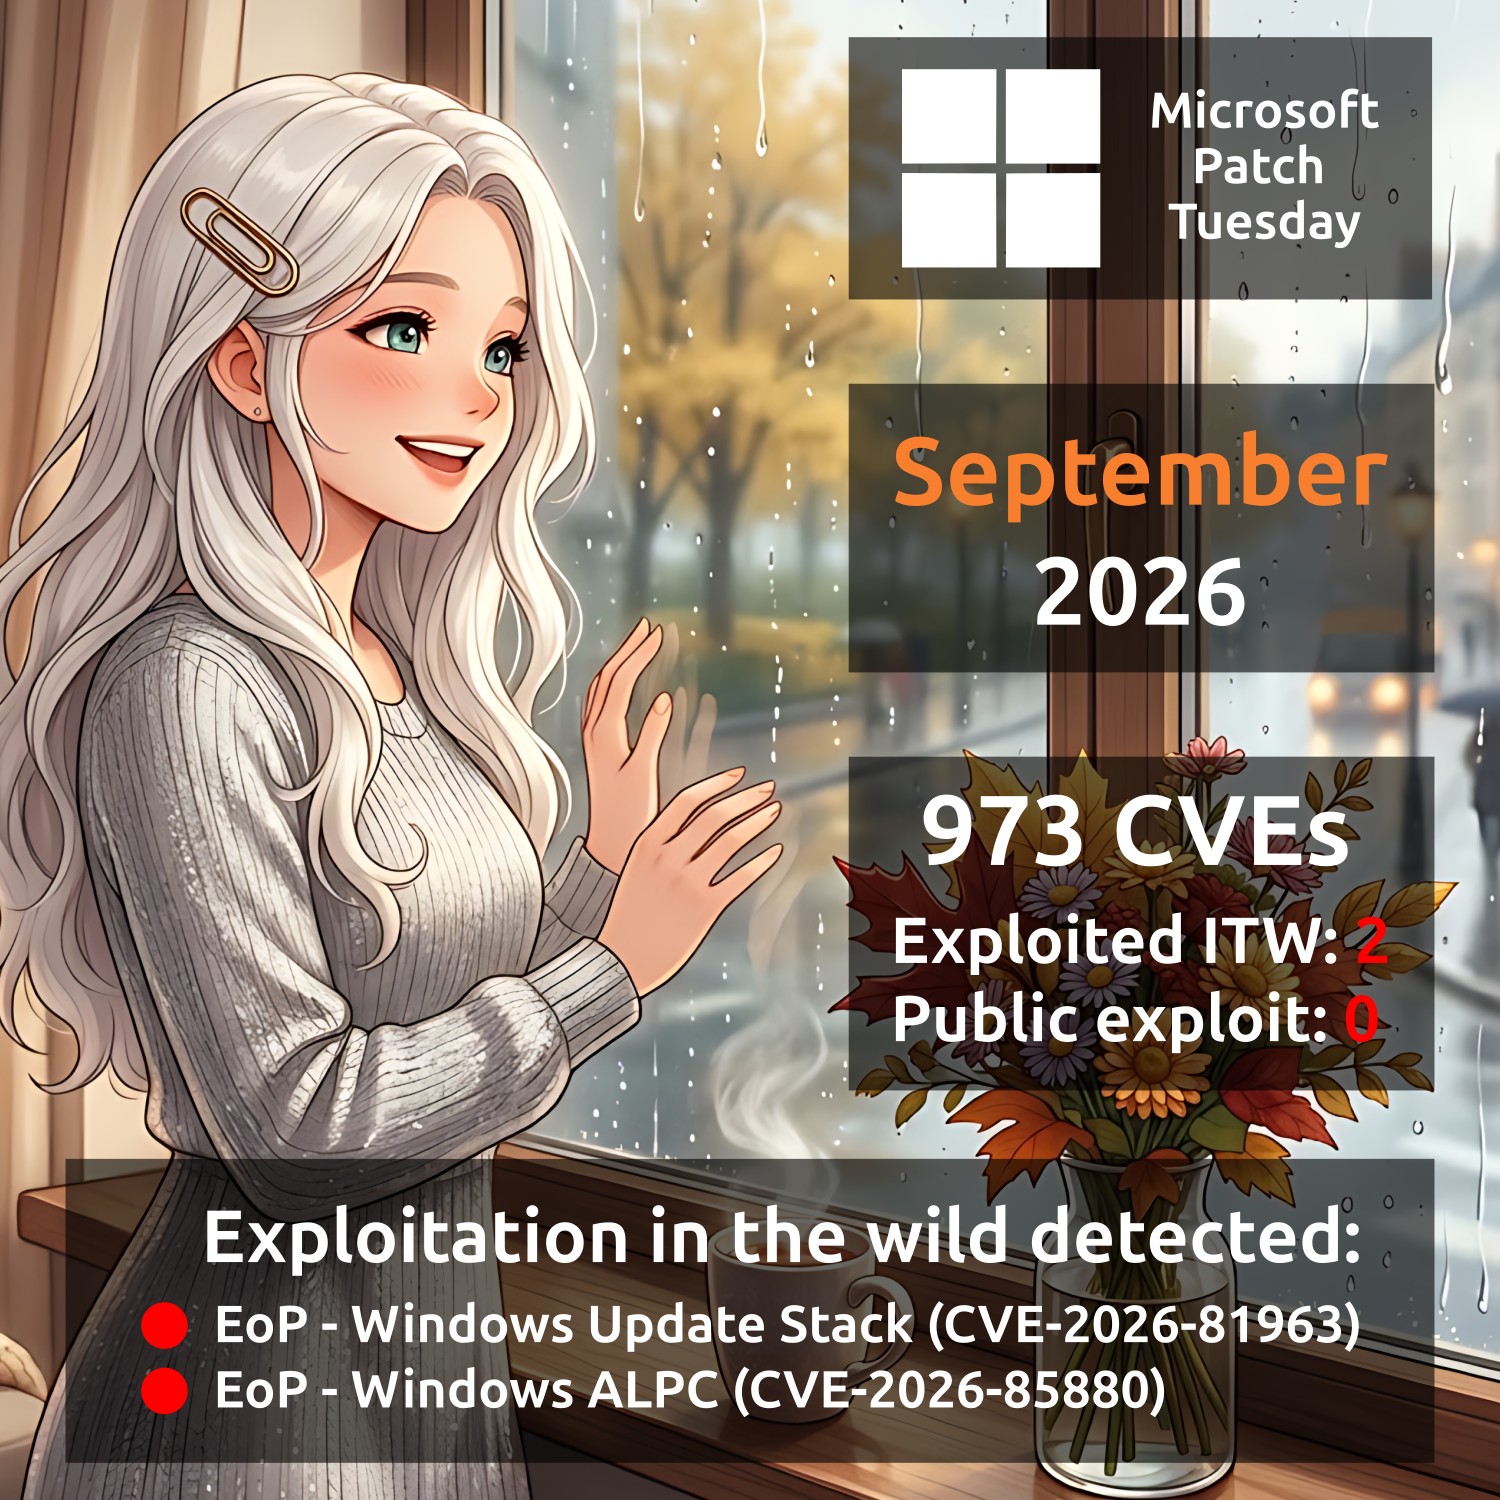
Multiple CVEs Disclosed on September 8, 2026, Affecting Microsoft Products
Sep 8
·
927 sources
74
Critical Docker Vulnerability CVE-2026-17106 Allows Host File Overwrite
Aug 11
·
4 sources
73
Critical Nessus Agent Vulnerability Allows SYSTEM-Level Code Execution
Apr 27
·
2 sources
73
Critical Vulnerabilities in Gogs and Jinjava Require Immediate Patching
Jun 25
·
2 sources
72
Symlink Traversal Flaw in brig Allows Sandbox Escape
2d ago
·
1 sources
58
Multiple Information Disclosure Vulnerabilities in Windows UPnP Device Host
Sep 8
·
2 sources
40
Prev
1 / 2
Next
Related Articles (14)
Tv 2026 1010
www.teamviewer.com
·
1d ago
AI Agent Sandbox Flaw in brig: Symlink Traversal (CVSS 8.2) | Blog
Endorlabs
·
2d ago
Exploit for CVE-2026
Sploitus
·
2d ago
Known Exploited Vulnerabilities Catalog
www.cisa.gov
·
Sep 10
September Microsoft Patch Tuesday
Avleonov
·
Sep 9
CVE-2026
Api.Msrc.Microsoft
·
Sep 8
CVE-2026
Api.Msrc.Microsoft
·
Sep 8
CVE-2026-68830 Windows Universal Plug and Play (UPnP) Device Host Information Disclosure Vulnerability
Api.Msrc.Microsoft
·
Sep 8
CopyEscape: Container-to-host arbitrary file write via docker cp (CVE-2026-17106)
Reddit
·
Aug 11
CC-4825 - Cisco Releases Catalyst SD
Digital.Nhs.Uk
·
Aug 6
Researchers David Carliez demonstrated
davidcarliez.github.io
·
Jul 27
Defender Zero
Techtimes
·
Jul 9
Warning: Multiple Vulnerabilities in Gogs Allow Remote Code Execution, Patch Immediately!
Ccb.Belgium.Be
·
Jun 25
Nessus Agent Windows Flaw Enables SYSTEM
Gbhackers
·
Apr 27
Prev
1 / 3
Next
Related Entities
Zero-day Exploit
Remote Code Execution
Data Breach
Privilege Escalation
Access Control Bypass
Authentication Bypass
Malware
Tenable
Ubuntu
United States
CVE-2026-20313
CVE-2026-33694