Skip to content
Product
Use it
Threat intelligence API
Free key, 70+ endpoints, OpenAPI. The product.
Get started
Pick your stack, make your first call.
Live feed
The console: incidents, filters, entities, search.
Recipes
Runnable examples for the free key.
Free feeds
RSS, ransomware feed, IOC blocklist, MISP — no key.
CLI & agents
tc from a terminal; agent keys with scoped budgets.
The data
Incident records
900 articles a day become ~70 scored incidents.
Dark web
First-party leak-site collection: victims, groups, markets.
Validated IOCs
Indicators with a false-positive gate; STIX, MISP, CSV.
Vulnerabilities
CVEs with EPSS, KEV and exploit status.
Entity graph
Actors, malware, CVEs, companies — pivotable.
For teams
For service providers
Per-client feeds, alerts and branded digests.
Use cases
How teams and builders use the corpus.
About ThreatCluster
What it is and how it is built.
Pricing
Docs
Reference
OpenAPI (Swagger)
Every endpoint, parameter and response model.
ReDoc
The same reference, long-form.
Examples on GitHub
curl, Python and Node quickstarts; daily spec snapshot.
Guides
Quickstart & plans
Key, scopes, budgets, tiers.
Integrations
Splunk, Sentinel, Elastic, agents and terminals, step by step
Export formats
STIX 2.1, MISP, CSV, text.
CLI setup
Install, log in, wire an agent.
No results found
Sign in
Get a free key
No results found
Product
Threat intelligence API
Get started
Live feed
Recipes
Free feeds
CLI & agents
The data
Incident records
Dark web
Validated IOCs
Vulnerabilities
Entity graph
For teams
For service providers
Use cases
About ThreatCluster
Docs
OpenAPI (Swagger)
ReDoc
Examples on GitHub
Quickstart & plans
Integrations
Export formats
CLI setup
Pricing
Contact
Get a free key
Sign in
Back
BodySnatcher
Vulnerability
Threat entity extracted from intelligence sources
Entities
›
vulnerability
›
BodySnatcher
Frequency
7
occurrences
First Seen
January 14, 2026
Last Seen
August 4, 2026
API
Overview
Recent Events
Profile
Profile
MITRE ATT&CK
1 / 2
Tools Used
Censys
Microsoft Teams
Related CVEs
CVE-2025-12420
CVE-2026-0542
MITRE Techniques
T1021 - Remote Services
T1041 - Exfiltration Over C2 Channel
T1190 - Exploit Public-Facing Application
T1195 - Supply Chain Compromise
Affected Platforms
Now Assist AI Agents
Virtual Agent API
Slack
Snyk AI Security Platform
Regions
Brazil
Australia
-
REC
Recon
No techniques detected
-
RD
Resource Dev
No techniques detected
1
IA
Initial Access
T1190 - Exploit Public-Facing Application
-
EX
Execution
No techniques detected
-
PE
Persistence
No techniques detected
-
PE
Priv Esc
No techniques detected
-
DE
Defense Evasion
No techniques detected
-
CA
Cred Access
No techniques detected
-
DI
Discovery
No techniques detected
1
LM
Lateral Mov
T1021 - Remote Services
-
CO
Collection
No techniques detected
-
C2
C2
No techniques detected
1
EX
Exfil
T1041 - Exfiltration Over C2 Channel
-
IM
Impact
No techniques detected
4
techniques detected across
3
tactics
Related Clusters (3)
ServiceNow Data Breach Exposes Customer Data via API Vulnerability
Jun 10
·
14 sources
70
Snyk Launches Evo Continuous Offensive Security for AI-Powered Pentesting
Aug 4
·
4 sources
68
BodySnatcher Vulnerability Enables ServiceNow User Impersonation
Jan 19
·
2 sources
26
Related Articles (7)
Evo Continuous Offensive Security Is Here
Snyk
·
Aug 4
ServiceNow Data Breach: Gated Advisory Left Customers Unaware of Exploited Zero
Techtimes
·
Jun 10
ServiceNow data breach: security issue gives attacker access
Cybernews
·
Jun 10
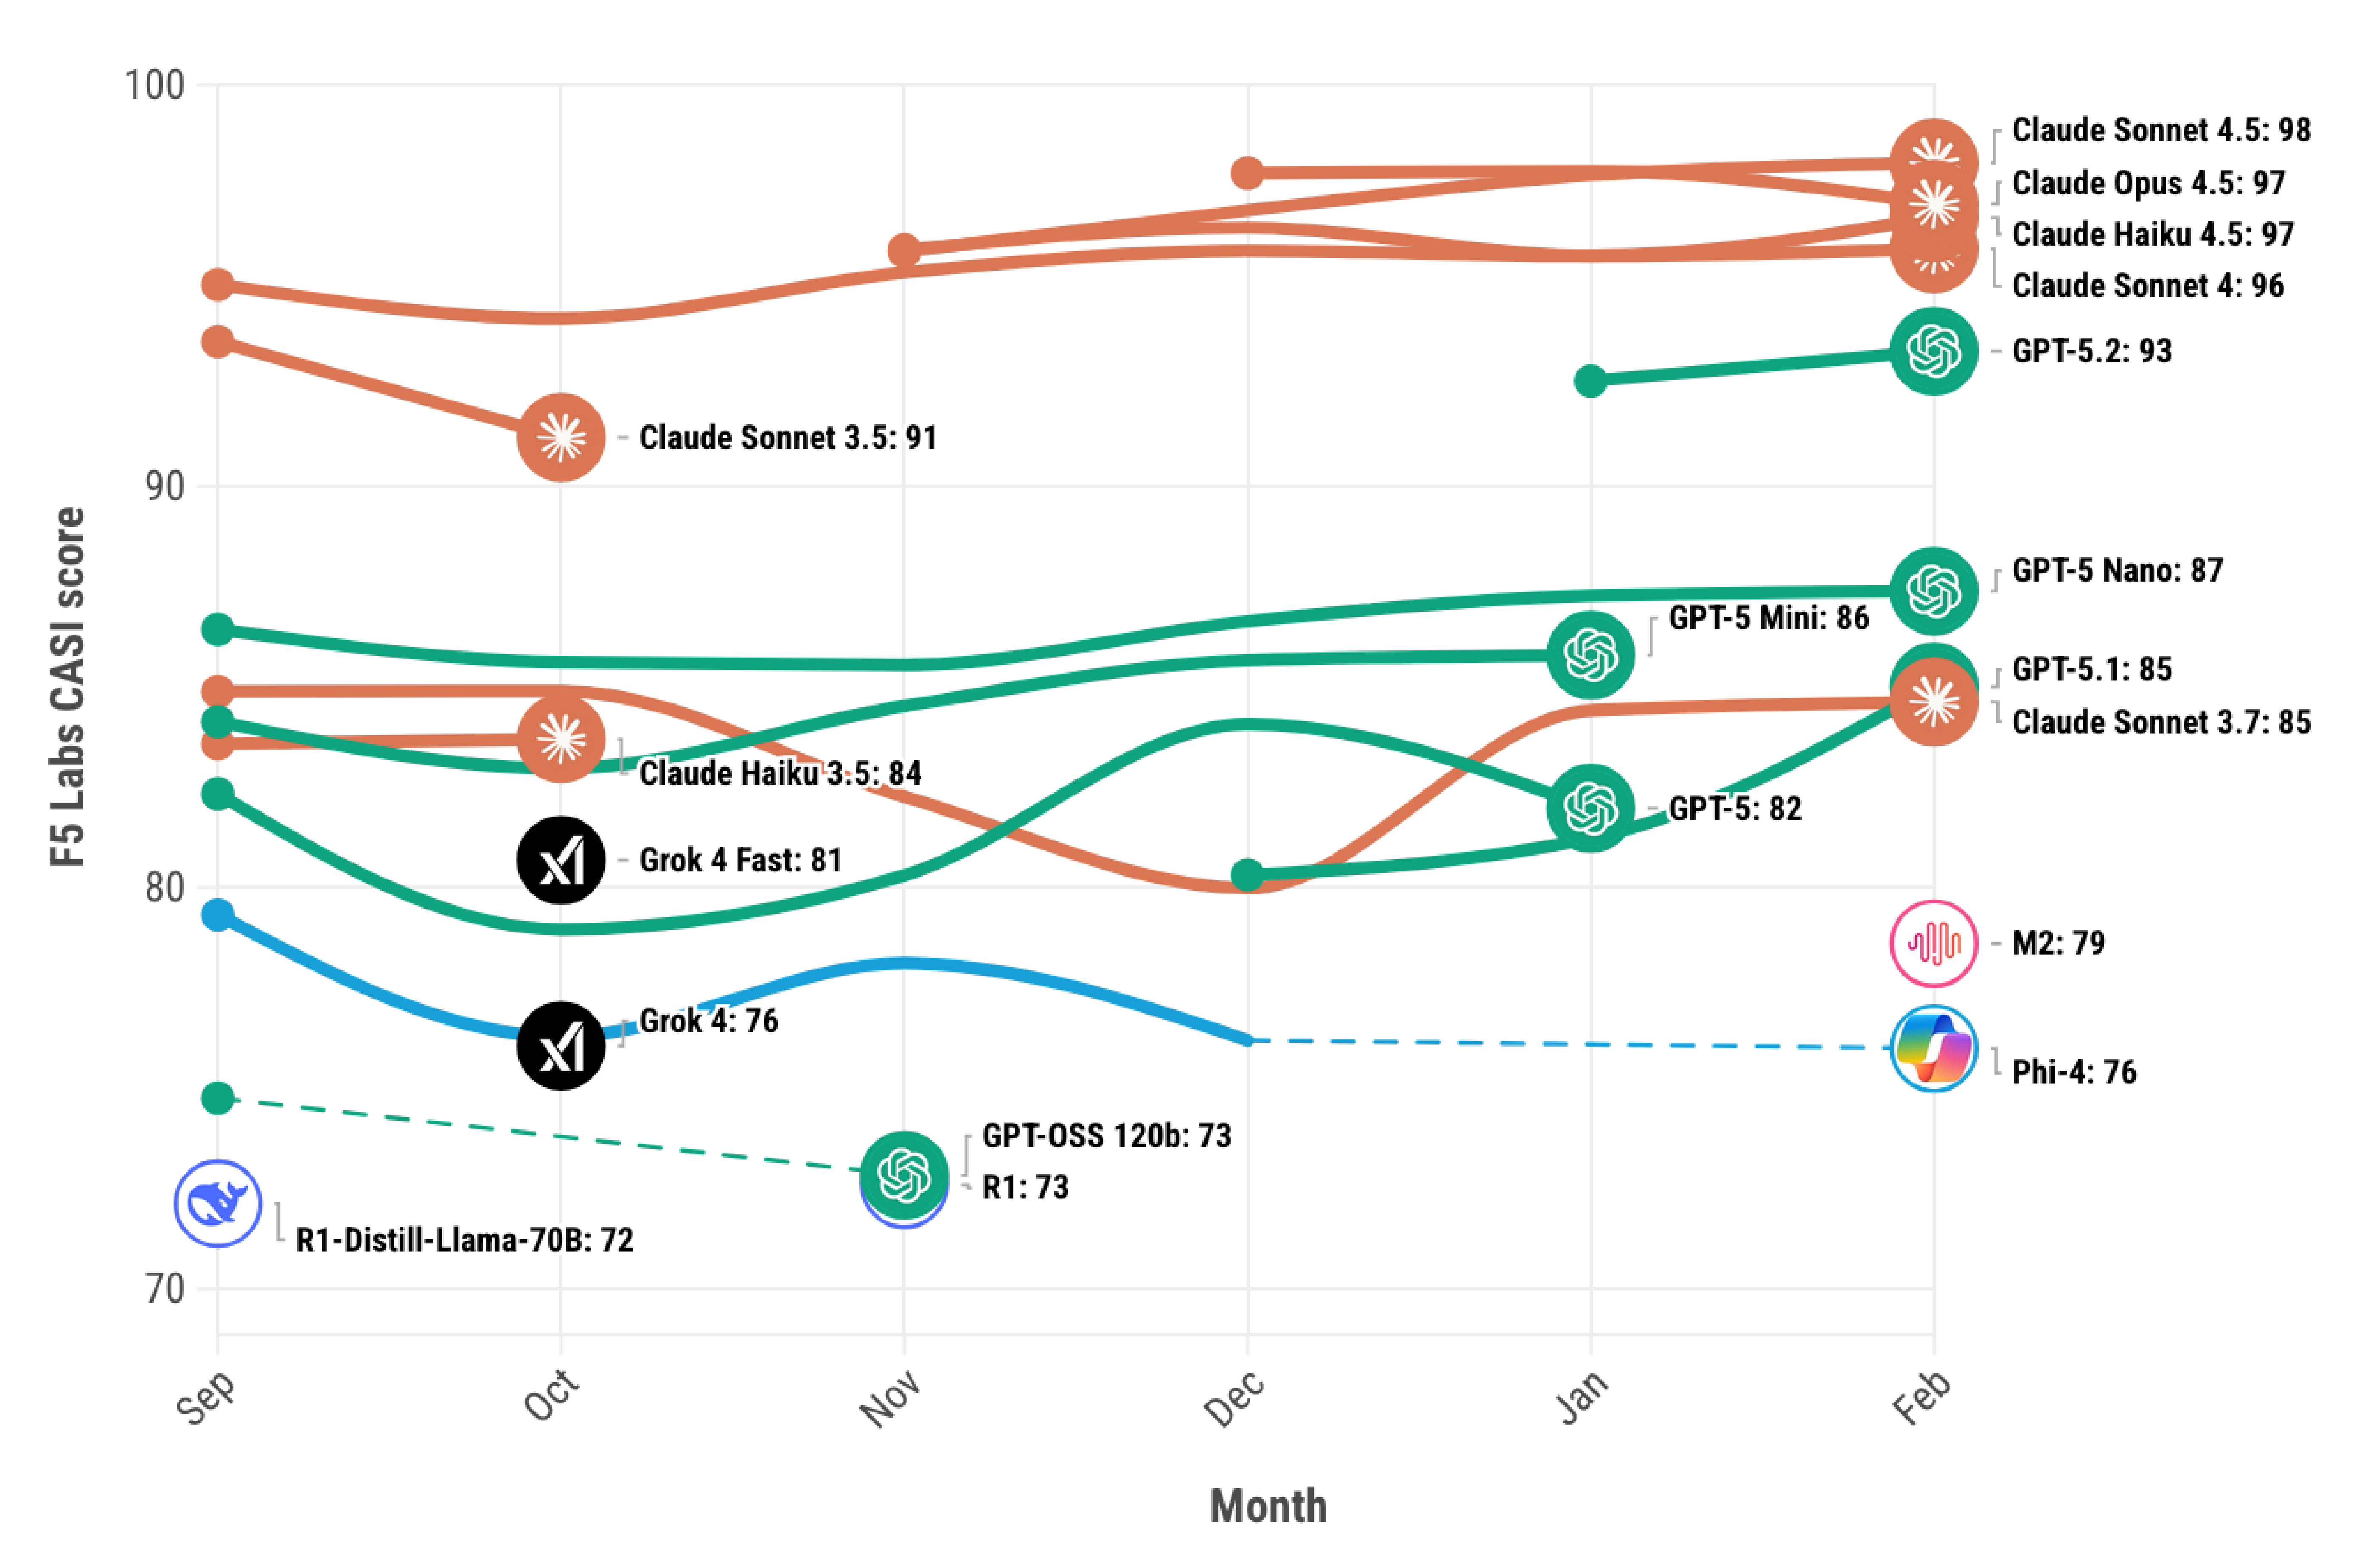
AI Capabilities Are Advancing Faster Than AI Security
F5
·
Feb 26
BodySnatcher Vulnerability Allows Attackers to Impersonate Any ServiceNow User
Cyberpress
·
Jan 19
New “BodySnatcher” Flaw Allows Full ServiceNow User Impersonation
Gbhackers
·
Jan 19
AppOmni Uncovers Agentic AI Security Flaw in ServiceNow
Cxtoday
·
Jan 14
Prev
1 / 2
Next
Related Entities
Data Breach
Cross-site Scripting
Sql Injection
Supply Chain Attack
Worm
ServiceNow
AppOmni
First American
HackerOne
OpenAI
SentinelOne
Brazil