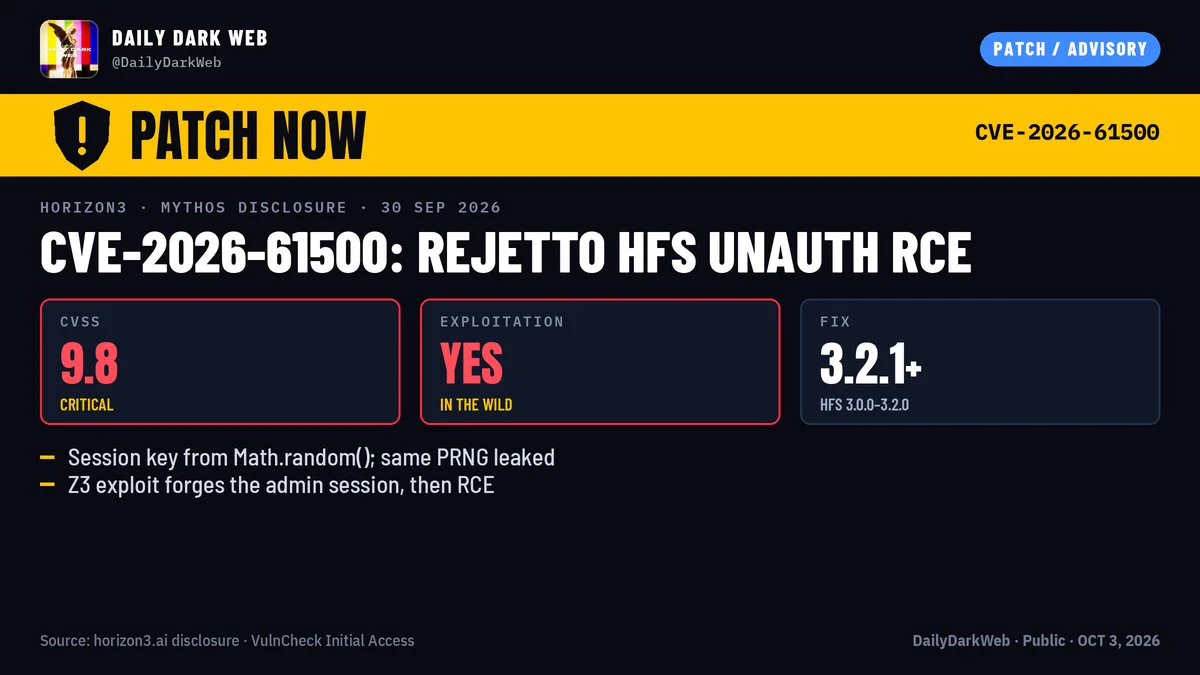
Dark Web Intelligence on X: "🚨 CVE-2026-61500 — REJETTO HTTP FILE SERVER UNAUTHENTICATED RCE
Horizon3 says Anthropic’s Mythos AI found a critical flaw in Rejetto HTTP File Server (HFS): unauthenticated remote code execution, CVSS 9.8.
• HFS session keys are built with Math.random(), a reversible PRNG
• A separate unauthenticated path leaks outputs from the same generator
• Mythos built a Z3 exploit that recovers the admin session key and gets RCE
• Affected: HFS 3.0.0 through 3.2.0. Fixed in 3.2.1 and later
VulnCheck Canary began observing exploitation on October 1, 2026. That activity was a China-hosted IP targeting hosts in the US, and also Japan. VulnCheck added CVE-2026-61500 to VulnCheck KEV. Roughly 100 internet-facing HFS instances. It is not in CISA KEV.
This is a short path from AI-assisted discovery to exploitation. Horizon3 published the Mythos write-up on September 30, 2026. VulnCheck Canary saw exploitation the day. The bug is a predictable session signing key, not a memory-corruption flaw, and the model still produced a working solver that recovers the admin key. Exposed HFS 3.x should be updated to 3.2.1 or later.
#DDW #DarkWeb #CyberSecurity #ThreatIntelligence #CVE"
🚨 CVE-2026-61500 — REJETTO HTTP FILE SERVER UNAUTHENTICATED RCE
Horizon3 says Anthropic’s Mythos AI found a critical flaw in Rejetto HTTP File Server (HFS): unauthenticated remote code execution, CVSS 9.8.
• HFS session keys are built with Math.random(), a reversible PRNG
• A separate unauthenticated path leaks outputs from the same generator
• Mythos built a Z3 exploit that recovers the admin session key and gets RCE
• Affected: HFS 3.0.0 through 3.2.0. Fixed in 3.2.1 and later
VulnCheck Canary began observing exploitation on October 1, 2026. That activity was a China-hosted IP targeting hosts in the US, and also Japan. VulnCheck added CVE-2026-61500 to VulnCheck KEV. Roughly 100 internet-facing HFS instances. It is not in CISA KEV.
This is a short path from AI-assisted discovery to exploitation. Horizon3 published the Mythos write-up on September 30, 2026. VulnCheck Canary saw exploitation the day. The bug is a predictable session signing key, not a memory-corruption flaw, and the model still produced a working solver that recovers the admin key. Exposed HFS 3.x should be updated to 3.2.1 or later.
GitHub - aramosf/CVE-2026-61500: CVE-2026-61500 Rejetto HFS predictable PRNG session forgery to RCE...
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
