Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
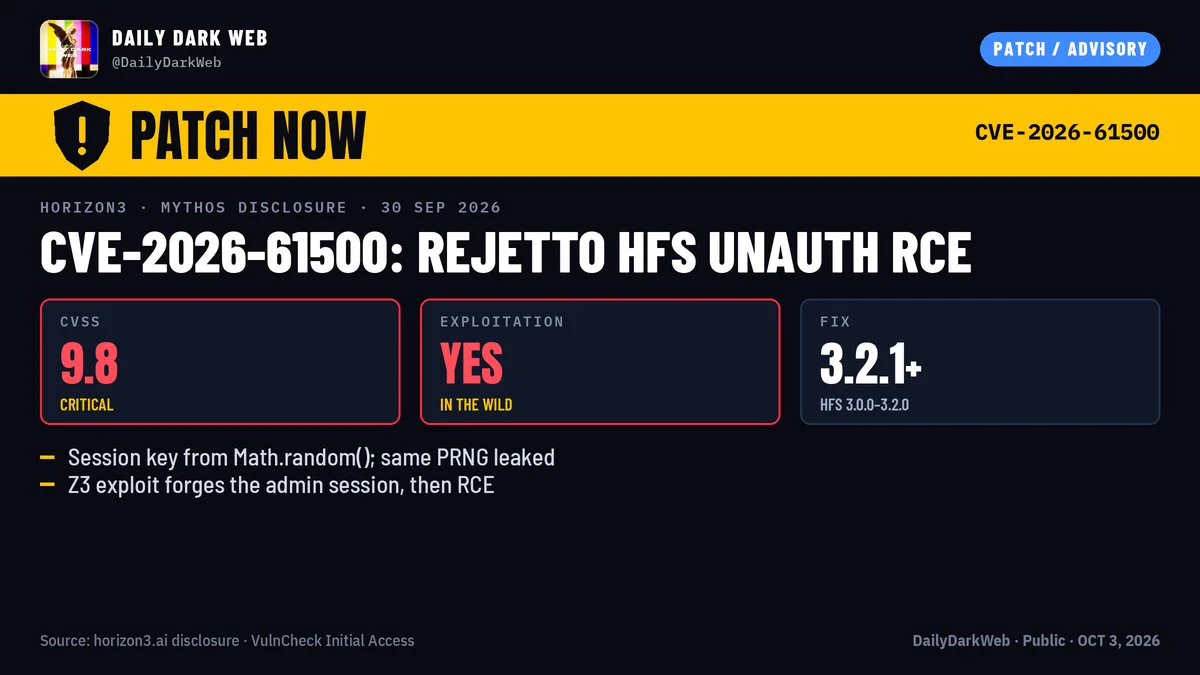
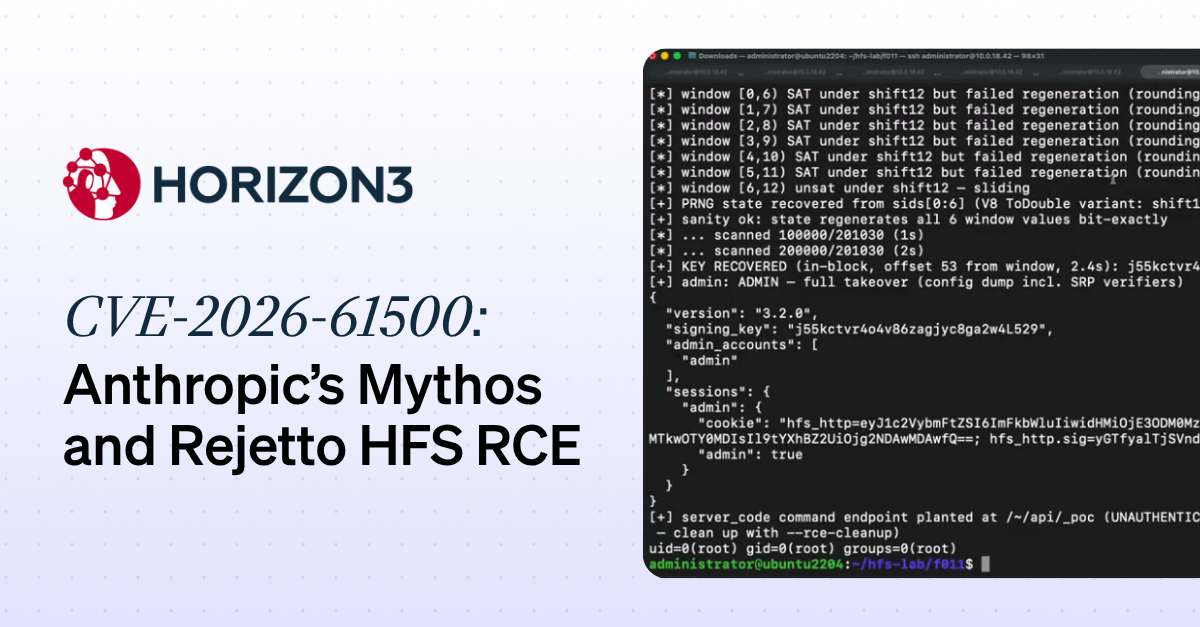
Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with...
A critical vulnerability, CVE-2026-61500, in Rejetto HTTP File Server (HFS) allows unauthenticated remote code execution (RCE) due to a weak pseudo-random number generator (PRNG) used for session keys. Discovered by Anthropic's Mythos AI, the flaw affects HFS versions 3.0.0 to 3.2.0, with a CVSS sco...
Palo Alto Networks disclosed a remote code execution (RCE) vulnerability, CVE-2026-0322, affecting the management interface of PAN-OS software. This flaw allows authenticated attackers with network access to execute arbitrary code with root privileges on affected firewalls. The vulnerability has a C...
Samsung's October 2026 security update, released on October 6, addresses 83 vulnerabilities across its Galaxy devices. This includes nine Android vulnerabilities, with CVEs such as CVE-2026-20519 and CVE-2026-20520, and 33 high-severity flaws. The update also includes four high-severity patches from...