 Back Freightwaves
Cybersecurity portal to fight bad guys open for business: NMFTA
Long Beach, California–Numerous speakers at the cybersecurity conference of the National Motor Freight Traffic Association here talked the need for cooperation to fight cybercrooks. That same theme was heard a year ago at the 2025 version of the NMFTA’s conference.
The discussion last year led to action: the creation of the NMFTA’s Threat Report Portal, where companies that are either victims of a cybersecurity breach or who saw one coming and fought it off can their experiences…anonymously.
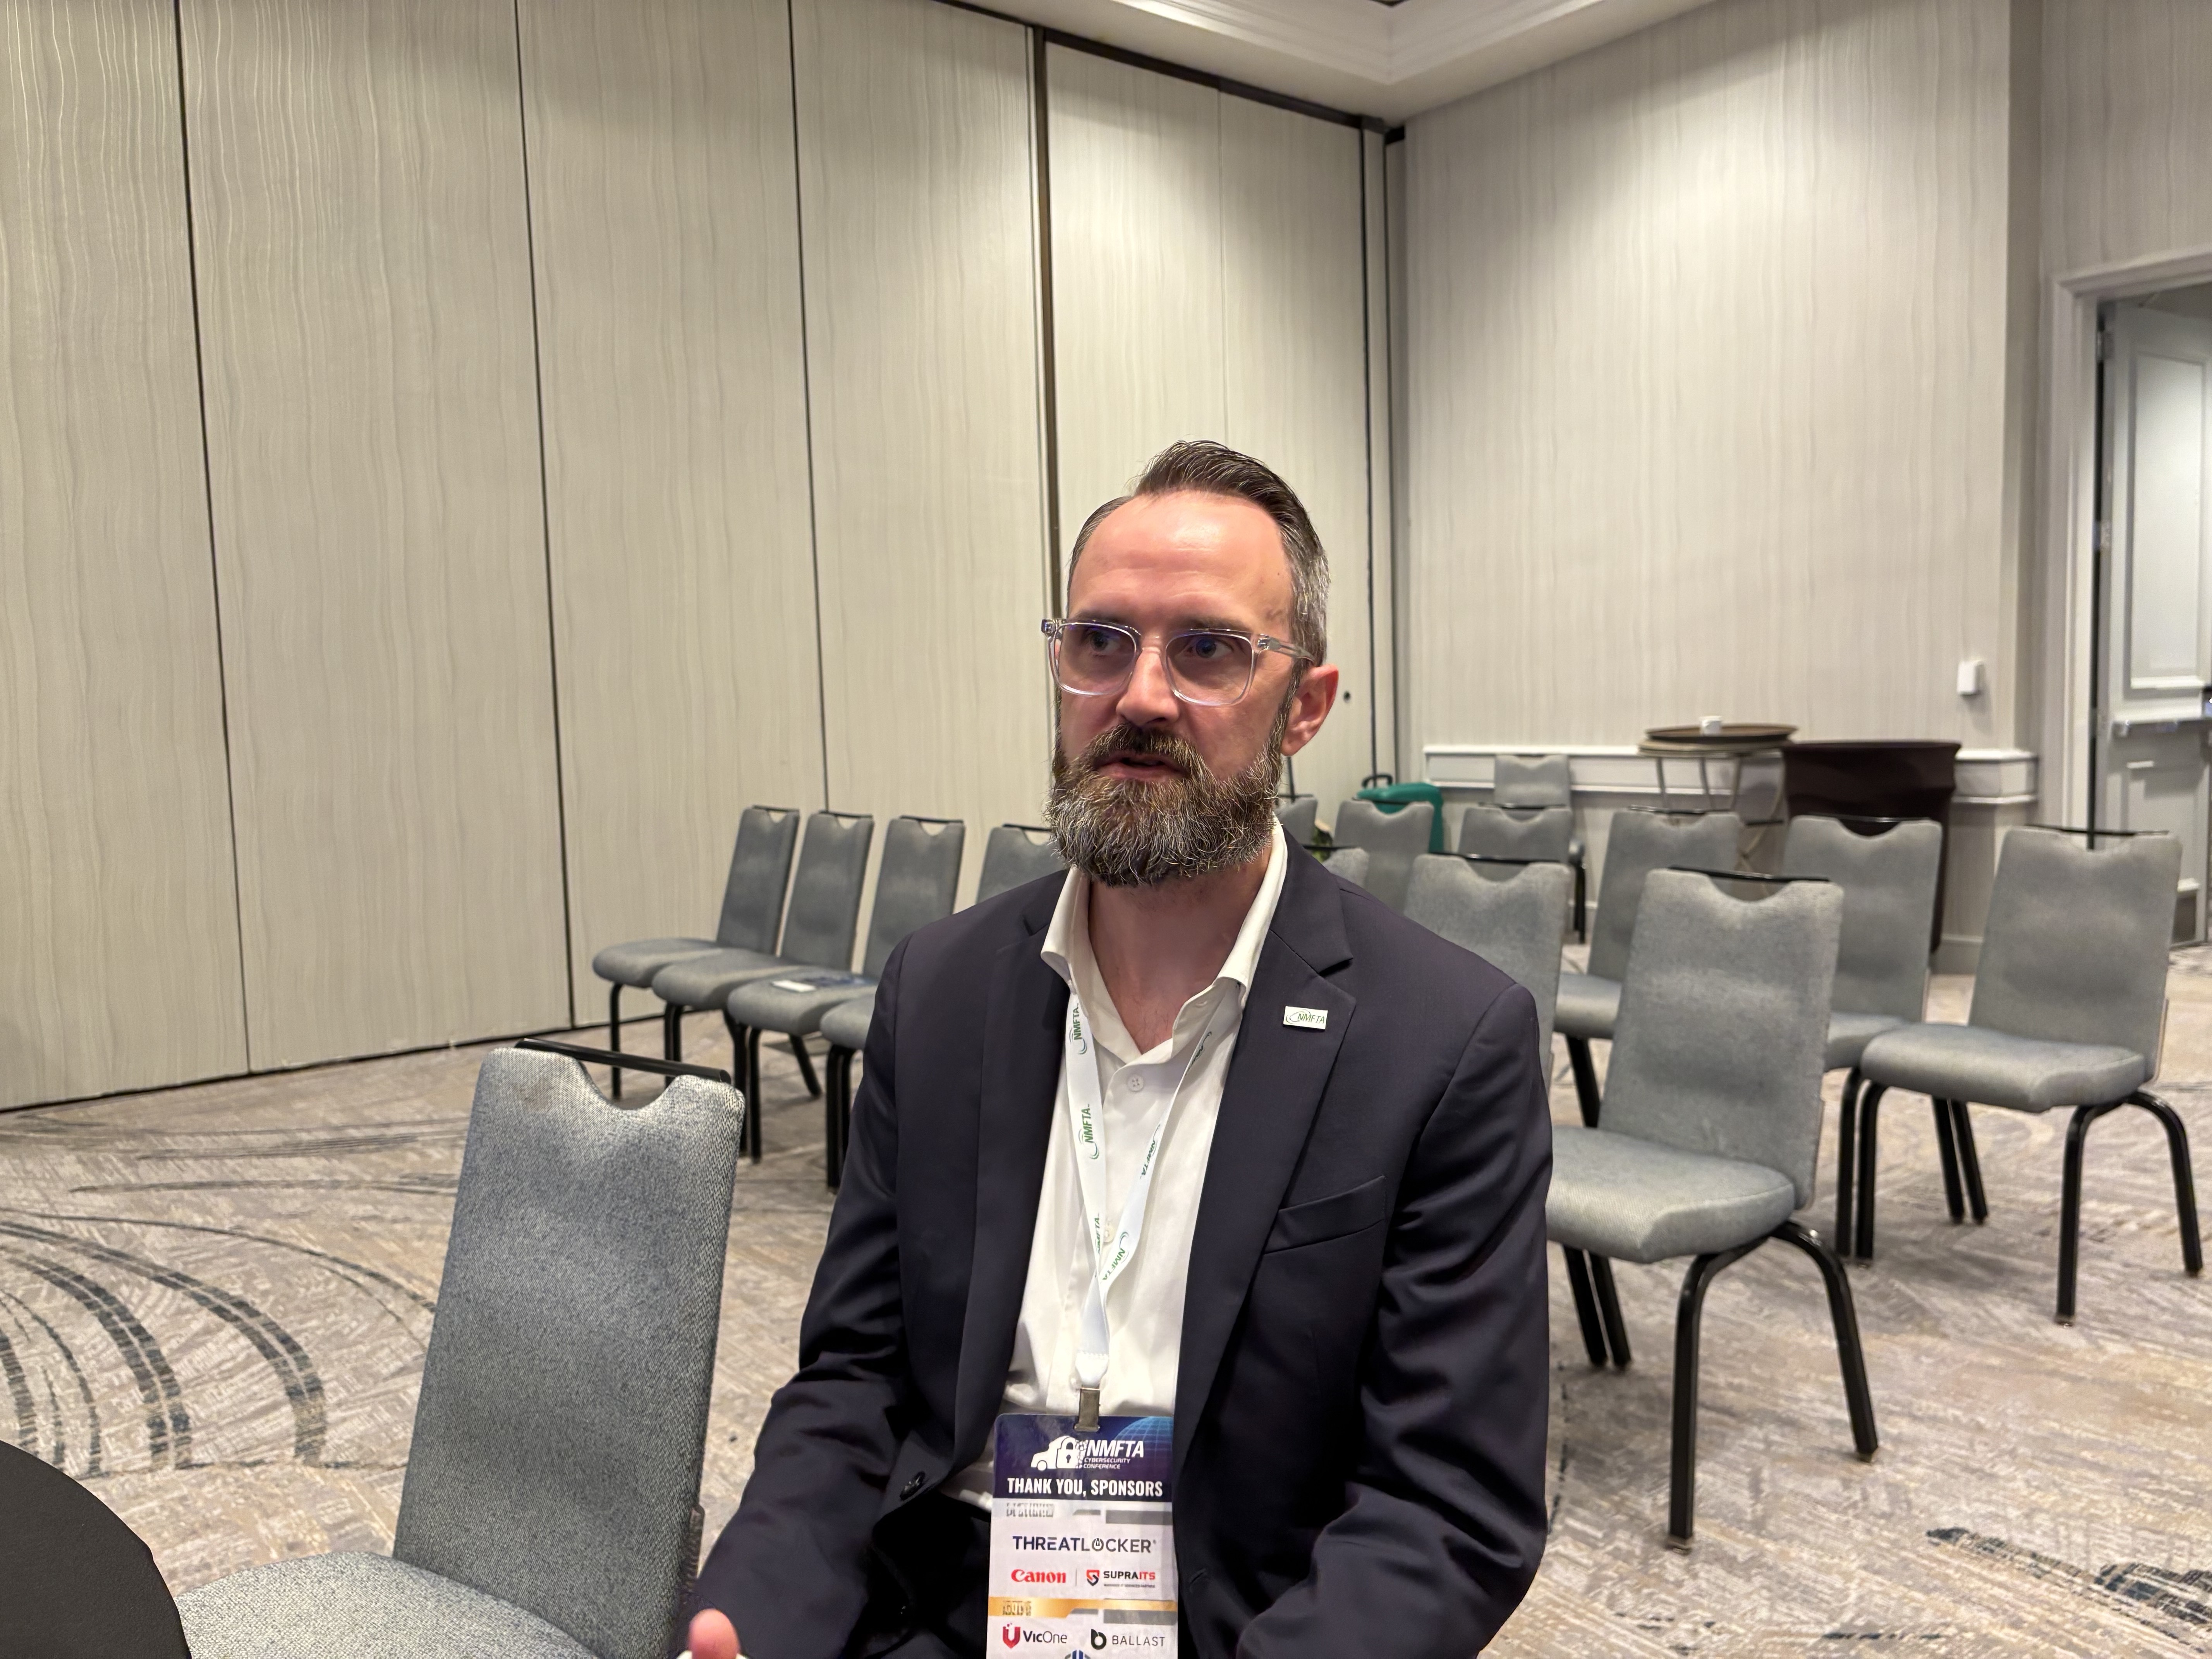
Ben Wilkens is the director of cybersecurity at NMFTA and steered the launch of the portal in May. That was a soft start, but the portal is now fully operational. It is open to anybody who registers.
Wilkens, in an interview on the sidelines of the NMFTA conference, said the group would like to see more volume.
Nobody will kow your name
He also wanted to stress the anonymous nature of the threats that are posted in the portal.
Wilkens used two abbreviations to describe what the portal is looking for: TTP, for Tactics, Techniques, and Procedures, and IOC for Indicator of Compromise. Microsoft has described the latter as “evidence that someone may have breached an organization’s network or endpoint.”
Some of the evidence that a “threat actor” might be behind activity, Wilkens said, could be “file hashes and things like that, specific IP addresses, things that can be used in a detection method.”
Sharing that playbook is seen as the defense against future attacks, according to Wilkens.
The anonymous nature of the portal deals with an issue that came up from the beginning. “One of the concerns we had is that we didn’t want people to feel like they’re kind of exposing themselves to, hey, this happened to our organization,” Wilkens said. The decision to have the information anonymous was made quickly in the process.
Vetting process before publication
Reports that come in a cybersecurity attack are vetted by NMFTA before being published on the portal, Wilkens said.
“We will anonymize them,” Wilkens said. “We strip out all the identifying information. And then as soon as we’ve vetted the incident, we it out with the entire community.”
He likened it to crowd sourcing.
Incidents that are reported through the portal are “never automatically shared out,” Wilkens said. “It’s always reviewed by one of us on the team. We verify, is this legit?”
The review could take as little as an hour but could go on longer, Wilkens said. “We make sure that this informs the community in some meaningful way, and then once we go through those processes, then we can publish.”
The vetting process can be quicker for companies NMFTA knows and has built a relationship with “because we already trust the source,” Wilkens said.
After general discussion of something like the threat portal at the 2025 cybersecurity conference, Wilkens said the staff at NFMTA developed it over the early part of the first months of the year. In the second quarter, he said, NMFTA conducted what he described as a “small beta test with a core group of those carriers who were involved in the conversation,” with the test revealing “tweaks” that needed to be made.
The full portal was released to the public in May.
Numbers are solid so far
There were 100 registrants to the portal by early June. “We were already good,” Wilkens said. “We have a really interesting range. We have some of the biggest shippers and 3PLs, both domestically and internationally. So we’re getting a lot of traction.” Wilkens added that some of the registrants include small carriers.
The dilemma is not surprising. “Polling people, they want to get the information, but the problem is getting people to their information back in to the portal,” Wilkens said. He described the current stream of information as “regular, but we would like to see a higher number.”
“We all focus on building the walls around our organization to protect ourselves and really understanding the security aspect,” Wilkens said, in what could almost be described as a mission statement for the portal. “What we need to also think is what’s happening outside that wall? What’s happening in our neighbor’s environment that’s either successful or that they’ve defended against? And sharing these near misses is equally as important as sharing the incidents that are successful, because the carrier or the broker may not have the same defenses in place, and so that technique that failed in your organization may actually work elsewhere.”
More articles by John Kingston
FMCSA’s Elison: ‘weeks’ away from fixing Motus user experience
Daimler Truck: concerned using cash to avoid new NoX rules
For transportation cybersecurity, AI isn’t helping fight..so far
Brokerage Compliance Symposium
The day before F3. Every compliance issue you face - fraud exposure, carrier liability, FMCSA rules, cargo theft, insurance gaps - navigated by attorneys and operators defining best practices in a changing industry.
The night before F3. FreightTech100 companies honored. FreightTech 25 and Shipper of Choice winners revealed live. Cocktail reception into dinner and live music - 300 industry leaders in one purpose-built room.
F3: Future of Freight Festival
Industry-defining keynotes, rapid-fire technology demos, and industry leaders networking in experiences across Chattanooga - plus the inaugural F3 Awards Dinner featuring the FreightTech and Shipper of Choice reveals.
The day before F3. Every compliance issue you face - fraud exposure, carrier liability, FMCSA rules, cargo theft, insurance gaps - navigated by attorneys and operators defining best practices in a changing industry.
The night before F3. FreightTech100 companies honored. FreightTech 25 and Shipper of Choice winners revealed live. Cocktail reception into dinner and live music - 300 industry leaders in one purpose-built room.
Industry-defining keynotes, rapid-fire technology demos, and industry leaders networking in experiences across Chattanooga - plus the inaugural F3 Awards Dinner featuring the FreightTech and Shipper of Choice reveals.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
