 Back Gbhackers
Hackers Use SEO Poisoning to Infect 1,000 WordPress Sites With Gootloader Malware
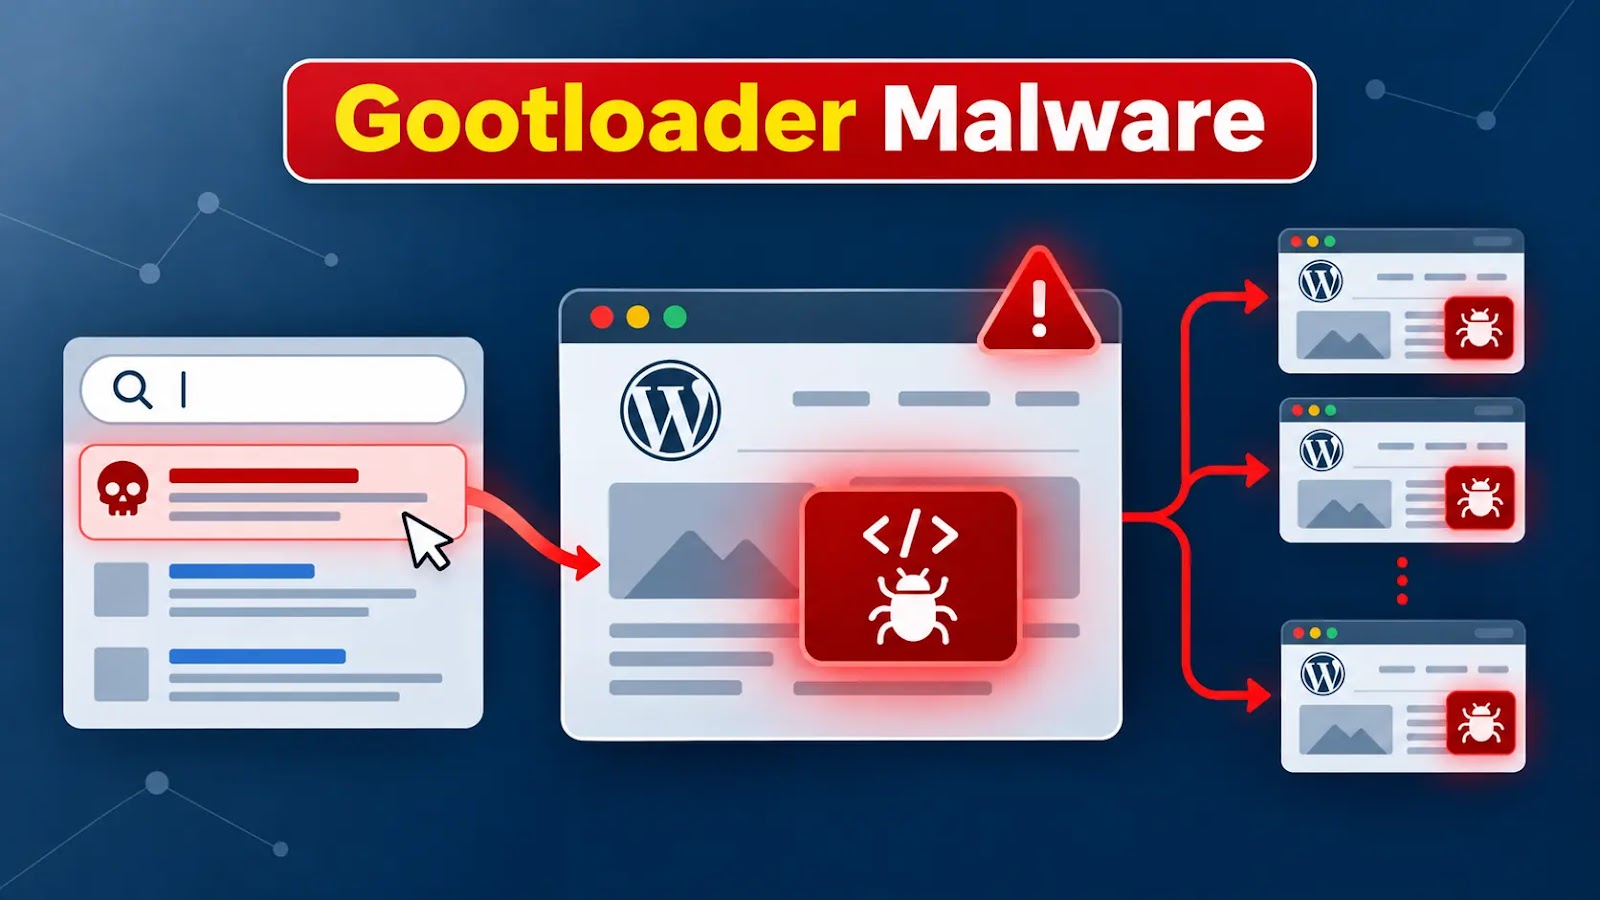
Cybercriminals behind Gootloader have compromised more than 1,000 WordPress websites and operated 216 administrator-controlled domains.
The supplied advisory links the operation to over $28 million in ransomware payments and describes sustained targeting of legal professionals through manipulated results.
SEO poisoning attracts potential victims; it is not the mechanism used to compromise the websites initially. Stolen credentials and exposed WordPress components underpin that infrastructure.
Gootloader operators target narrowly defined searches with limited competition, including jurisdiction-specific contract clauses and business agreements.
Hidden keyword links, injected posts, and coordinated backlinks push compromised pages alongside legitimate resources, increasing the likelihood that professionals encounter malicious downloads during routine research.
The advisory identifies attorneys, in-house counsel, litigation teams, privacy specialists, and legal technology decision-makers as targets.
Traffic distribution infrastructure filters visitors by country, referrer, cookies, and IP address, selectively exposing malicious content rather than showing identical pages to every visitor.
Sophos research explains how these pages simulate forum conversations matching a visitor’s . A fabricated administrator supplies a download link, while another fictional participant endorses the response.
The supposed document arrives as a ZIP archive containing the first-stage JavaScript payload.
This distinction matters operationally: a compromised website functions as delivery infrastructure, while the downloaded script establishes access to the visitor’s Windows environment.
Gootloader Malware Attack
A high ranking and an otherwise legitimate domain therefore provide no assurance that the offered file is trustworthy.
The campaign combines two distinct compromises: attackers first breach WordPress websites, then exploit their visibility to deliver malware to visitors. ic3 said .
The FBI document traces Gootloader’s evolution from ZIP-delivered JavaScript and Windows Script Host execution to AppData staging, scheduled tasks, PowerShell, and registry-resident payloads.
Its recent activity adds WordPress -path abuse, geofencing, and increasingly selective traffic distribution.
Once executed, the loader can establish the foothold required for additional malware and hands-on intrusion activity.
IBM X-Force’s GootBot investigation previously documented compromised WordPress sites serving command-and-control infrastructure and PowerShell implants spreading across enterprise environments.
IBM tracks the associated group as Hive0127, also known as UNC2565.
The FLASH also maps observed activity to credential theft, Kerberoasting, process injection, defense impairment, and lateral movement through SMB, WMI, and WinRM.
These mappings describe broader intrusion capabilities, rather than proving that every Gootloader infection progresses through every listed technique.
The warning follows a Justice Department disruption announcement on November 12. Authorities reported removing Gootloader malware from over 100 servers and seizing delivery and control domains.
DOJ separately attributed at least 25,000 computer infections worldwide and approximately $28.8 million in losses across at least 44 American ransomware victims to the operation.
For Windows environments, the supplied advisory prioritizes restricting Windows Script Host where unnecessary, enforcing application controls, and blocking unauthorized execution from user-writable directories.
Investigators should correlate PowerShell events 4103 and 4104 with process creation, scheduled tasks, DNS, proxy, and endpoint telemetry.
WordPress administrators should patch components, remove unused plugins, enforce strong administrative authentication, restrict unnecessary XML-RPC access, and monitor unexpected file or REST endpoint changes.
If malicious JavaScript executes, the advisory recommends network isolation and evidence preservation. Confirmed persistence, credential theft, or follow-on malware warrants reimaging; deleting the original archive alone does not restore trust.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC .
Artificial Intelligence
Cyber security Course
Cyber Security Resources
Cybersecurity
Information Gathering
Information Security Risks
11 Penetration Testing Companies: The 2026 Buyer’s Verdict Guide
11 Attack Path Management Tools: The 2026 Buyer’s Verdict Guide
11 Cyber Asset Attack Surface Management (CAASM) Tools: The 2026 Buyer’s Verdict Guide
11 Attack Surface Management (ASM/EASM) Tools: The 2026 Buyer’s Verdict Guide
11 Continuous Threat Exposure Management (CTEM) Platforms: The 2026 Buyer’s Verdict Guide
ARTEX AI Framework Linked to 44-Hour Barracuda Cloud Attack Targeting Credentials and Crypto Wallets
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
