 Back Infostealers
Introducing Cavalier's New Threat Feeds: Comprehensive Visibility into Attacker Infrastructure
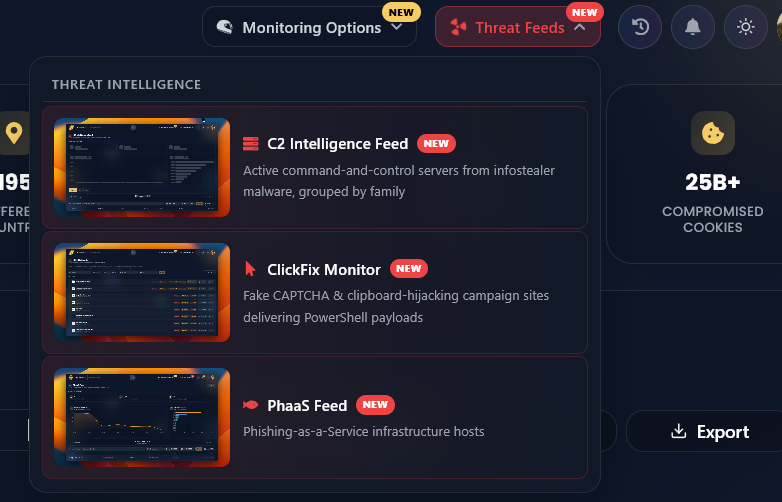
We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data , ClickFix , and PhaaS (Phishing-as-a-service) . Together, they give security teams comprehensive visibility into active attacker infrastructure – from infostealer command-and-control (C2) servers to malicious ClickFix pages executing clipboard injection, to turnkey Phishing-as-a-service (PhaaS) kits targeting corporate credentials.
🛡️ Infostealers C2 Monitoring | 🖱️ ClickFix Server Monitoring | 🎣 Phishing-as-a-Service (PhaaS)
The new C2 Data module provides unprecedented access to observed command-and-control (C2) hosts associated directly with active infostealer campaigns. This empowers security teams to transition from reactive incident response to preemptive blocking.
Inside Cavalier, you can seamlessly review:
One of the most powerful features of the C2 Intelligence Feed is the integration of Infostealer credential telemetry linked to the hosting platform . This shows compromised employee or user credentials that likely enabled the threat actors to gain initial access to the server in the first place.
For example, you can open a host such as myrtler(.)biz and immediately see that it’s associated with the Vidar malware family, along with its DNS activity, first-seen date, and critical infrastructure details as they are actively observed.
To truly block active command-and-control channels at the firewall or proxy level – stopping infected endpoints from exfiltrating credentials, receiving instructions, or dropping secondary payloads – automation is key.
All C2 datasets are fully accessible via REST API endpoints for seamless integration into your existing security stack. Using the GET /json/v3/threat-feeds/c2 endpoint, teams can retrieve observed infostealer C2 hosts with granular filters for host, malware family, country, ASN, feed type, date, and pagination.
The new ClickFix module provides critical visibility into malicious websites that use fake verification pages, CAPTCHA prompts, and clipboard injection techniques to trick users into executing malicious commands.
Inside Cavalier, you can seamlessly review:
With ClickFix lures becoming increasingly sophisticated, it is vital to understand the exact mechanisms threat actors are using to deceive employees. Cavalier allows you to investigate flagged sites, view the copied commands presented to victims, and examine visual evidence of the attack.
Perhaps the most powerful capability of the ClickFix monitor is its integration with Infostealer credential telemetry linked to the hosting platform . This pinpoints compromised employee or user credentials that enabled attackers to gain initial access to the server, explaining how a legitimate business domain became a host for malware.
We’ve previously documented how legitimate businesses turn into malware hosts , and a recent high-profile example perfectly illustrates this pipeline.
In our recent shared research on how an infostealer infection led to a sophisticated ClickFix campaign at Artlist , we traced the root cause of a compromised Artlist subdomain back to an infostealer infection from August 2023. A freelance developer unwittingly downloaded a pirated copy of Adobe Acrobat PRO DC, infecting their machine. This breach exposed highly privileged WordPress credentials belonging to a Senior Content Executive. Armed with valid, high-privilege access, threat actors were able to inject an advanced EtherHiding script into the blog, which dynamically routed visitors to a ClickFix payload.
With Cavalier’s new Threat Feeds, security teams can now instantly monitor these high-value, trusted domains that have been repurposed by threat actors. This capability pinpoints exactly where they are serving ClickFix prompts and simultaneously reveals the compromised credentials that facilitated the takeover.
All datasets are fully accessible via REST API endpoints. Teams can utilize the GET /json/v3/threat-feeds/clickfix endpoint to retrieve detected sites, including domains, URLs, malicious indicators, clipboard activity, CAPTCHA detection, and screenshot evidence, or use the GET /json/v3/threat-feeds/clickfix/{domain} endpoint for specific record lookups.
As Phishing-as-a-Service (PhaaS) platforms become extremely prominent in high-profile corporate hacks, giving lower-tier actors turnkey access to advanced credential harvesting tools, preemptive visibility is more critical than ever. The new PhaaS Threat Feed is unique to Hudson Rock , providing an unparalleled view into active phishing host networks before they are deployed in targeted spear-phishing campaigns against your workforce.
Inside Cavalier, security teams can seamlessly review:
Cavalier groups PhaaS hosts by their specific operational kits, allowing defenders to understand the exact tactics they are facing. Our intelligence tracks massive networks running well-known platforms like Eviltokens and Kali365 , as well as exclusive, recently uncovered campaigns like SessionSerpent —intelligence you will only find surfaced through Hudson Rock.
The PhaaS feed allows you to go beyond the domain level and map out the entire operational footprint of an attacker. For example, you can surface surface infrastructure like garage-door-repair(.)cyou running Eviltokens, or pinpoint specific IP nodes like 43.172.6.35 tied to Kali365 operations.
Crucially, just like our ClickFix and C2 modules, the PhaaS feed integrates directly with our infostealer telemetry. This allows you to instantly see if a host domain (e.g., webcindario(.)com ) has compromised employee credentials tied to it, revealing exactly how attackers gained initial control of the server to host their phishing infrastructure.
All datasets are fully accessible via REST API endpoints for automated ingestion into your SIEM or SOAR. Teams can utilize the GET /json/v3/threat-feeds/phaas endpoint to retrieve active Phishing-as-a-Service indicators with flexible filtering, or use the GET /json/v3/threat-feeds/phaas/{host} endpoint for specific host network lookups and operational status checks.
With our new Threat Feeds, cybersecurity teams can monitor live C2 infrastructure from infostealer campaigns, ClickFix networks, and PhaaS (Phishing-as-a-service) operations to proactively block malicious communications.
We also provide access to various free cybercrime intelligence tools that you can find here:
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
