 Infostealers
Cavalier Launches Threat Feeds for Infostealer Campaign Monitoring
Article Content

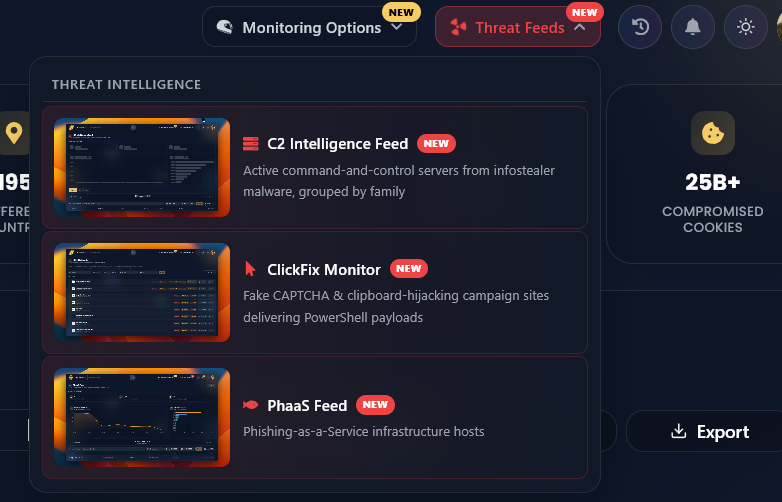
- •Cavalier launched new Threat Feed modules for monitoring infostealer activities.
- •The C2 Data module allows access to active infostealer command-and-control servers.
- •ClickFix identifies malicious sites using clipboard injection techniques.
Cavalier has introduced three new Threat Feed modules: C2 Data, ClickFix, and PhaaS, aimed at enhancing visibility into infostealer operations. The C2 Data module provides access to command-and-control (C2) servers linked to active infostealer campaigns, enabling preemptive blocking. The ClickFix module monitors malicious websites that utilize clipboard injection and fake verification pages to deceive users. These tools integrate Infostealer credential telemetry, revealing compromised credentials that facilitated initial access. Security teams can utilize REST API endpoints for seamless integration into existing security infrastructures. This development is critical as infostealer campaigns become increasingly sophisticated, targeting corporate credentials through various attack vectors.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track ClickFix and Artlist in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Active Exploitation of Siemens Software Center Vulnerability in ClickFix Campaign Siemens has confirmed that a DLL side-loading vulnerability (CVE-2026-110936) in Siemens Software Center is actively being exploited in malware attacks. The vulnerability allows attackers to execute malicious code by placing a specially crafted DLL in a directory searched by the application. Siemens first disclosed…
 ClickFix Technique Surges with AI Lures in Cyber Attacks ClickFix has emerged as a dominant cyber attack technique since 2024, now accounting for over 52% of Push's detections. This method has evolved to include sub-techniques like InstallFix and ConsentFix, with attackers increasingly using AI tools as bait. In Q2 2026, ClickFix detections reached 67%, surpassing other…