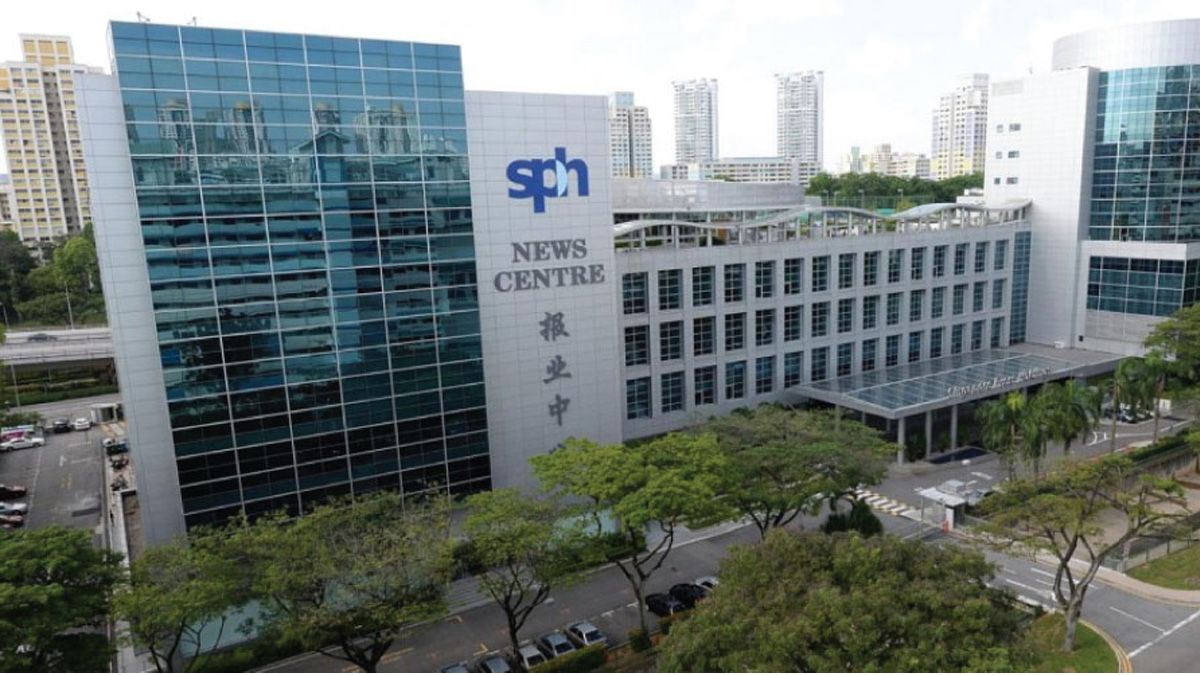
SINGAPORE: SPH Media said on 10 November 2026 that it had been hit by a series of cyberattacks that affected nine per cent of its database.
The media company, which publishes titles including The Straits Times, The Business Times and Lianhe Zaobao, said the exposed information was mostly e-mail addresses, along with some names, mailing addresses and phone numbers.
No payment card details, financial or banking information, or customer accounts were compromised, it added.
SPH Media detects five intrusions believed to be linked to one actor
In a statement, SPH Media said it had identified cyberattacks on five of its systems, which it believed were “a concerted effort that was carried out by the same threat actor”.
The first incident was detected on 4 November and the most recent on 8 November.
Based on preliminary investigations, the company said it suspects the intrusions could have been artificial intelligence (AI)-enabled attacks.
Its spokesman said the breaches arose from a combination of factors, including software bugs and system configuration.
The company did not say how many individuals were affected, and it did not identify the threat actor.
No corporate customers’ information was affected. However, some e-mail addresses belonging to SPH Media employees were compromised, and the affected staff have been told to remain vigilant and exercise caution, the company said.
Breach reported to regulators as company patches bugs and configurations
SPH Media said that when it discovered the incidents, it immediately took steps to secure the affected systems. It also engaged external cybersecurity experts to investigate and contain the breaches.
The organisation reported the incidents to the Personal Data Protection Commission (PDPC), the Cyber Security Agency of Singapore (CSA) and the Infocomm Media Development Authority (IMDA). It also filed a police report.
SPH Media said it has since applied bug fixes to its IT systems and updated its system configurations.
It has also updated its perimeter defences to block further probing and exploitation attempts by the attackers, and has heightened its monitoring posture.
“SPH Media takes the security and confidentiality of customers’ information very seriously, and has been working very closely with the relevant authorities and third-party specialists,” said the spokesman.
Customers urged to stay vigilant against suspicious e-mails and calls
The company asked customers to be wary of unsolicited that could make use of the exposed details.
“We advise customers to remain vigilant and exercise caution for suspicious and unsolicited e-mails, messages and calls, particularly those requesting personal information, passwords or payments, and to avoid clicking on suspicious links or attachments,” the spokesman said.
“We remain committed to safeguarding our systems and the information entrusted to us,” the spokesman added.
Breach follows spate of data incidents disclosed in Singapore this month
SPH Media’s disclosure follows a series of data breaches made public in Singapore within a single week in early November.
On 3 November, Singapore Airlines (SIA) said 46,000 booking records had been accessed in a breach at its reservation technology provider, Amadeus.
On the same day, finance platform MoneySmart told customers that data on users in Singapore and Hong Kong had been copied from its systems. It had detected unauthorised access on 29 October.
On 6 November, telecommunications company M1 said customers’ names, identity card details and information had been compromised in a breach on 30 October.
That evening, telemedicine provider Doctor Anywhere said it had learnt on 29 October of a breach that exposed users’ identity, passport and bank account details.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
