 Pasqualepillitteri.It
Arcadia Disaster Alert System Hacked for Phishing Attack
Article Content

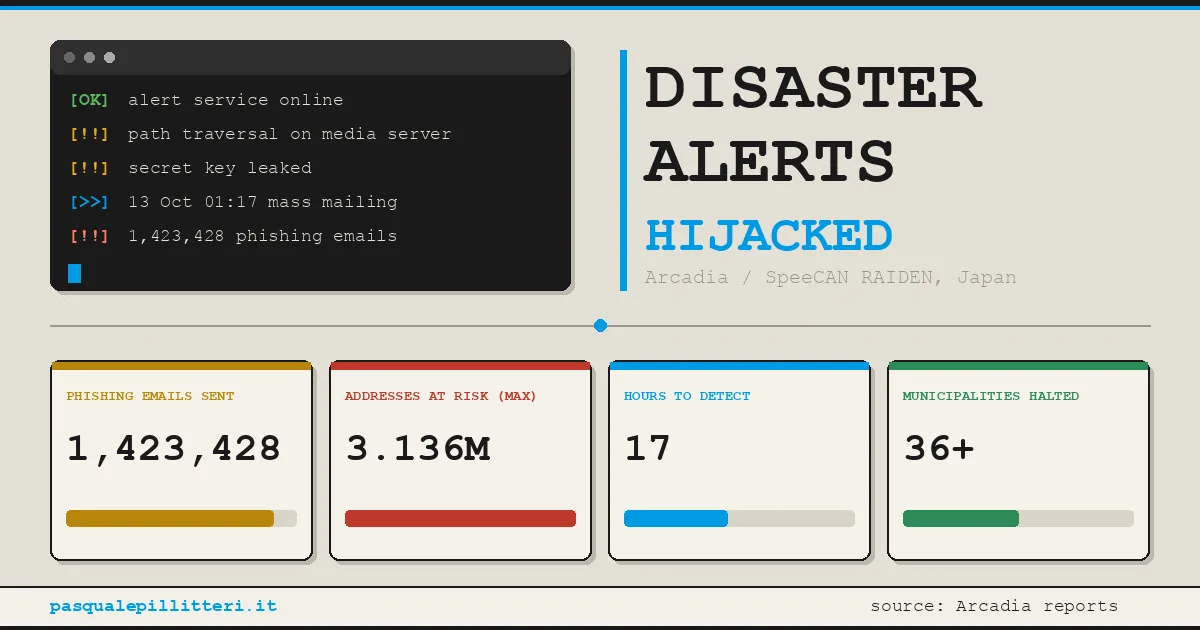
- •1.42 million phishing emails sent using Arcadia's compromised disaster alert service.
- •Approximately 3.13 million email addresses may have been exposed in the breach.
- •Osaka police are investigating potential violations of Japan's Unauthorized Access Prohibition Act.
On October 11, 2026, hackers breached Arcadia's disaster alert service, which is used by 875 public organizations in Japan. They exploited a directory path traversal vulnerability to gain access and sent 1.42 million phishing emails within hours. The attack may have exposed approximately 3.13 million email addresses, including sensitive data from emergency services. Arcadia's president noted the attack's scale suggested possible AI involvement. The Osaka police are investigating the breach, which has disrupted disaster alert services. The incident has raised concerns about public trust in emergency communication systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track JR East in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What organizations are affected?
How did the attackers gain access?
What actions are being taken in response?
Continue Reading
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…
 Vulnerability in OpenEMR Enables Remote Code Execution A vulnerability (CVE-2026-124450) has been identified in OpenEMR versions prior to 8.3.0, specifically within the fax/sms module. The flaw involves broken access control and path traversal through an unvalidated file_path parameter. This allows authenticated low-privilege users to read sensitive files, such as…