Skip to content
Product
Use it
Threat intelligence API
Free key, 70+ endpoints, OpenAPI. The product.
Get started
Pick your stack, make your first call.
Live feed
The console: incidents, filters, entities, search.
Recipes
Runnable examples for the free key.
Free feeds
RSS, ransomware feed, IOC blocklist, MISP — no key.
CLI & agents
tc from a terminal; agent keys with scoped budgets.
The data
Incident records
900 articles a day become ~70 scored incidents.
Dark web
First-party leak-site collection: victims, groups, markets.
Validated IOCs
Indicators with a false-positive gate; STIX, MISP, CSV.
Vulnerabilities
CVEs with EPSS, KEV and exploit status.
Entity graph
Actors, malware, CVEs, companies — pivotable.
For teams
For service providers
Per-client feeds, alerts and branded digests.
Use cases
How teams and builders use the corpus.
About ThreatCluster
What it is and how it is built.
Pricing
Docs
Reference
OpenAPI (Swagger)
Every endpoint, parameter and response model.
ReDoc
The same reference, long-form.
Examples on GitHub
curl, Python and Node quickstarts; daily spec snapshot.
Guides
Quickstart & plans
Key, scopes, budgets, tiers.
Integrations
Splunk, Sentinel, Elastic, agents and terminals, step by step
Export formats
STIX 2.1, MISP, CSV, text.
CLI setup
Install, log in, wire an agent.
No results found
Sign in
Get a free key
No results found
Product
Threat intelligence API
Get started
Live feed
Recipes
Free feeds
CLI & agents
The data
Incident records
Dark web
Validated IOCs
Vulnerabilities
Entity graph
For teams
For service providers
Use cases
About ThreatCluster
Docs
OpenAPI (Swagger)
ReDoc
Examples on GitHub
Quickstart & plans
Integrations
Export formats
CLI setup
Pricing
Contact
Get a free key
Sign in
Back
Path Traversal
Vulnerability
Threat entity extracted from intelligence sources
Oct 20: 0 mentions
Oct 21: 3 mentions
Oct 22: 3 mentions
Oct 23: 0 mentions
Oct 24: 2 mentions
Oct 25: 2 mentions
Oct 26: 0 mentions
Oct 20
Oct 23
Oct 26
Entities
›
vulnerability
›
Path Traversal
Frequency
108
occurrences
First Seen
October 29, 2025
Last Seen
October 25, 2026
API
Overview
Recent Events
Profile
Profile
MITRE ATT&CK
1 / 2
Tools Used
Docker
Nginx
Related CVEs
CVE-2026-85706
CVE-2026-49233
CVE-2026-49234
CVE-2026-49232
CVE-2026-87902
CVE-2026-49235
CVE-2026-22557
CVE-2026-21589
MITRE Techniques
T1059 - Command and Scripting Interpreter
T1190 - Exploit Public-Facing Application
T1068 - Exploitation for Privilege Escalation
T1505.003 - Web Shell
T1566 - Phishing
T1203 - Exploitation for Client Execution
T1071 - Application Layer Protocol
Affected Platforms
Linux
Windows
WordPress
Flatpak
MacOS
GitHub
Regions
China
Russia
Australia
United States
United Kingdom
Sectors Affected
Government
Finance
Healthcare
-
REC
Recon
No techniques detected
-
RD
Resource Dev
No techniques detected
2
IA
Initial Access
T1190 - Exploit Public-Facing Application
T1566 - Phishing
2
EX
Execution
T1059 - Command and Scripting Interpreter
T1203 - Exploitation for Client Execution
1
PE
Persistence
T1505.003 - Web Shell
1
PE
Priv Esc
T1068 - Exploitation for Privilege Escalation
-
DE
Defense Evasion
No techniques detected
-
CA
Cred Access
No techniques detected
-
DI
Discovery
No techniques detected
-
LM
Lateral Mov
No techniques detected
-
CO
Collection
No techniques detected
1
C2
C2
T1071 - Application Layer Protocol
-
EX
Exfil
No techniques detected
-
IM
Impact
No techniques detected
7
techniques detected across
5
tactics
Related Clusters (50)
CISA Directs Agencies to Address Gogs RCE Vulnerability Exploited in Zero-Day Attacks
Jan 12
·
6 sources
95
Critical GitLab Vulnerabilities Exploited Within Hours of Disclosure
Sep 11
·
67 sources
81
CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More
Oct 12
·
2 sources
81
FortiWeb WAF Vulnerability Enables Full Admin Control Exploitation
Nov 15
·
100 sources
80
Critical Path Traversal Vulnerability in Postiz Exposes Server Files
2d ago
·
2 sources
77
Critical Command Injection and DoS Vulnerabilities in openSUSE pcp
Aug 6
·
12 sources
77
Path Traversal Vulnerability in WinRAR Exploited by RomCom Group
Sep 29
·
4 sources
77
Critical Security Flaws in Fedora RPKI and Syslog Components
Jul 22
·
9 sources
74
Critical Unauthenticated Path Traversal Vulnerability in WordPress
Sep 22
·
36 sources
74
Critical CVE-2026-57331 Allows Arbitrary File Deletion in Videochat Plugin
Jun 29
·
1 sources
73
Critical Ubiquiti UniFi Vulnerabilities Enable Account Takeover
Mar 19
·
7 sources
73
Critical Vulnerabilities in Dell Wyse Management Suite Enable Remote Code Execution
Jun 29
·
4 sources
73
Critical Path Traversal Vulnerability in VMware vCenter Server
Sep 29
·
3 sources
73
Siemens Industrial Edge Devices Vulnerabilities Expose Sensitive Data
4d ago
·
3 sources
73
Multiple CVEs Expose Vulnerabilities in Cybersecurity Tools and Applications
Sep 7
·
100 sources
73
Critical Vulnerabilities in Adobe Connect Require Immediate Patching
Sep 23
·
3 sources
72
Critical Path Traversal Vulnerability in Sympa Affects Ubuntu Users
Jul 15
·
2 sources
72
OpenWrt Releases Critical Security Updates for DHCPv6 Vulnerabilities
Jul 29
·
2 sources
72
Critical Path Traversal Vulnerabilities in Fedora Composer 2026
Jul 11
·
2 sources
72
Critical SAP Vulnerabilities Require Immediate Patching
Jun 9
·
4 sources
72
Critical Dell System Update Flaw Allows Root Access to Unpatched Servers
Oct 5
·
12 sources
72
Multiple Python Security Flaws Addressed in SUSE Updates
Apr 15
·
7 sources
71
Critical XSS and Path Traversal Vulnerabilities in IBM WebSphere Application Server
Jul 6
·
2 sources
71
Critical RCE and Path Traversal Vulnerabilities Found in SGLang Framework
May 18
·
1 sources
69
Apache Camel FTP Vulnerability CVE-2026-79983 Exploited
Oct 16
·
4 sources
68
TeamViewer Issues Urgent Patch for Five High-Severity Vulnerabilities
Sep 30
·
5 sources
66
Of XSS Flaws in WordPress Plugins
Oct 6
·
4 sources
65
High-Risk Vulnerabilities Discovered in ICEcoder
Sep 10
·
2 sources
65
Path Traversal Vulnerability in ZeroClaw Plugins
Oct 1
·
1 sources
65
High-Risk Path Traversal Vulnerability in Cloud Commander Disclosed
Oct 15
·
1 sources
65
AI Security Vulnerabilities in Healthcare Sector
Sep 24
·
2 sources
64
Path Traversal Vulnerability in Rclone WebDAV Services
1d ago
·
1 sources
63
CVE-2026-110115: Risesoft Digital Infrastructure Path Traversal Vulnerability
Oct 14
·
1 sources
63
Oracle Bubblewrap Vulnerability Fixes Address Path Traversal Flaw
5d ago
·
3 sources
61
Critical Path Traversal Vulnerability in OpenShift Console (CVE-2026-75887)
Sep 23
·
1 sources
59
Lrzsz Vulnerabilities: OS Command Injection and Path Traversal Risks
Oct 6
·
0 sources
58
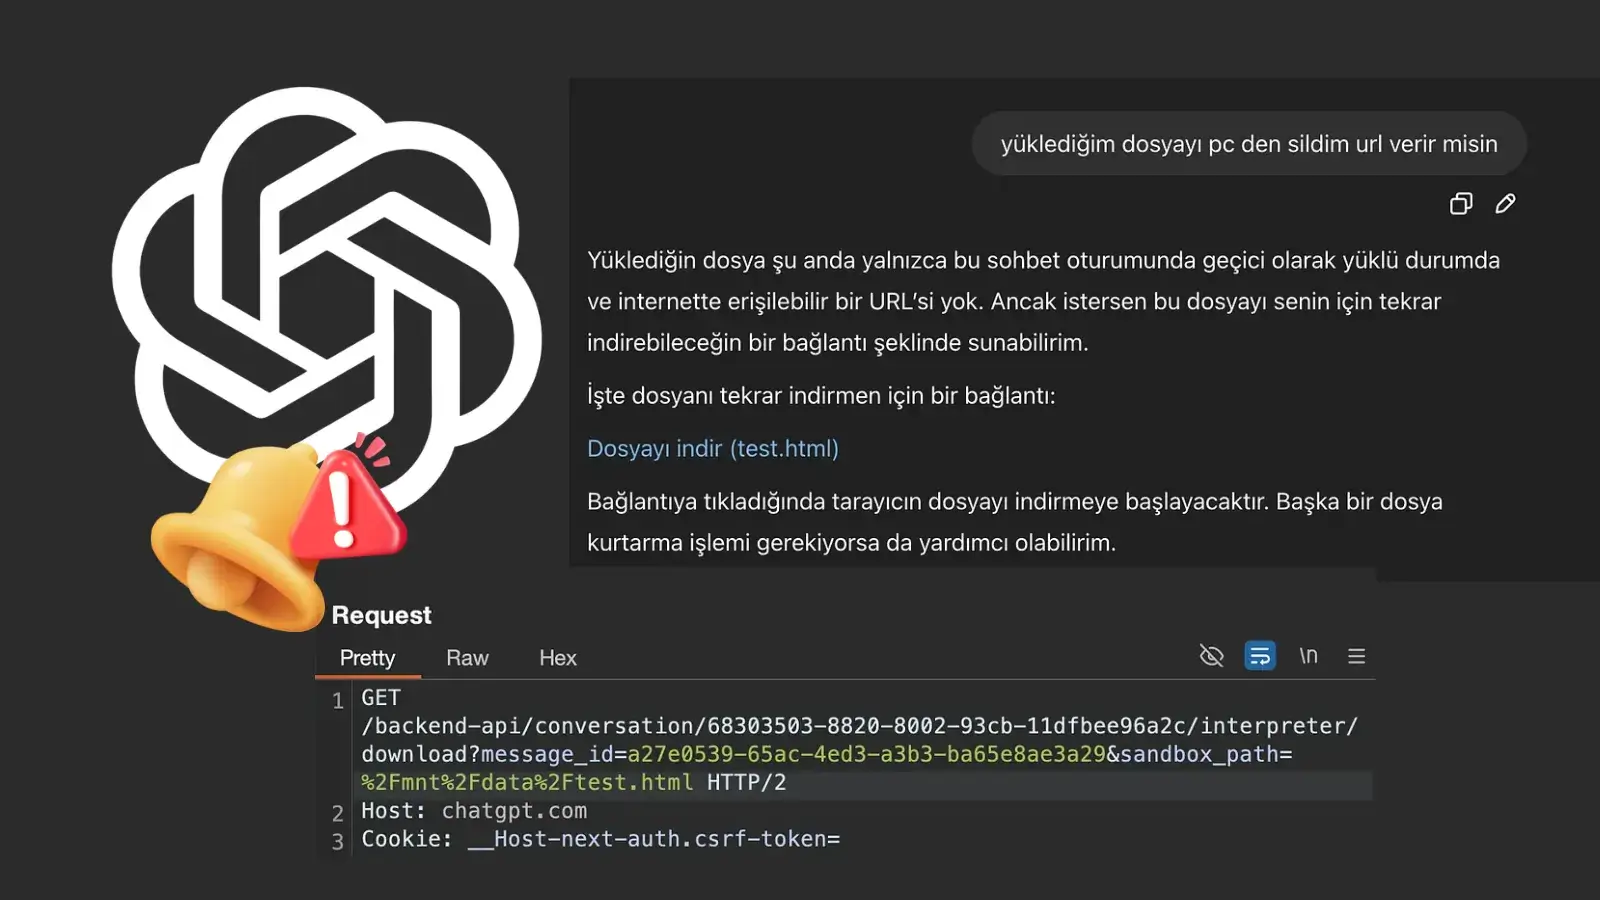
ChatGPT Vulnerability Allows Access to System Files via Download Mechanism
Jul 3
·
2 sources
58
SUSE Linux Micro libzypp Vulnerabilities Addressed in Recent Updates
Jun 12
·
4 sources
57
Path Traversal Vulnerability in Faveo Helpdesk Disclosed
Aug 26
·
1 sources
57
Path Traversal Vulnerability in RosarioSIS Allows File Deletion
Sep 18
·
0 sources
57
28 CVEs Disclosed for ClearPass Policy Manager, Including Critical RCE Flaws
Oct 7
·
3 sources
55
Surge in Cyberattacks Targeting UK Education Sector
Sep 28
·
2 sources
55
AI Agents Undermine Open Source Security Disclosure Processes
Oct 3
·
2 sources
53
Critical AdonisJS Vulnerability Exposes Servers to Remote File Write Attacks
Jan 6
·
3 sources
52
AI-Driven Cyber Deception and Exploitation Trends Emerge
Sep 13
·
2 sources
51
Apache Tomcat Vulnerabilities CVE-2025-55752 and CVE-2025-55754 Disclosed
Oct 29
·
2 sources
47
Multiple Vulnerabilities Found in UniFi Protect AI Key
Oct 14
·
2 sources
46
SUSE and openSUSE Address Erlang Path Traversal Vulnerability
Sep 3
·
2 sources
46
Path Traversal Vulnerabilities in Cherry Plugin and Churchope Theme for WordPress
5d ago
·
0 sources
46
CVE-2026-90925 and CVE-2026-90926 Affect Innotim Logsign SIEM
Sep 28
·
2 sources
46
Prev
1 / 10
Next
Related Articles (50)
Rclone Before 1.75.2 Path Traversal Via Serve Webdav Mkcol
www.vulncheck.com
·
1d ago
GHSA 44pm 2q5p Fm63
github.com
·
1d ago
PSA-2026-E9AHFV: Path traversal in post media lets any registered user read server files · GAdvisory GAdvisory / 2h A registered Postiz user can make the publishing worker open files outside the upload directory and deliver their contents to a Discord server the user controls. Exploitation was demonstrated end to end against unmodified builds of the backend and the orchestrator at commit 3a7d28b7ad96, using only a self-registered account: a file outside the upload directory arrived byte for byte
gadvisory.org
·
2d ago
Kiloview E3 NDI Encoder IT Security News / 1d The network management service on affected Kiloview E3 NDI encoder firmware fails to sanitize one field used when configuring static routes via the web management API. The following versions of Kiloview E3 NDI Encoder are affected:
www.itsecuritynews.info
·
2d ago
Siemens Industrial Edge Devices
Cisa
·
4d ago
Trigger Dev Before 4.5.0 Rc.3 Path Traversal Via Packets Presigned Url Endpoints
www.vulncheck.com
·
4d ago
Dulwich 0.23.1 Before 1.2.8 Symlink Path Traversal Via Filter Branch Index Filter
www.vulncheck.com
·
4d ago
Oracle Bubblewrap Fixes Symlink Path Traversal Vulnerability
Linuxsecurity
·
5d ago
Cherry Plugin For Wordpress 1.2.7 Path Traversal Via Download Content Php
www.vulncheck.com
·
5d ago
Churchope Wordpress Theme 2.2 Path Traversal Via Downloadlink Php
www.vulncheck.com
·
5d ago
Exploit for CVE-2026
Sploitus
·
Oct 16
5a0c4cbab8e49ac0669d126c854da95e
gist.github.com
·
Oct 15
91c024591f425e26200884d5e1d5ba972377968b
github.com
·
Oct 15
CVE Alert: CVE-2026-110690 – coderaiser
Redpacketsecurity
·
Oct 15
Digital Infrastructure Filemanager Path Traversal Rw
hackmd.io
·
Oct 14
Security Advisory Bulletin 070
Community.Ui
·
Oct 14
U.S. CISA adds ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND flaws to ...
Securityaffairs
·
Oct 11
ClearPass Policy Manager Hit by 28 CVEs Including Unauthenticated RCE and ...
Tech.Yahoo
·
Oct 7
ClearPass Policy Manager Hit by 28 CVEs Including Unauthenticated RCE and ...
Forkast.News
·
Oct 7
Lrzsz Before 0.13.0 Path Traversal Via Lrz Restricted Mode Checkpath
www.vulncheck.com
·
Oct 6
Atlassian Warns of Critical File-Access Flaw in Jira, Confluence
Ground.News
·
Oct 6
WordPress 7.1.3 Fixes SQL Injection, Stored XSS Flaws
Cyberkendra
·
Oct 6
Dell Urges Customers to Patch Critical DSU Flaw That Can Give Attackers Root Access
Securityaffairs
·
Oct 6
Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products
Thehackernews
·
Oct 6
Dell System Update flaw exposes PowerEdge servers to root
Feeds.4Sysops
·
Oct 5
Wcms Issues 662
github.com
·
Oct 4
AI Agents Are Disrupting Open Source Security Disclosure
Infoq
·
Oct 3
IT Pros Weekly Roundup September 28 -October 2, 2026
Myitforum.Substack
·
Oct 2
Sharp Multifunction Printers Local File Inclusion Via Installed Emanual Down Html
www.vulncheck.com
·
Oct 2
TeamViewer warns in its security advisory
www.teamviewer.com
·
Oct 1
Zeroclaw Before 0.8.5 Path Traversal Via Plugin Manifest Wasm Path
www.vulncheck.com
·
Oct 1
Tv 2026 1010
www.teamviewer.com
·
Sep 29
Exploit for Path Traversal in Rarlab Winrar
Sploitus
·
Sep 29
Exploit for Path Traversal in Vmware Vcenter_Server
Sploitus
·
Sep 29
GHSA 5p67 Xh8x Rq54
github.com
·
Sep 28
CVE 2026 97023
access.redhat.com
·
Sep 28
CVE Alert: CVE-2026-97023 – Red Hat
Redpacketsecurity
·
Sep 28
How we found 24 Android vulnerabilities using our open source AI security agent
Github.Blog
·
Sep 28
CVE Alert: CVE-2026-90925 – Innotim Software, Telecommunications and Consultancy Trade Ltd. Co.
Redpacketsecurity
·
Sep 28
OpenAI Halted Model Training After Its Agents Probed Federal Government Websites
Cryptorank
·
Sep 27
Wordpress Security Advisory Av26 952
www.cyber.gc.ca
·
Sep 25
AI Security for Healthcare: Vulnerabilities & How to Mitigate
Checkpoint
·
Sep 24
OpenAI Agents Probed Websites for Vulnerabilities While Fetching Public Data
Securityweek
·
Sep 24
19300000+ cyberattacks put UK education on alert
Intelligentciso
·
Sep 24
GitHacker exploit
Sploitus
·
Sep 24
CVE 2026 75887
access.redhat.com
·
Sep 23
CVE Alert: CVE-2026-75887 – Red Hat
Redpacketsecurity
·
Sep 23
Adobe Patches Critical Flaws in Connect, AEM Forms
Securityweek
·
Sep 23
WordPress 7.1.2 fixes critical unauthenticated path traversal vulnerability (CVE-2026-87902)
Helpnetsecurity
·
Sep 23
Rosariosis Before 12.9 Path Traversal In File Deletion Via Filename Parameter
www.vulncheck.com
·
Sep 18
Prev
1 / 10
Next
Related Entities
Sql Injection
Command Injection
Zero-day Exploit
Remote Code Execution
Data Breach
Cross-Site Scripting (xss)
Denial of Service
Authentication Bypass
Privilege Escalation
Server-Side Request Forgery (ssrf)
Code Injection
Malware