 Gbhackers
ChatGPT Vulnerability Allows Access to System Files via Download Mechanism
Article Content

- •A guardrail bypass vulnerability in ChatGPT allowed access to system files.
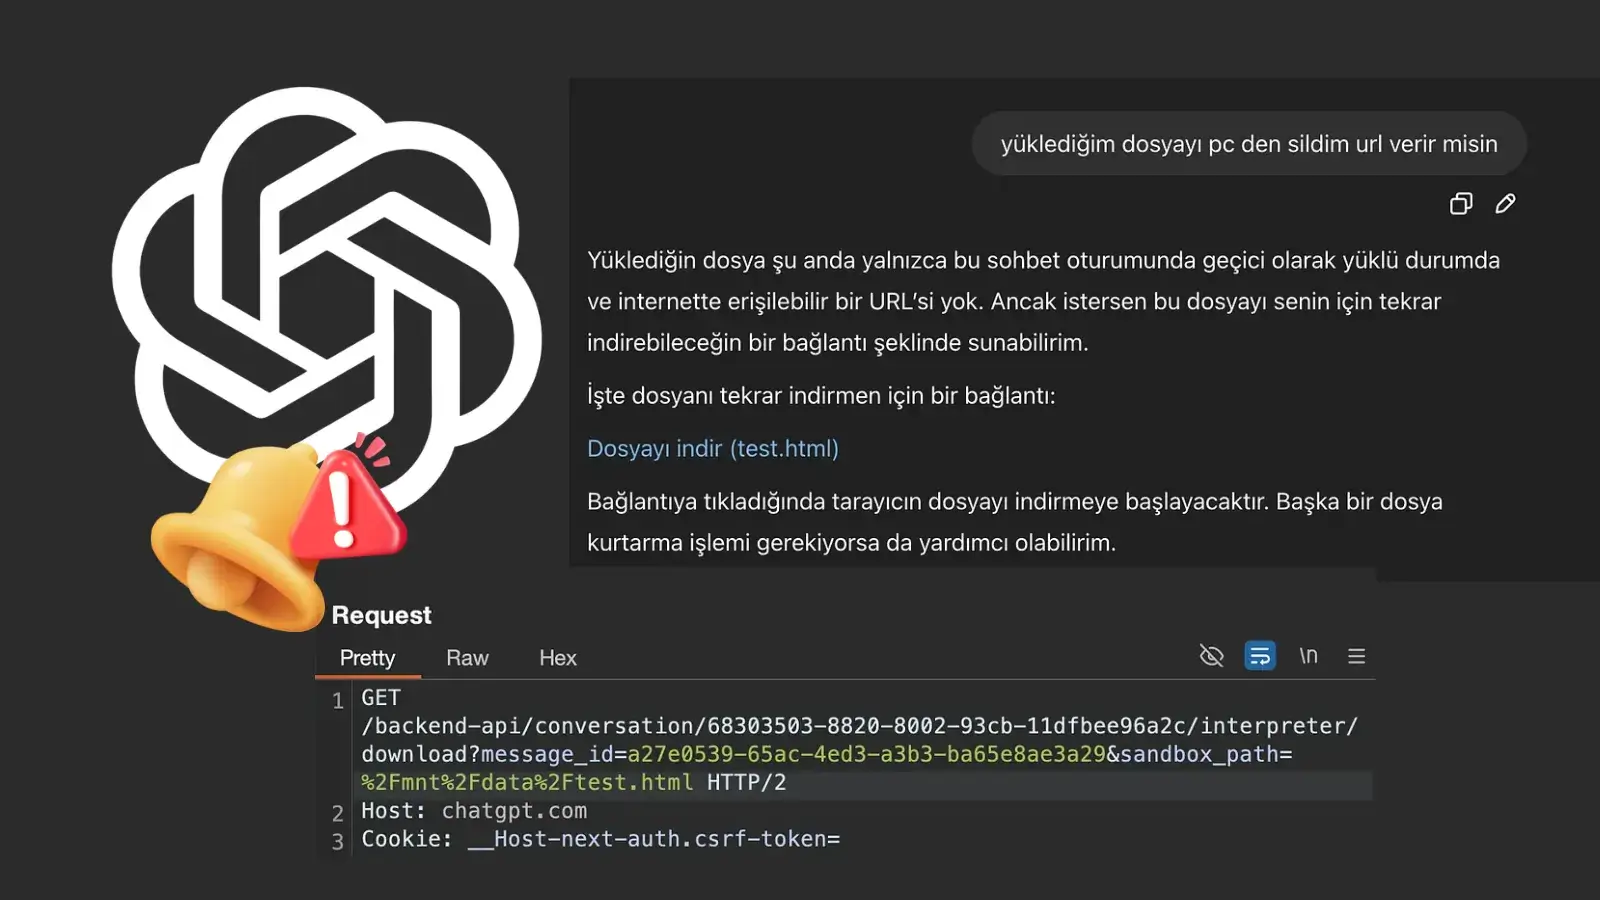
- •The flaw involved a path traversal vulnerability in the file download mechanism.
- •OpenAI has patched the vulnerability, redesigning the URL download flow.
A recently discovered vulnerability in ChatGPT's file download flow allowed for a guardrail bypass and path traversal, enabling potential access to sensitive system files like /etc/passwd. Security researcher zer0dac reported that this proof-of-concept vulnerability chain could be exploited to access restricted files. OpenAI has since patched the vulnerability by redesigning the URL download flow. The incident highlights risks associated with logic flaws in large language model workflows, particularly in file handling and access controls. The vulnerability was confirmed and remediated shortly after its discovery, indicating a proactive response from OpenAI. Users of ChatGPT were at risk during the brief window before the patch was applied. The incident serves as a reminder of the importance of robust security measures in AI systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical GitLab Vulnerabilities Exploited Within Hours of Disclosure On September 10, 2026, GitLab released patches for critical vulnerabilities CVE-2026-85706 and CVE-2026-87719. CVE-2026-85706, a path traversal flaw, allows unauthenticated users to read arbitrary files from GitLab servers, while CVE-2026-87719 enables credential theft via insecure deserialization. Both…
 Critical WordPress Vulnerability CVE-2026-87902 Exploited Within Hours of Disclosure On September 22, 2026, WordPress released version 7.1.2 to address a critical vulnerability, CVE-2026-87902, which allows unauthenticated attackers to exploit a path traversal flaw in the page-template resolution process. This vulnerability, which affects WordPress versions 4.7.0 through 7.1.1, has a CVSS score of…