 Securityaffairs.Co
Cyberattack on France's ANTS Exposes Personal Data of Users
Article Content

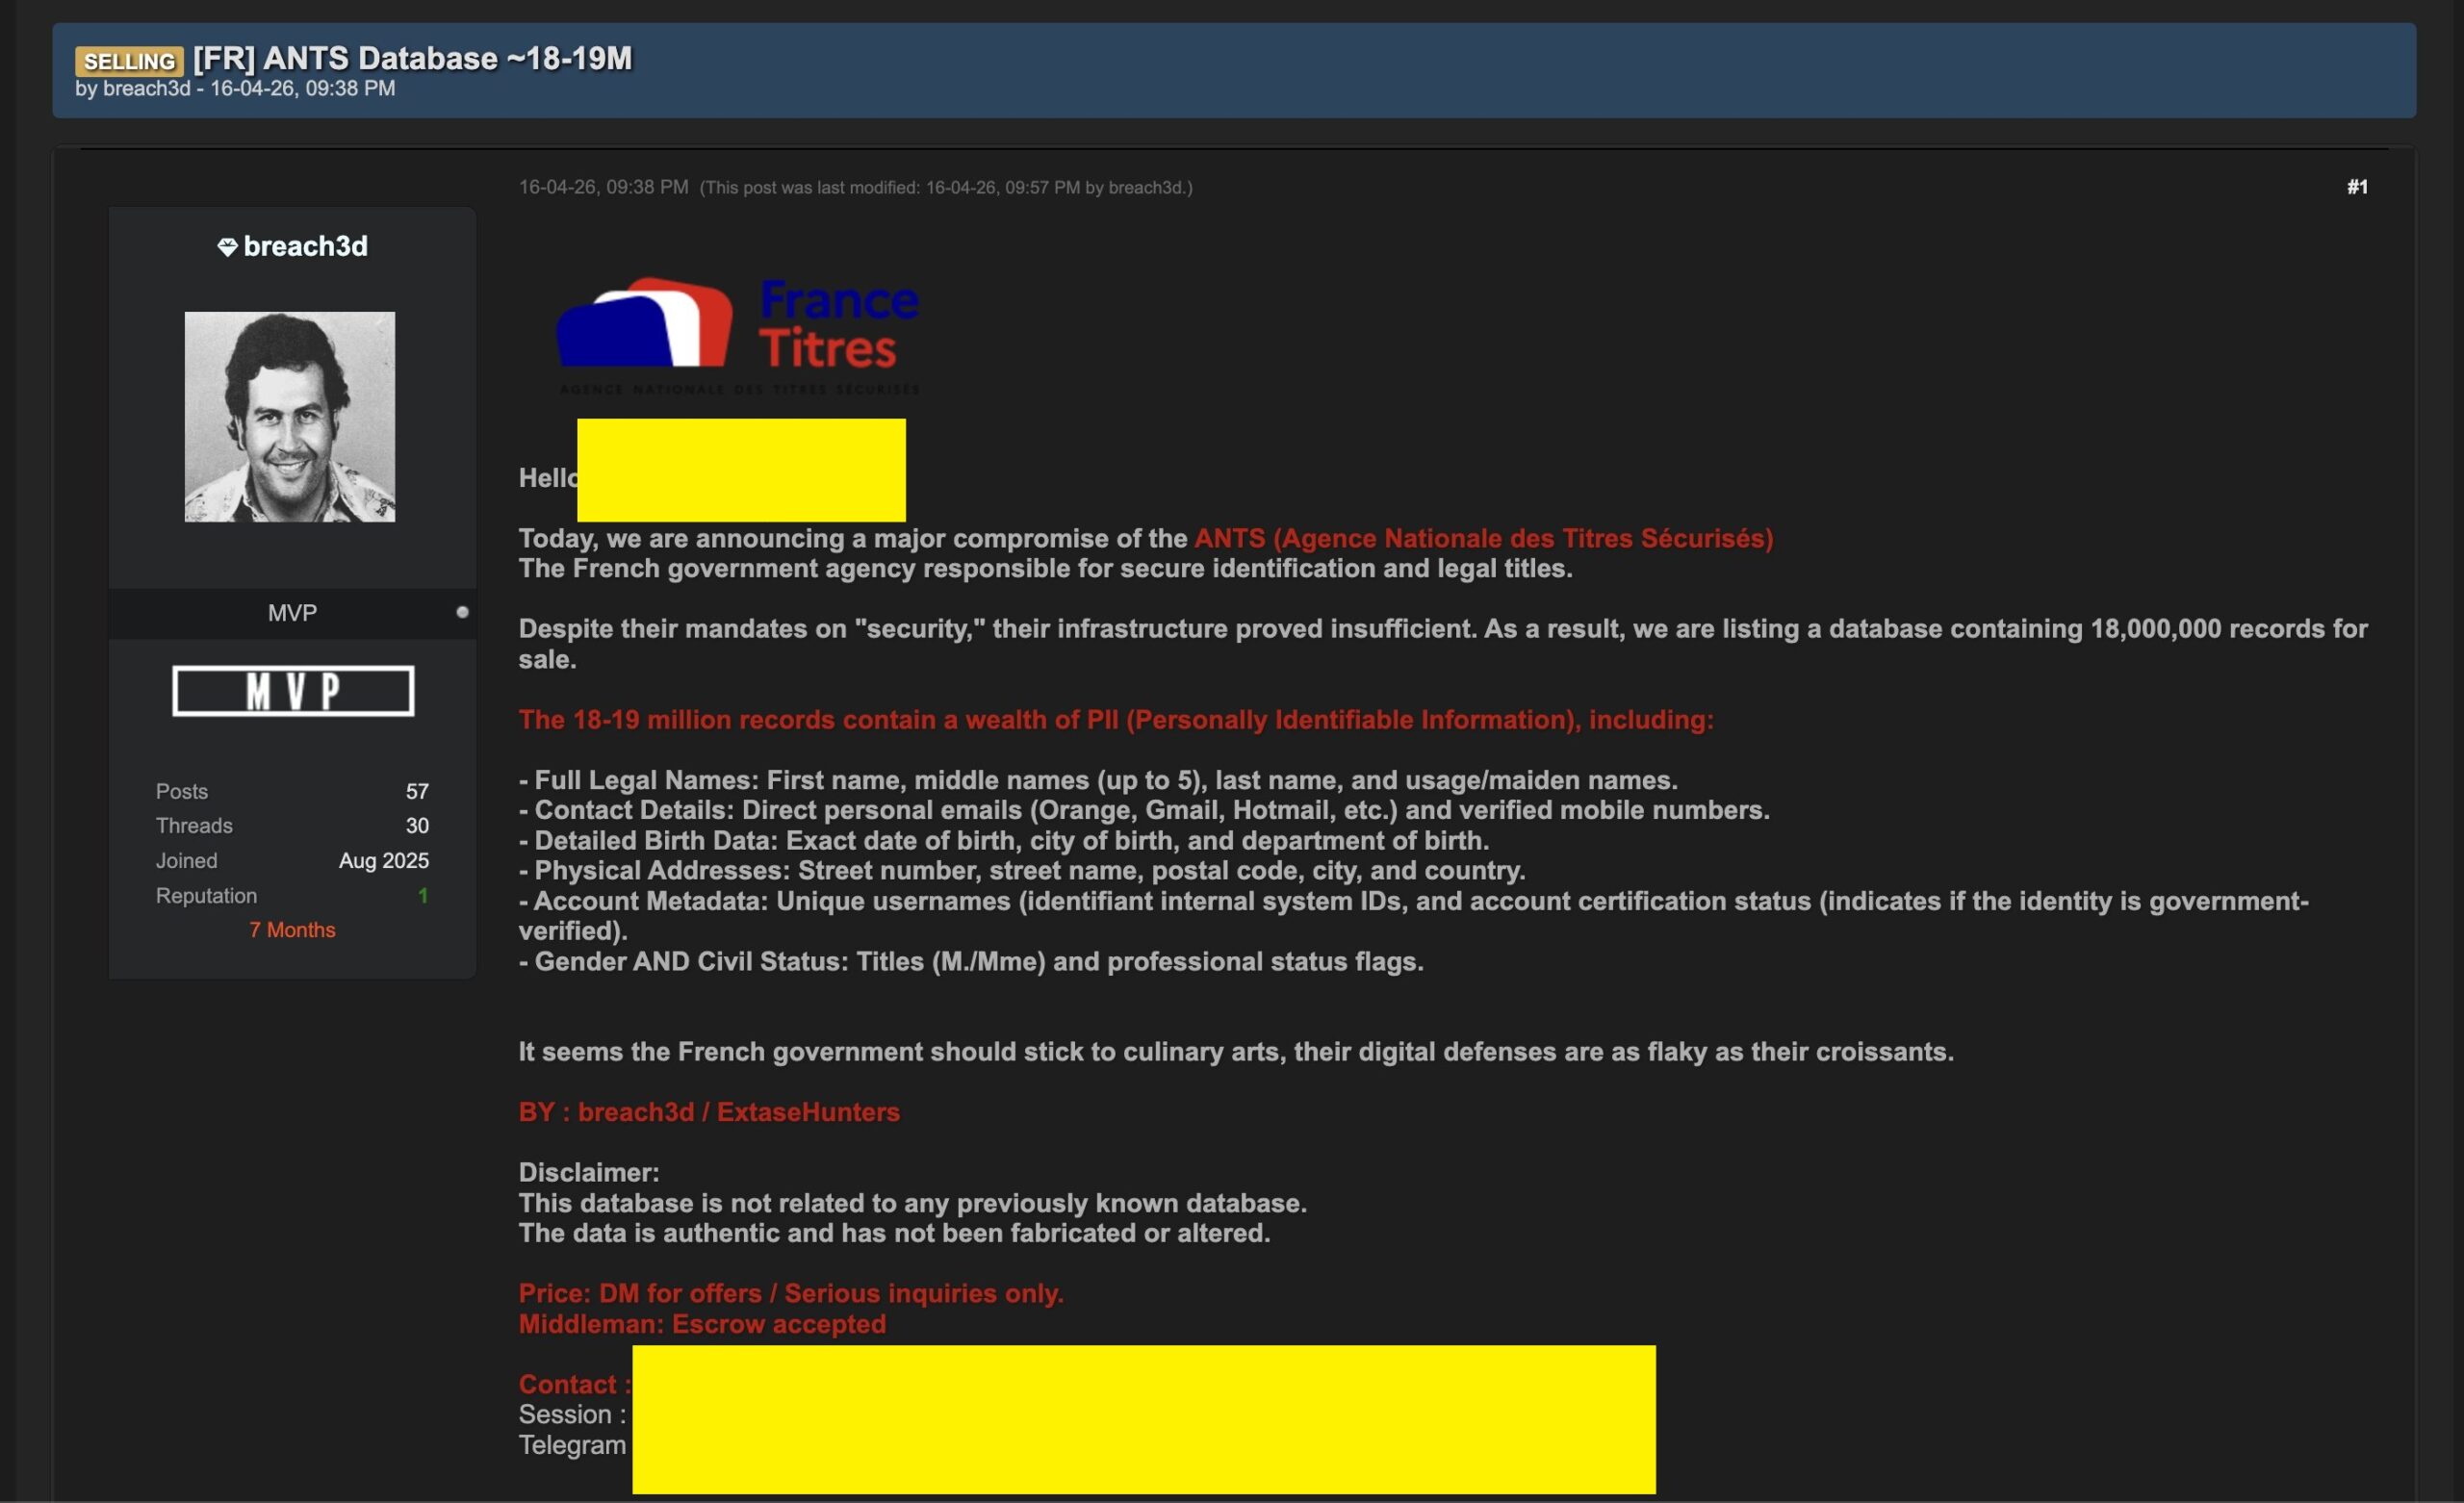
- •The ANTS cyberattack occurred on April 15, 2026, affecting personal data of users.
- •Compromised data includes names, email addresses, and dates of birth.
- •Users are advised to be vigilant against phishing attempts following the breach.
The Agence nationale des titres sécurisés (ANTS), France's official document authority, experienced a cyberattack on April 15, 2026, which resulted in the unauthorized access of personal data from its users. The breach affects individuals applying for ID cards, passports, residency cards, and driving licenses, with information such as names, email addresses, and dates of birth being compromised. Although the exact number of affected individuals has not been disclosed, the Interior Ministry has advised those impacted to remain vigilant against potential phishing scams. ANTS has since enhanced its security measures and filed a criminal report with the Paris prosecutor. This incident is part of a broader trend of cyberattacks targeting professional databases in France throughout 2026. The Ministry confirmed that supplementary data submitted during various procedures was not disclosed, and no immediate action is required from users. However, those whose data was compromised are at a higher risk of scams.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (35)
Following this threat?
Track ANTS in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…