
Danabot Malware Version 669 Resurfaces After Operation Endgame
Article Content
Browse articles 
Danabot malware has resurfaced with a new version, 669, following the conclusion of Operation Endgame. This resurgence poses risks to various systems as it exploits vulnerabilities to facilitate cyber attacks. The specific targets and impact of this version have not been detailed in the articles.
Ask AI about this cluster
Answers cite the sources they use
Updated 243d ago How this analysis works
More articles in this cluster (2)
Following this threat?
Track Danabot in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Stealc Stealer: New Malware Threats Emerge Stealc is a new information stealer malware that has been sold as Malware-as-a-Service since January 9, 2023. It primarily targets Windows systems, stealing data from web browsers, cryptocurrency wallets, and other applications. The malware is advertised by its presumed developer, Plymouth, on Russian-speaking…
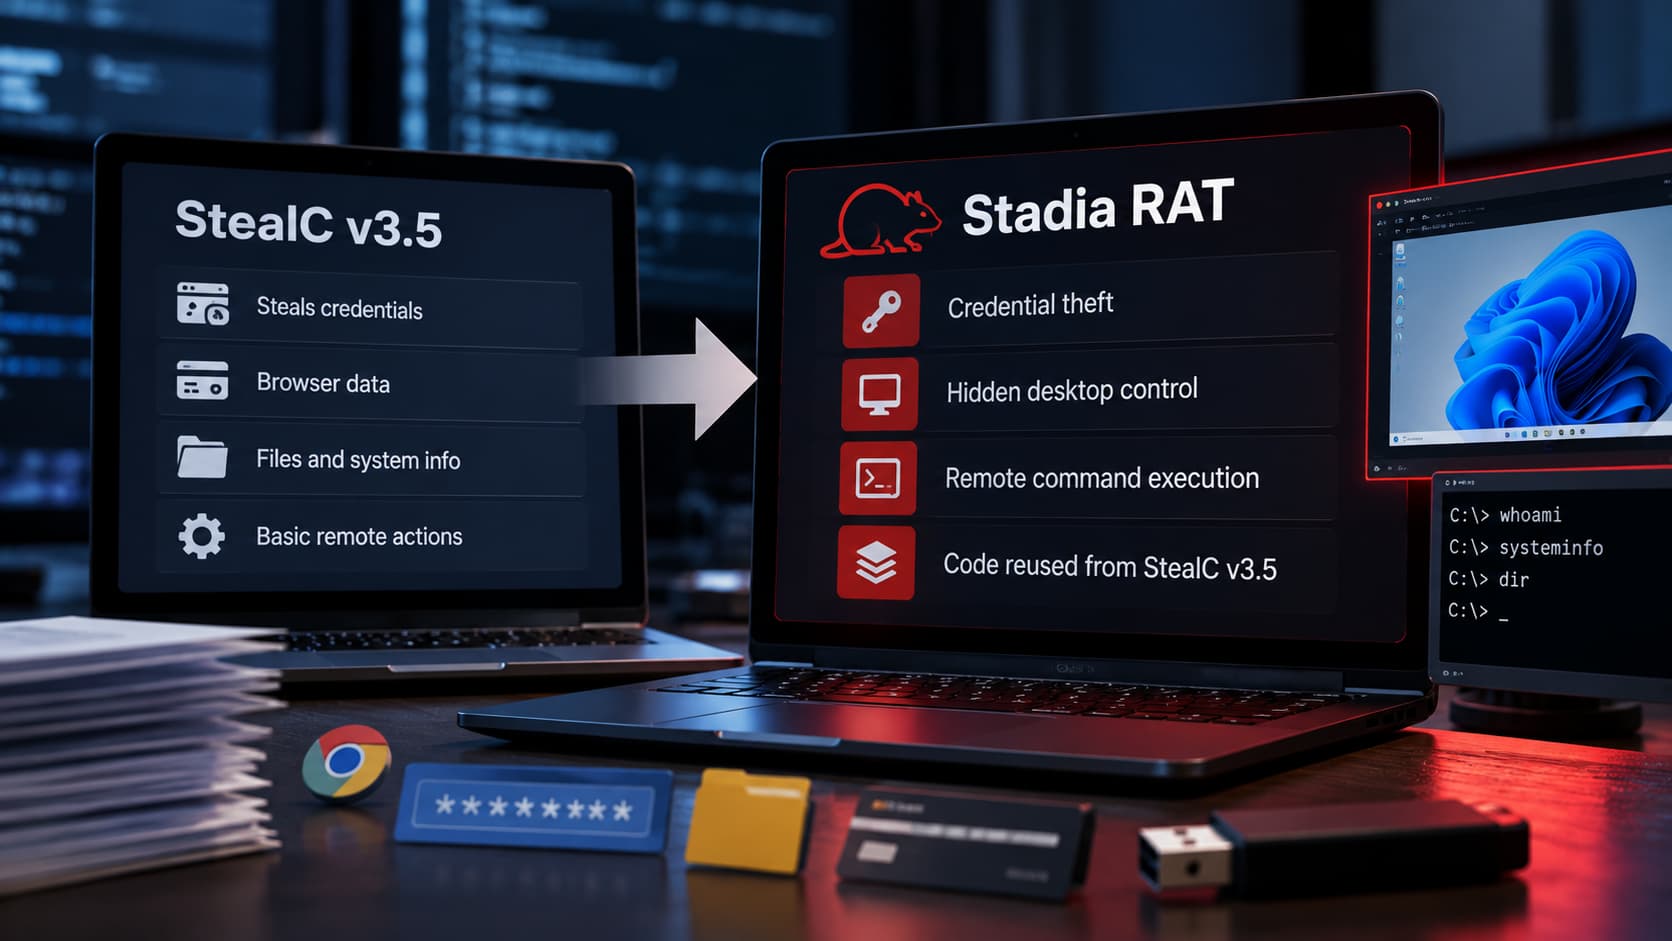 StealC Malware Revives as Stadia RAT with Enhanced Capabilities Following the takedown of StealC by Europol in June 2026, its seller has re-emerged with a new remote access trojan (RAT) named Stadia. This RAT combines credential theft with remote desktop control and command execution, utilizing code from StealC v3.5. Stadia was advertised on October 16, 2026, and features six…