 Pasqualepillitteri.It
DarkSword Malware Targets iPhones via Compromised Websites
Article Content

- •DarkSword exploits six vulnerabilities in iOS, three of which are zero-days.
- •The malware targets unpatched iPhones through compromised legitimate websites.
- •Google has patched the vulnerabilities, but many users remain vulnerable due to outdated software.
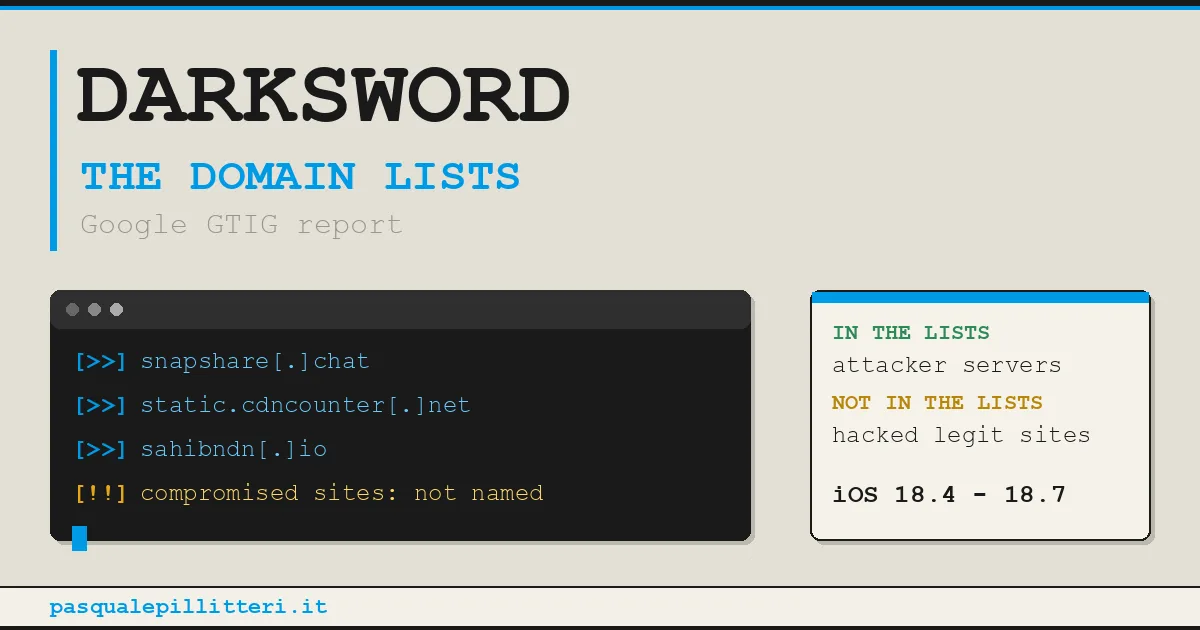
Google's Threat Intelligence Group reported on the DarkSword malware, an exploit kit targeting iPhones running iOS versions 18.4 to 18.7. The malware exploits six vulnerabilities, three of which are zero-days, to take control of devices when users visit compromised websites. The attackers have been linked to three distinct campaigns, including a suspected Russian espionage group targeting Ukrainian sites. While Google has patched all vulnerabilities in iOS 26.3, many users remain at risk if they have not updated their devices. The malware can be deployed easily by less skilled attackers, making it a significant threat. The report highlights that legitimate sites, including a Ukrainian government domain, were used to deliver the malware, increasing the scope of potential victims. Current versions of iOS that have been patched include 26.4 and earlier updates for iOS 15 and 16.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track DarkSword in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which iOS versions are affected by DarkSword?
How can I protect my device from DarkSword?
What should I do if I suspect my device is infected?
Continue Reading
 Star Blizzard Expands Phishing Operations with RedFlick Technique Russian state-sponsored hacking group Star Blizzard has significantly escalated its phishing operations since January 2026, targeting over 100 organizations, primarily in the U.S. and U.K. The group has shifted from targeted spear-phishing to large-scale campaigns, employing a new malware delivery method called…
 Atlassian Flaw Exploited Within Hours of Disclosure A vulnerability in Atlassian Data Center products, tracked as CVE-2026-21589 with a CVSS score of 9.3, was within two hours of its disclosure. The flaw allows arbitrary file access and affects multiple products, including Bitbucket, Confluence, and Jira. Exploitation activity targeting honeypot networks began…