 Vietnam.Vn
Hanoi Police Warn of Dangerous Malware Strains Targeting Officials
Article Content

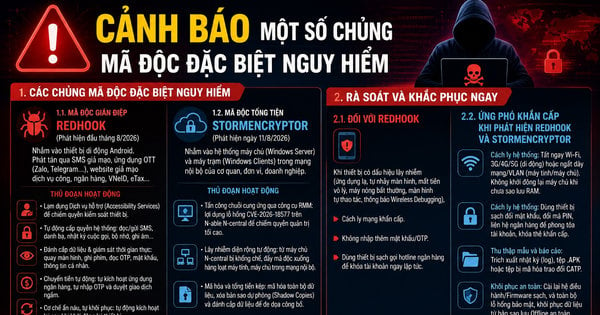
- •RedHook spyware targets Android devices, exploiting Accessibility Services for control.
- •StormEncryptor ransomware targets Windows systems, leveraging CVE-2026-18577 for access.
- •Both malware strains pose serious risks to officials' mobile devices and organizational networks.
Hanoi City Police have identified two particularly dangerous malware strains, RedHook spyware and StormEncryptor ransomware, which are being exploited by hacker groups to attack information systems and mobile devices of officials and civil servants. RedHook, discovered in early August 2026, targets Android devices through fake SMS and messaging apps, gaining control via Accessibility Services and enabling data theft and unauthorized banking transactions. StormEncryptor, identified on August 11, 2026, targets Windows Server and Client systems within organizations, exploiting CVE-2026-18577 to gain administrative control through compromised remote management tools. Both malware strains pose significant risks to cybersecurity and information security in the region. The situation is ongoing, with authorities urging vigilance and prompt action against potential infections.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track StormEncryptor, RedHook and CVE-2026-18577 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…