Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Cisco has disclosed a critical vulnerability (CVE-2026-76460) in its Identity Services Engine (ISE) that allows unauthenticated remote attackers to bypass authentication via a flaw in an API endpoint. This vulnerability has a CVSS score of 10.0 and is actively being exploited in the wild, prompting...
N-able has released Hotfix 4 for its N-central platform to address CVE-2026-86218, a critical remote code execution (RCE) vulnerability rated CVSS 10.0. This flaw allows unauthenticated attackers to execute arbitrary code on N-central servers running versions prior to 2026.3.1.14. The vulnerability...
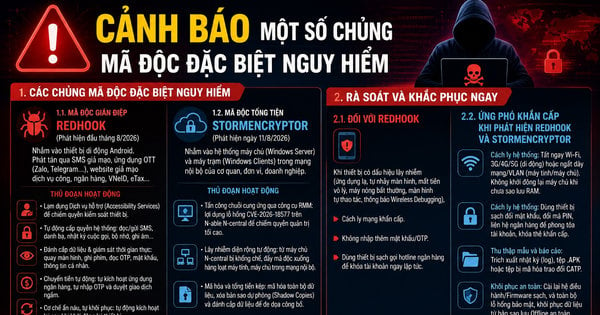
A financially motivated threat actor, Storm-1175, previously linked to Medusa ransomware, has begun deploying a new ransomware strain named StormEncryptor. This campaign was initiated after exploiting an authentication-bypass vulnerability (CVE-2026-18577) in the N-central remote monitoring tool. Th...
N-able has issued an emergency hotfix for CVE-2026-18577, an authentication bypass vulnerability in its N-central RMM platform, which allows remote, unauthenticated attackers to gain administrative access. This flaw affects all versions prior to 2026.3.1.7 and was actively exploited before the fix w...