 www.militarytimes.com
Laser Counter-Drone Systems Deployed at Mar-a-Lago Amid Heightened Security
Article Content

- •LOCUST laser counter-drone system deployed at Mar-a-Lago for enhanced security.
- •Deployment follows threats against Trump from Iran and recent assassination attempts.
- •U.S. military has positioned additional air defense systems in the area.
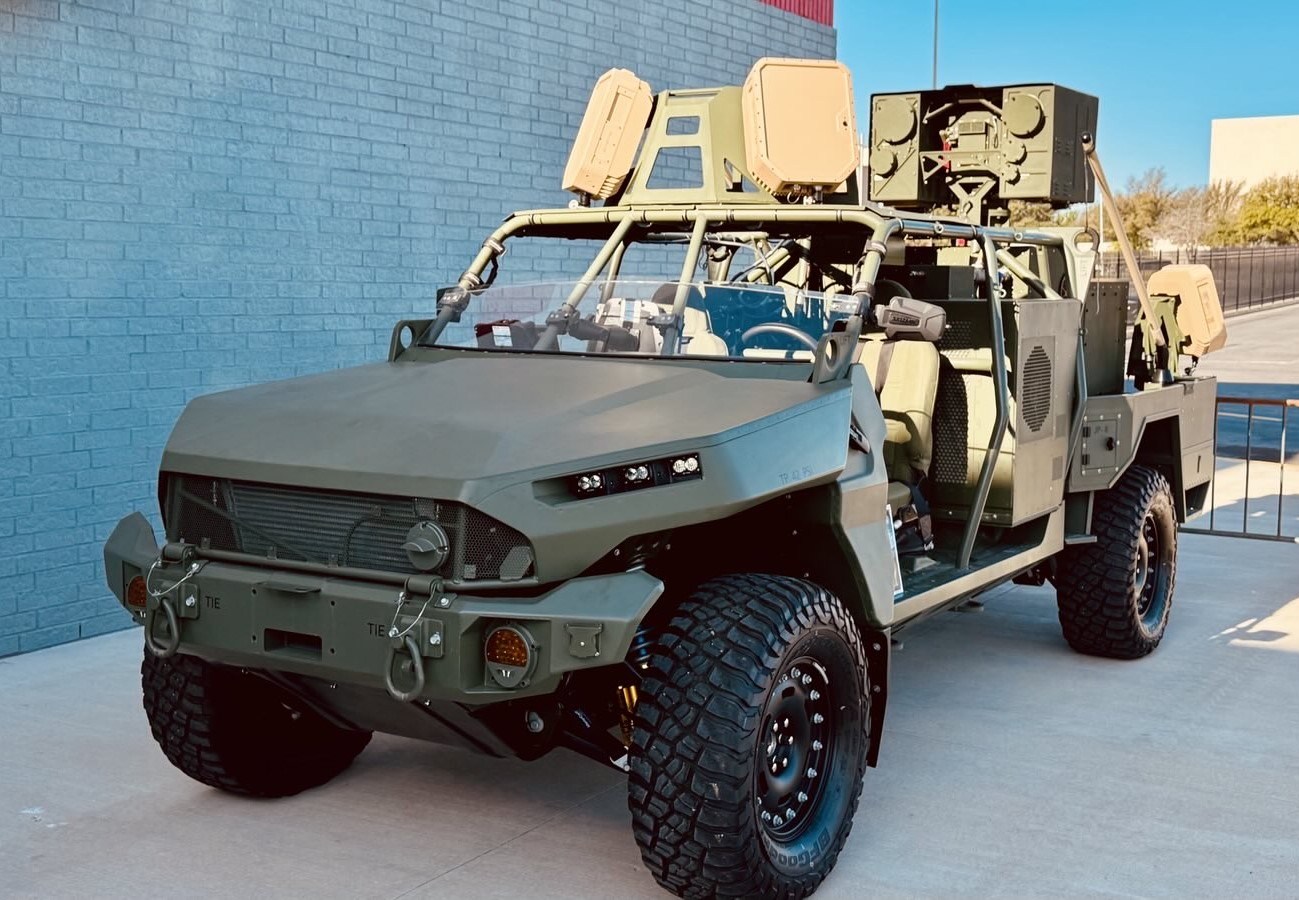
AeroVironment's LOCUST laser counter-drone system has been deployed at Mar-a-Lago, Florida, as part of enhanced security measures amid threats from Iran. The U.S. military has also positioned short-range air defense systems and Counter-Unmanned Aircraft System capabilities around the estate. The deployment follows a series of assassination threats against former President Trump, particularly from the Iranian regime. The U.S. Secret Service and NORAD confirmed the deployment of these advanced defense systems to protect against potential drone threats. The LOCUST system, mounted on a Joint Light Tactical Vehicle, represents a growing trend in military applications of directed-energy weapons. This development coincides with the upcoming mid-term elections, increasing the urgency for security enhancements.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What systems are being deployed at Mar-a-Lago?
Why is there heightened security at Mar-a-Lago?
What is the role of NORAD and USNORTHCOM in this deployment?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…