 Socket.Dev
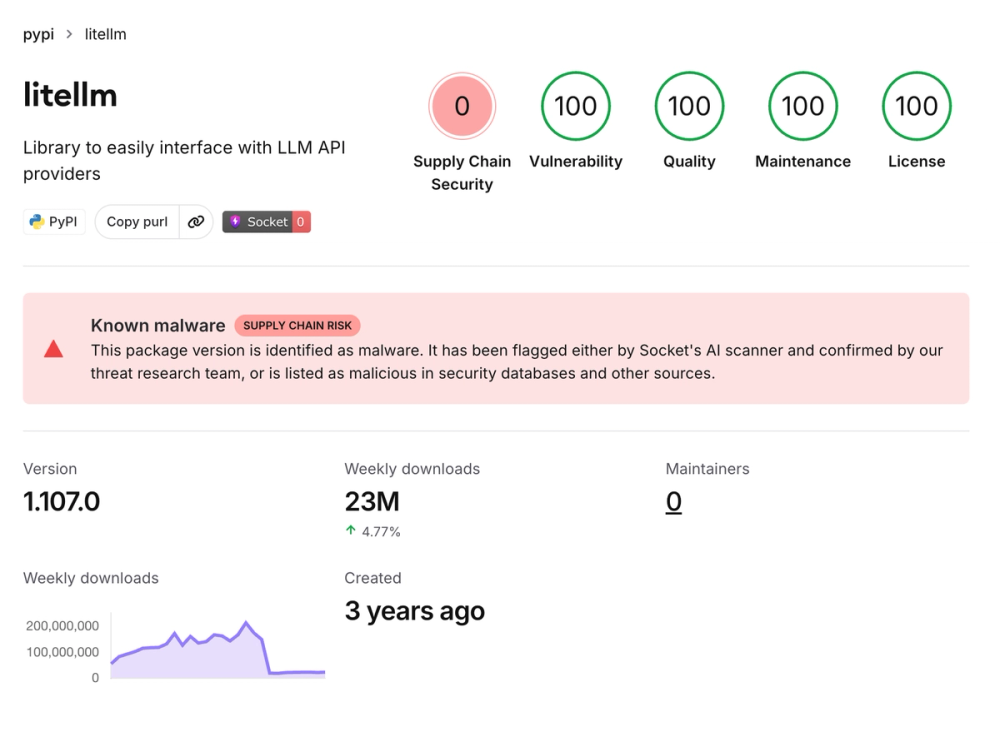
LiteLLM 1.107.0 Compromise: Credential Stealer and RAT Discovered
Article Content

- •LiteLLM 1.107.0 contains a credential stealer and RAT, affecting all platforms.
- •The malicious payload executes on Python startup, even without importing LiteLLM.
- •Users must check for specific temporary files to assess compromise and should stop using the affected version.
On October 21, 2026, version 1.107.0 of LiteLLM was compromised, containing a credential stealer and a remote access trojan (RAT) that executes on Python startup. The malicious code was injected into the package's wheels on PyPI and its official Docker image. Users who installed this version should assume their credentials are compromised and check for specific temporary files indicating the attack. The attack exploited a directive in LiteLLM's build configuration to include malicious files that are not present in the source repository. PyPI has since quarantined the compromised version, and the Docker image has been removed from public registries. This incident marks the second documented hijacking of LiteLLM in 2026, following a previous compromise earlier in the year. The malicious payloads can exfiltrate sensitive data and allow for remote code execution, affecting a wide range of users.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Privcollect and ASOS in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which versions of LiteLLM are affected?
What should I do if I installed this version?
Has the compromised version been removed?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…