 www.biometricupdate.com
Naver Pay Secures Biometric Certification Amidst Competitive Face Payment Expansion
Article Content

- •Naver Pay is the first in South Korea to secure ISO/IEC 24745 certification for biometric data.
- •The certification validates Naver's framework for managing biometric information but does not verify recognition accuracy.
- •Naver is competing with Toss by offering cashback incentives and expanding Face Sign usage across multiple venues.
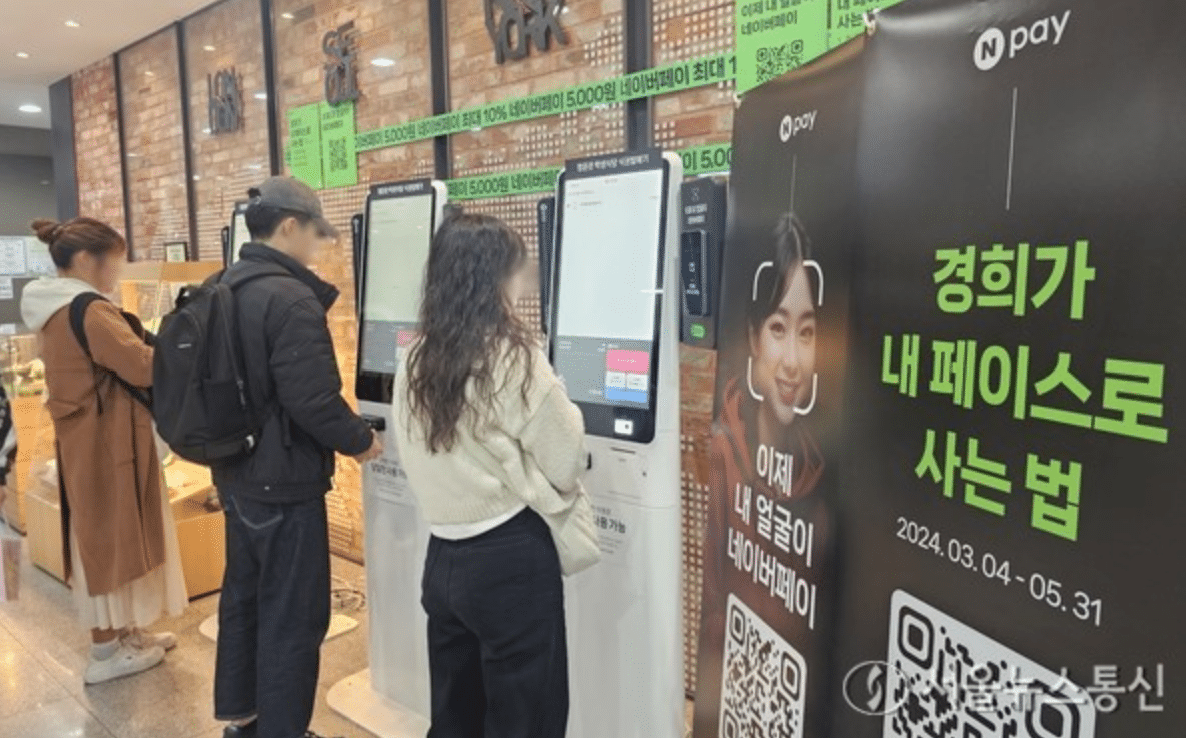
Naver Pay has achieved ISO/IEC 24745 certification for biometric data protection as it expands its Face Sign facial recognition payment service in South Korea. This certification, awarded by LRQA, validates Naver's framework for managing sensitive biometric information, including storage and transmission protocols. The certification does not assess facial recognition accuracy but indicates Naver's commitment to security, utilizing AI-based anti-spoofing technology and post-quantum cryptography. The move comes as Naver Financial intensifies competition with rival Toss, which has a larger market presence. To encourage adoption, Naver Pay is offering a 10% cashback incentive for transactions through its Connect payment terminals. The Face Sign service is being integrated into various venues, including university festivals and airports, highlighting the growing role of biometric authentication in financial transactions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What does the ISO/IEC 24745 certification cover?
How does Naver Pay ensure security in its Face Sign service?
What incentives is Naver offering to users?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Coordinated Attack On October 29, 2026, Binance suffered a large cyberattack attributed to North Korean hackers known as TraderTraitor, resulting in the theft of approximately $6.3 billion in cryptocurrency. The attackers gained initial access through social engineering tactics, including a fake job offer that led to malware…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…