 www.navytimes.com
Navy Renames Expeditionary Command After Afghanistan War Reflection
Article Content

- •The Navy renamed its expeditionary command to better reflect its evolving mission.
- •The rebranding is part of a strategic shift following the Afghanistan War.
- •Daily operations of the command will not be affected by the name change.
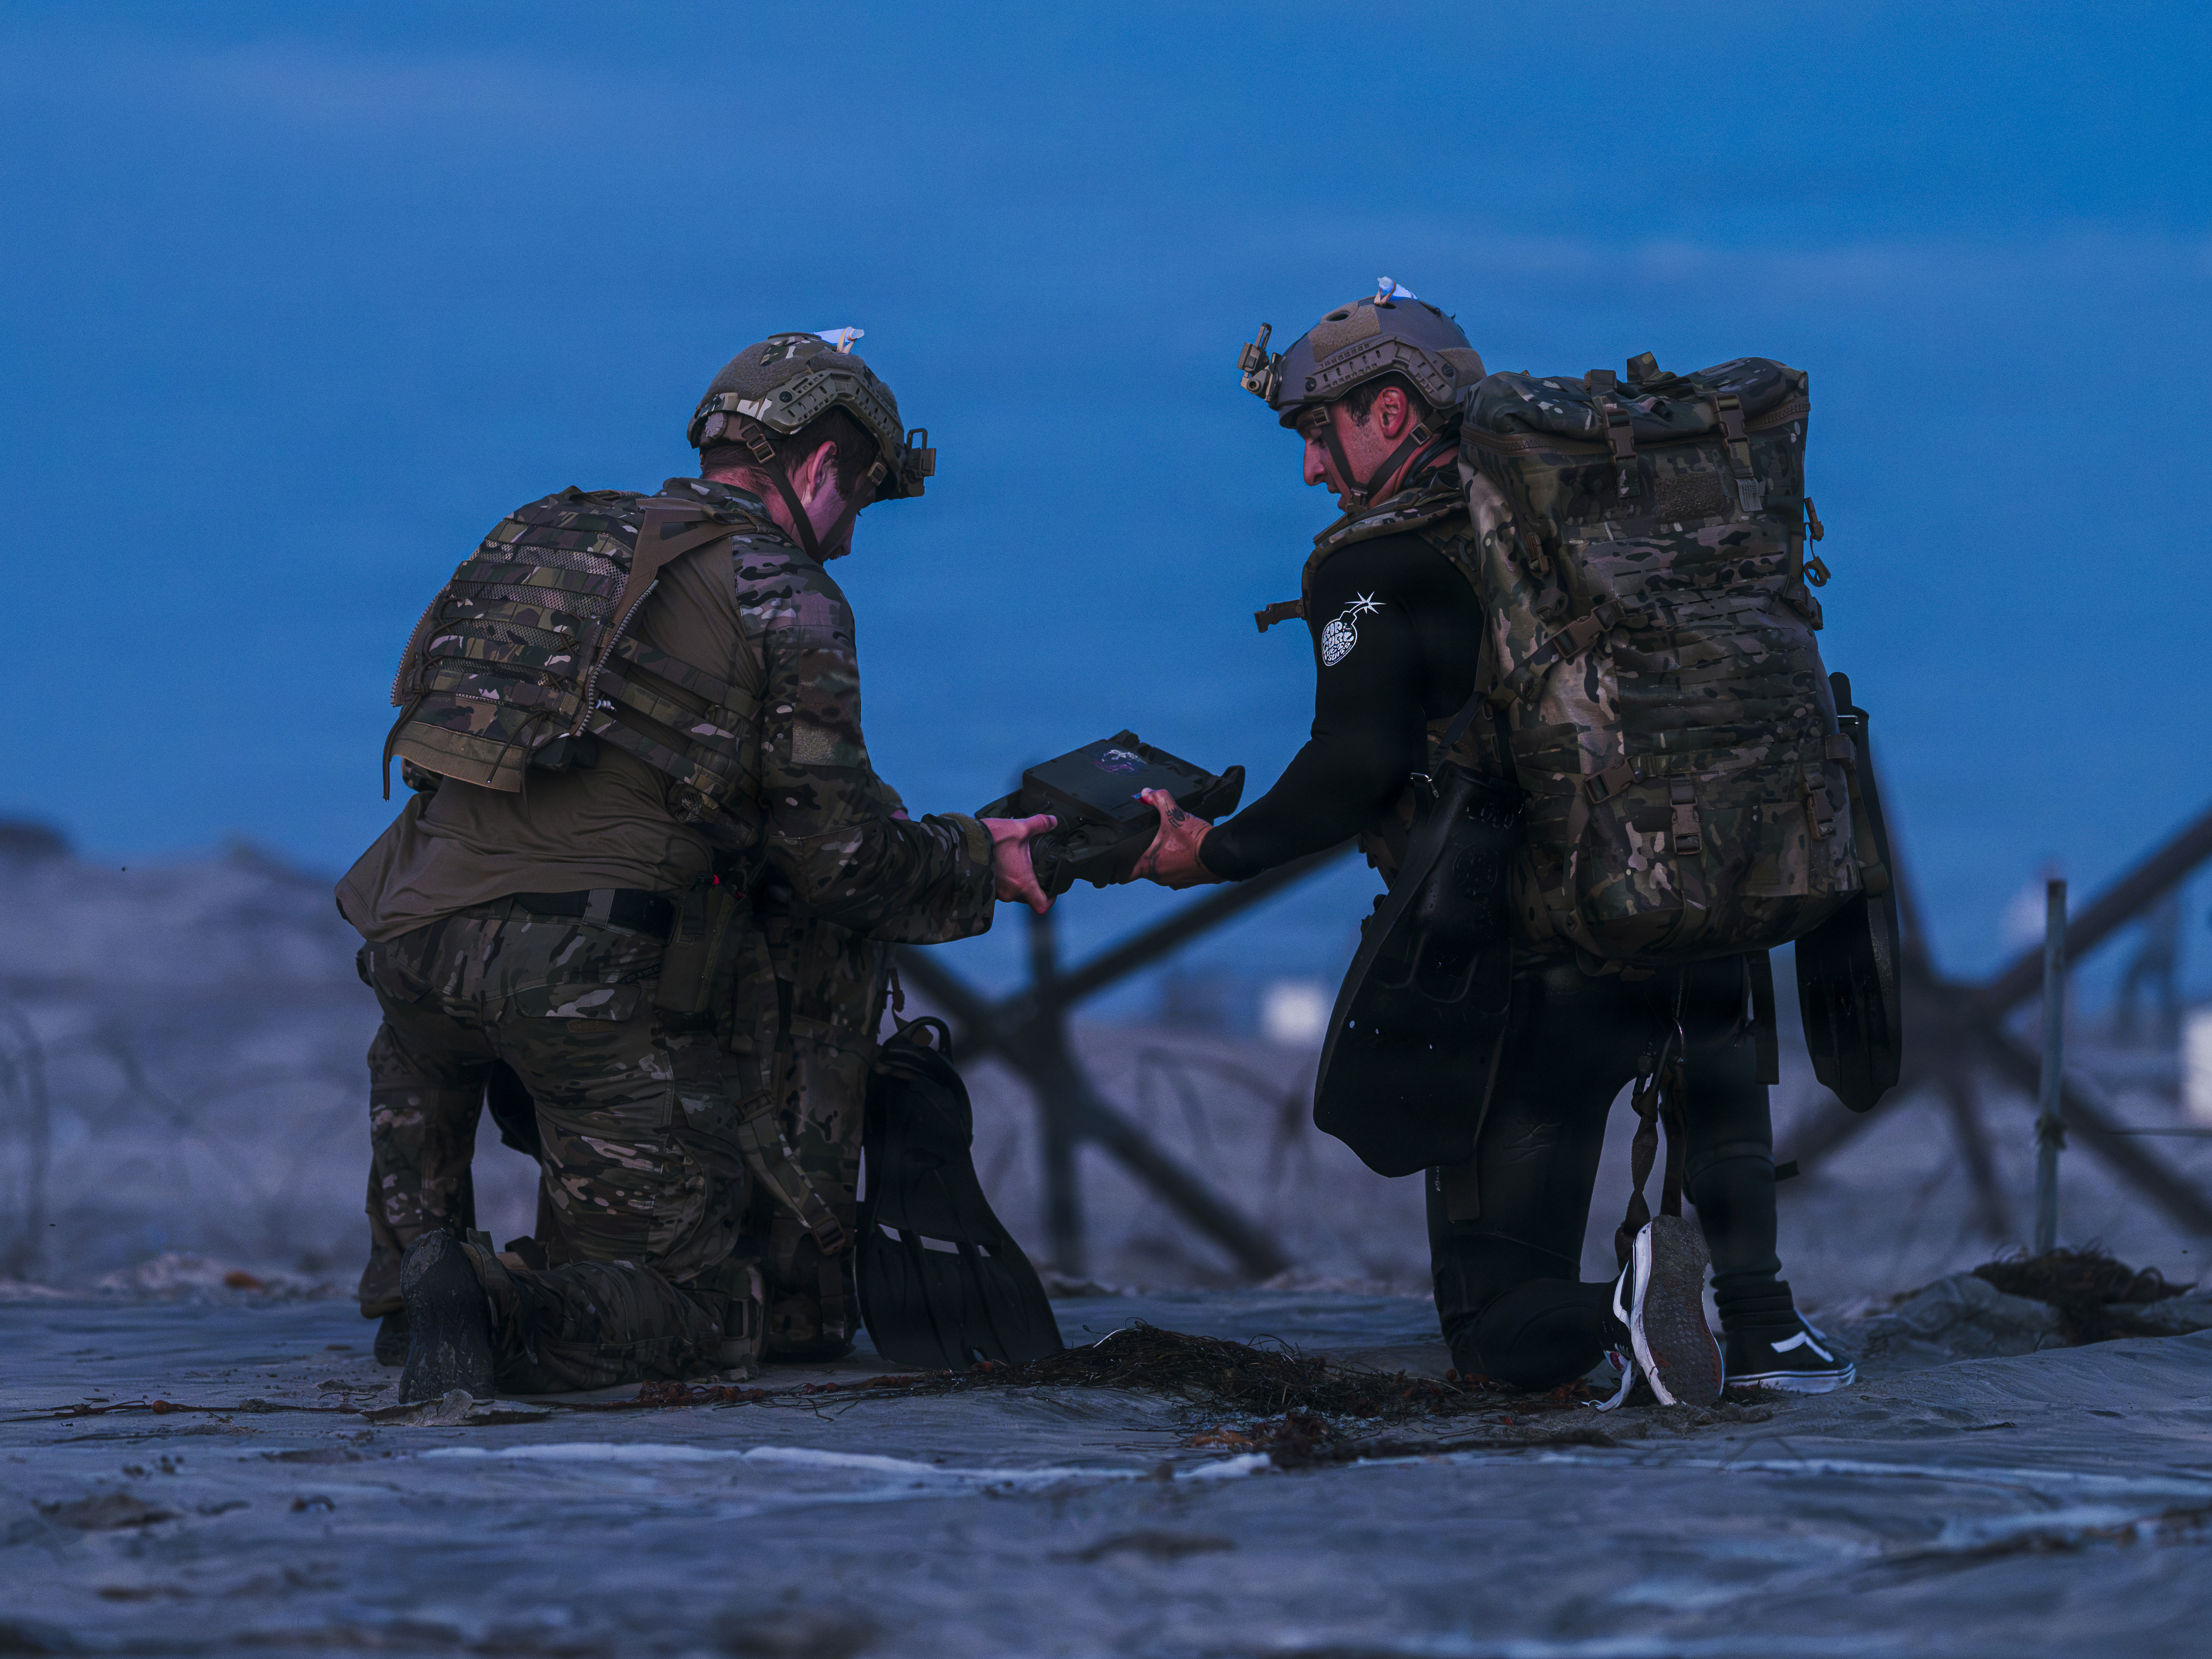
The U.S. Navy has officially renamed the Navy Expeditionary Combat Command to Commander, Navy Expeditionary Forces as of October 1, 2026. This change reflects a strategic pivot following the end of the Afghanistan War, aimed at enhancing the command's role in training and preparing expeditionary sailors for future combat missions. Rear Adm. Bradley Andros emphasized the need for the command to adapt to evolving warfare requirements, questioning its relevance in the post-war context. The rebranding aligns with the Navy's investment in autonomous systems and aims to improve operational readiness and capabilities across various mission areas, including explosive ordnance disposal and maritime security. The command's daily operations will remain unchanged despite the name change.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What prompted the renaming of the command?
Will the operations of the command change after the renaming?
What are the new responsibilities of the Commander, Navy Expeditionary Forces?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Coordinated Attack On October 29, 2026, Binance suffered a large cyberattack attributed to North Korean hackers known as TraderTraitor, resulting in the theft of approximately $6.3 billion in cryptocurrency. The attackers gained initial access through social engineering tactics, including a fake job offer that led to malware…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…