 blog.primeradiant.com
New External Sandboxes Enhance Safety for Coding Agents
Article Content

- •Three sandbox implementations released for coding agents.
- •Sandboxes isolate code execution to prevent system damage.
- •Network access is restricted by default, enhancing security.
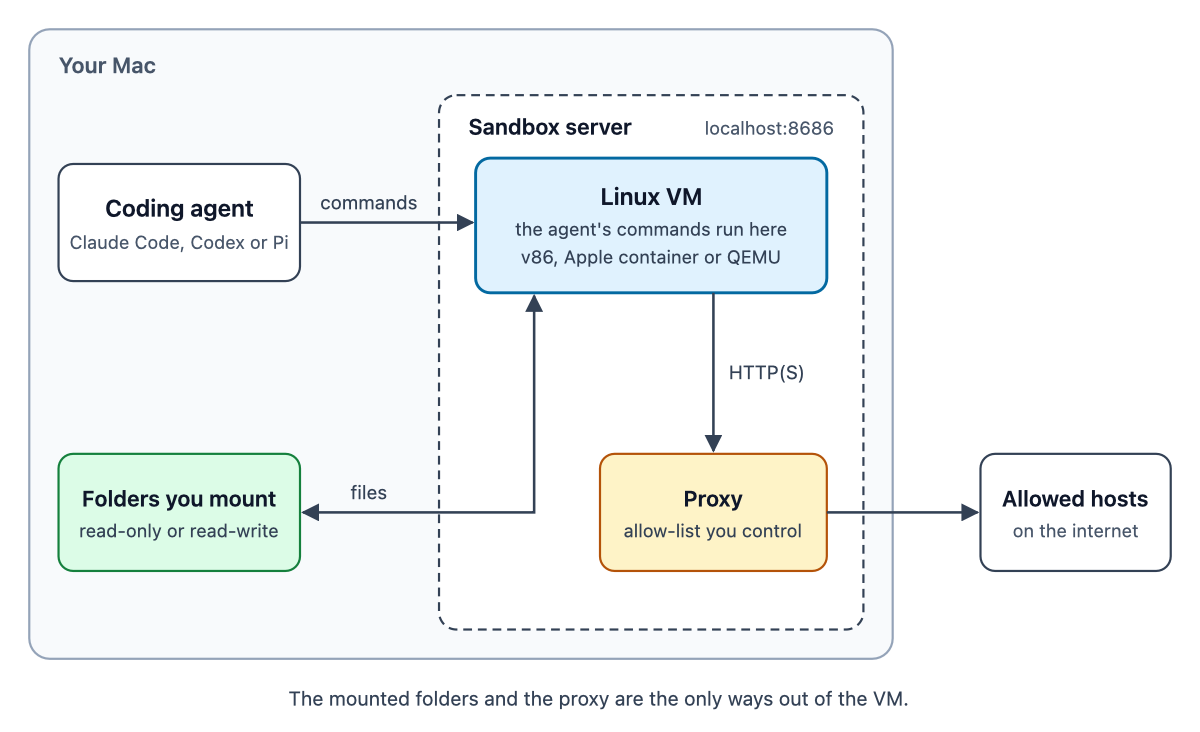
On November 17, 2026, Simon Willison and Prime Radiant introduced external sandboxes designed for coding agents, enhancing security during code execution. The sandboxes allow agents like Pi, Claude Code, and Codex to run code in isolated environments, mitigating risks from prompt injection attacks and other vulnerabilities. Three implementations were released: one using Node.js and WebAssembly, another with Apple Containers, and a third utilizing Microsoft's Quicksand. Each sandbox restricts network access and allows for controlled folder access, ensuring that agents cannot interact with the broader system. This development aims to provide a safer way to experiment with AI models without compromising system integrity. The project is currently in prototype stage, with detailed instructions available for users to set up and test the sandboxes.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
What coding agents can use these sandboxes?
How do these sandboxes enhance security?
Are there any known vulnerabilities in these sandboxes?
Continue Reading
 Critical Code Injection Vulnerability in Staggs Plugin for WordPress A critical code injection vulnerability, CVE-2026-78287, has been identified in the Staggs plugin for WordPress, affecting versions up to 3.3.0. This flaw allows unauthenticated attackers to execute arbitrary code remotely, posing severe risks to affected sites. The vulnerability stems from improper control over code…
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…