Article Content

- •CISA reports active exploitation of Unitronics PLCs in U.S. water facilities.
- •Affected systems include critical components for water treatment and monitoring.
- •CISA recommends immediate password changes and multifactor authentication.
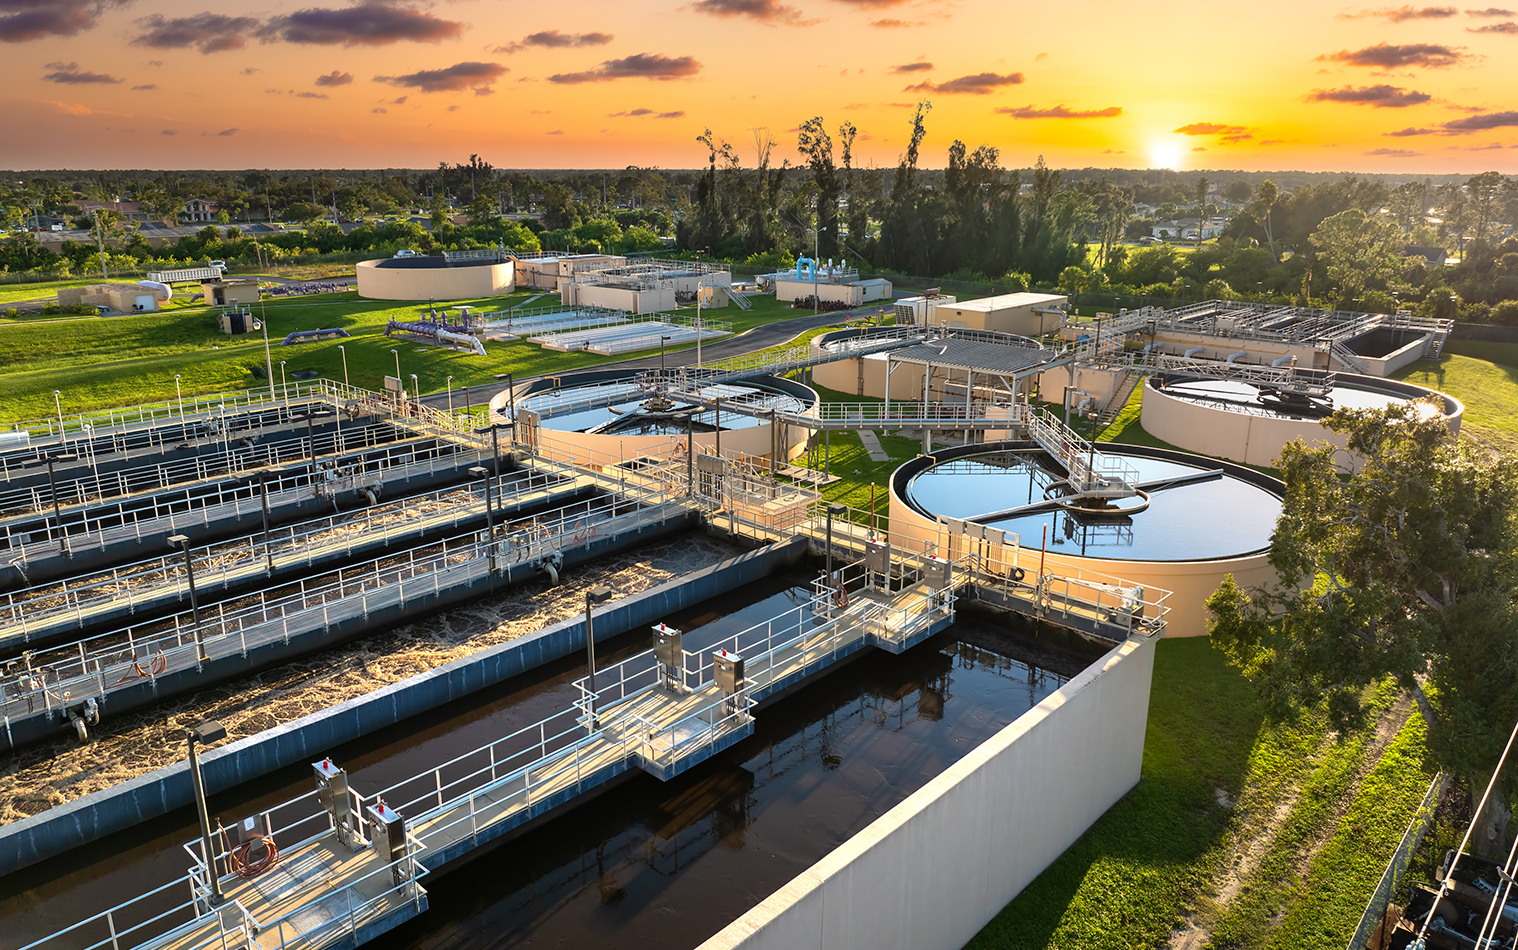
CISA has reported of Unitronics programmable logic controllers (PLCs) in U.S. Cyber threat actors are targeting these PLCs, which are critical for controlling water and wastewater treatment processes. The affected municipality's water authority has taken the system offline and switched to manual operations, ensuring no risk to drinking water. The exploitation likely stems from poor password security and internet exposure. CISA recommends changing default passwords and implementing multifactor authentication to secure these systems. The specific PLC involved is the Unitronics Vision Series, which includes a Human Machine Interface (HMI). This incident is part of a broader concern regarding cybersecurity vulnerabilities in the water sector, highlighted by recent NIST guidelines. The situation remains under close observation as CISA continues to monitor the threat landscape.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What specific vulnerabilities are being exploited?
What immediate actions should organizations take?
Is there a risk to drinking water safety?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Coordinated Attack On October 29, 2026, Binance suffered a large cyberattack attributed to North Korean hackers known as TraderTraitor, resulting in the theft of approximately $6.3 billion in cryptocurrency. The attackers gained initial access through social engineering tactics, including a fake job offer that led to malware…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…