 Bleepingcomputer
Operation Endgame Disrupts Major Malware Networks Rhadamanthys, VenomRAT, and Elysium
Article Content
Browse articles 
Law enforcement from nine countries has dismantled over 1,000 servers associated with the Rhadamanthys infostealer, VenomRAT remote access Trojan, and Elysium botnet during Operation Endgame. This operation, coordinated by Europol and Eurojust, targeted cybercriminal infrastructures that infected hundreds of thousands of computers and compromised millions of credentials. The raids took place from November 10 to 13, 2025.
Ask AI about this cluster
Answers cite the sources they use
Updated 242d ago How this analysis works
More articles in this cluster (8)
Following this threat?
Track Elysium in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
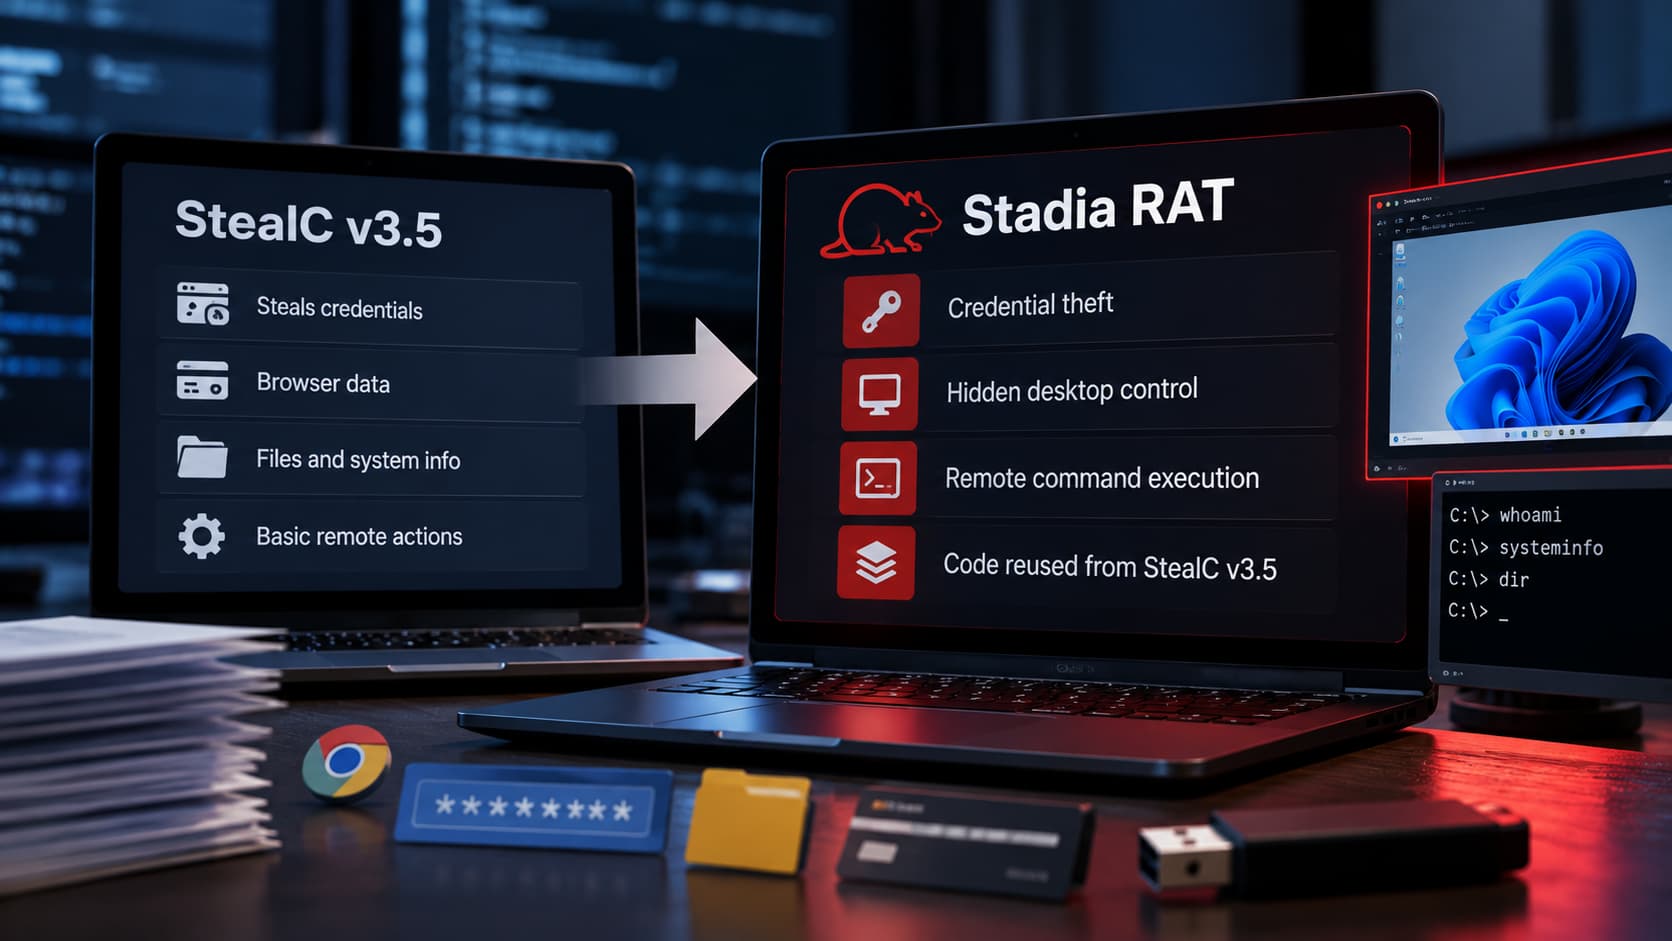 StealC Malware Revives as Stadia RAT with Enhanced Capabilities Following the takedown of StealC by Europol in June 2026, its seller has re-emerged with a new remote access trojan (RAT) named Stadia. This RAT combines credential theft with remote desktop control and command execution, utilizing code from StealC v3.5. Stadia was advertised on October 16, 2026, and features six…
 Australia Disrupts Amadey Malware, Cuts Off 180,000 Infected Systems The Australian Signals Directorate (ASD) successfully breached the command-and-control backend of the Amadey malware, disconnecting approximately 180,000 infected computers globally. This operation, which requires government approval, severed the connection between the malware's controllers and the compromised…