 Tovima
Pro-Russian Hackers Leak Italian Foreign Minister's Data on Dark Web
Article Content

- •Antonio Tajani's personal data has been leaked on the dark web by pro-Russian hackers.
- •The hackers are offering money for more information about Tajani and his family.
- •Italian authorities are investigating the incident amidst a rise in cyber threats across Europe.
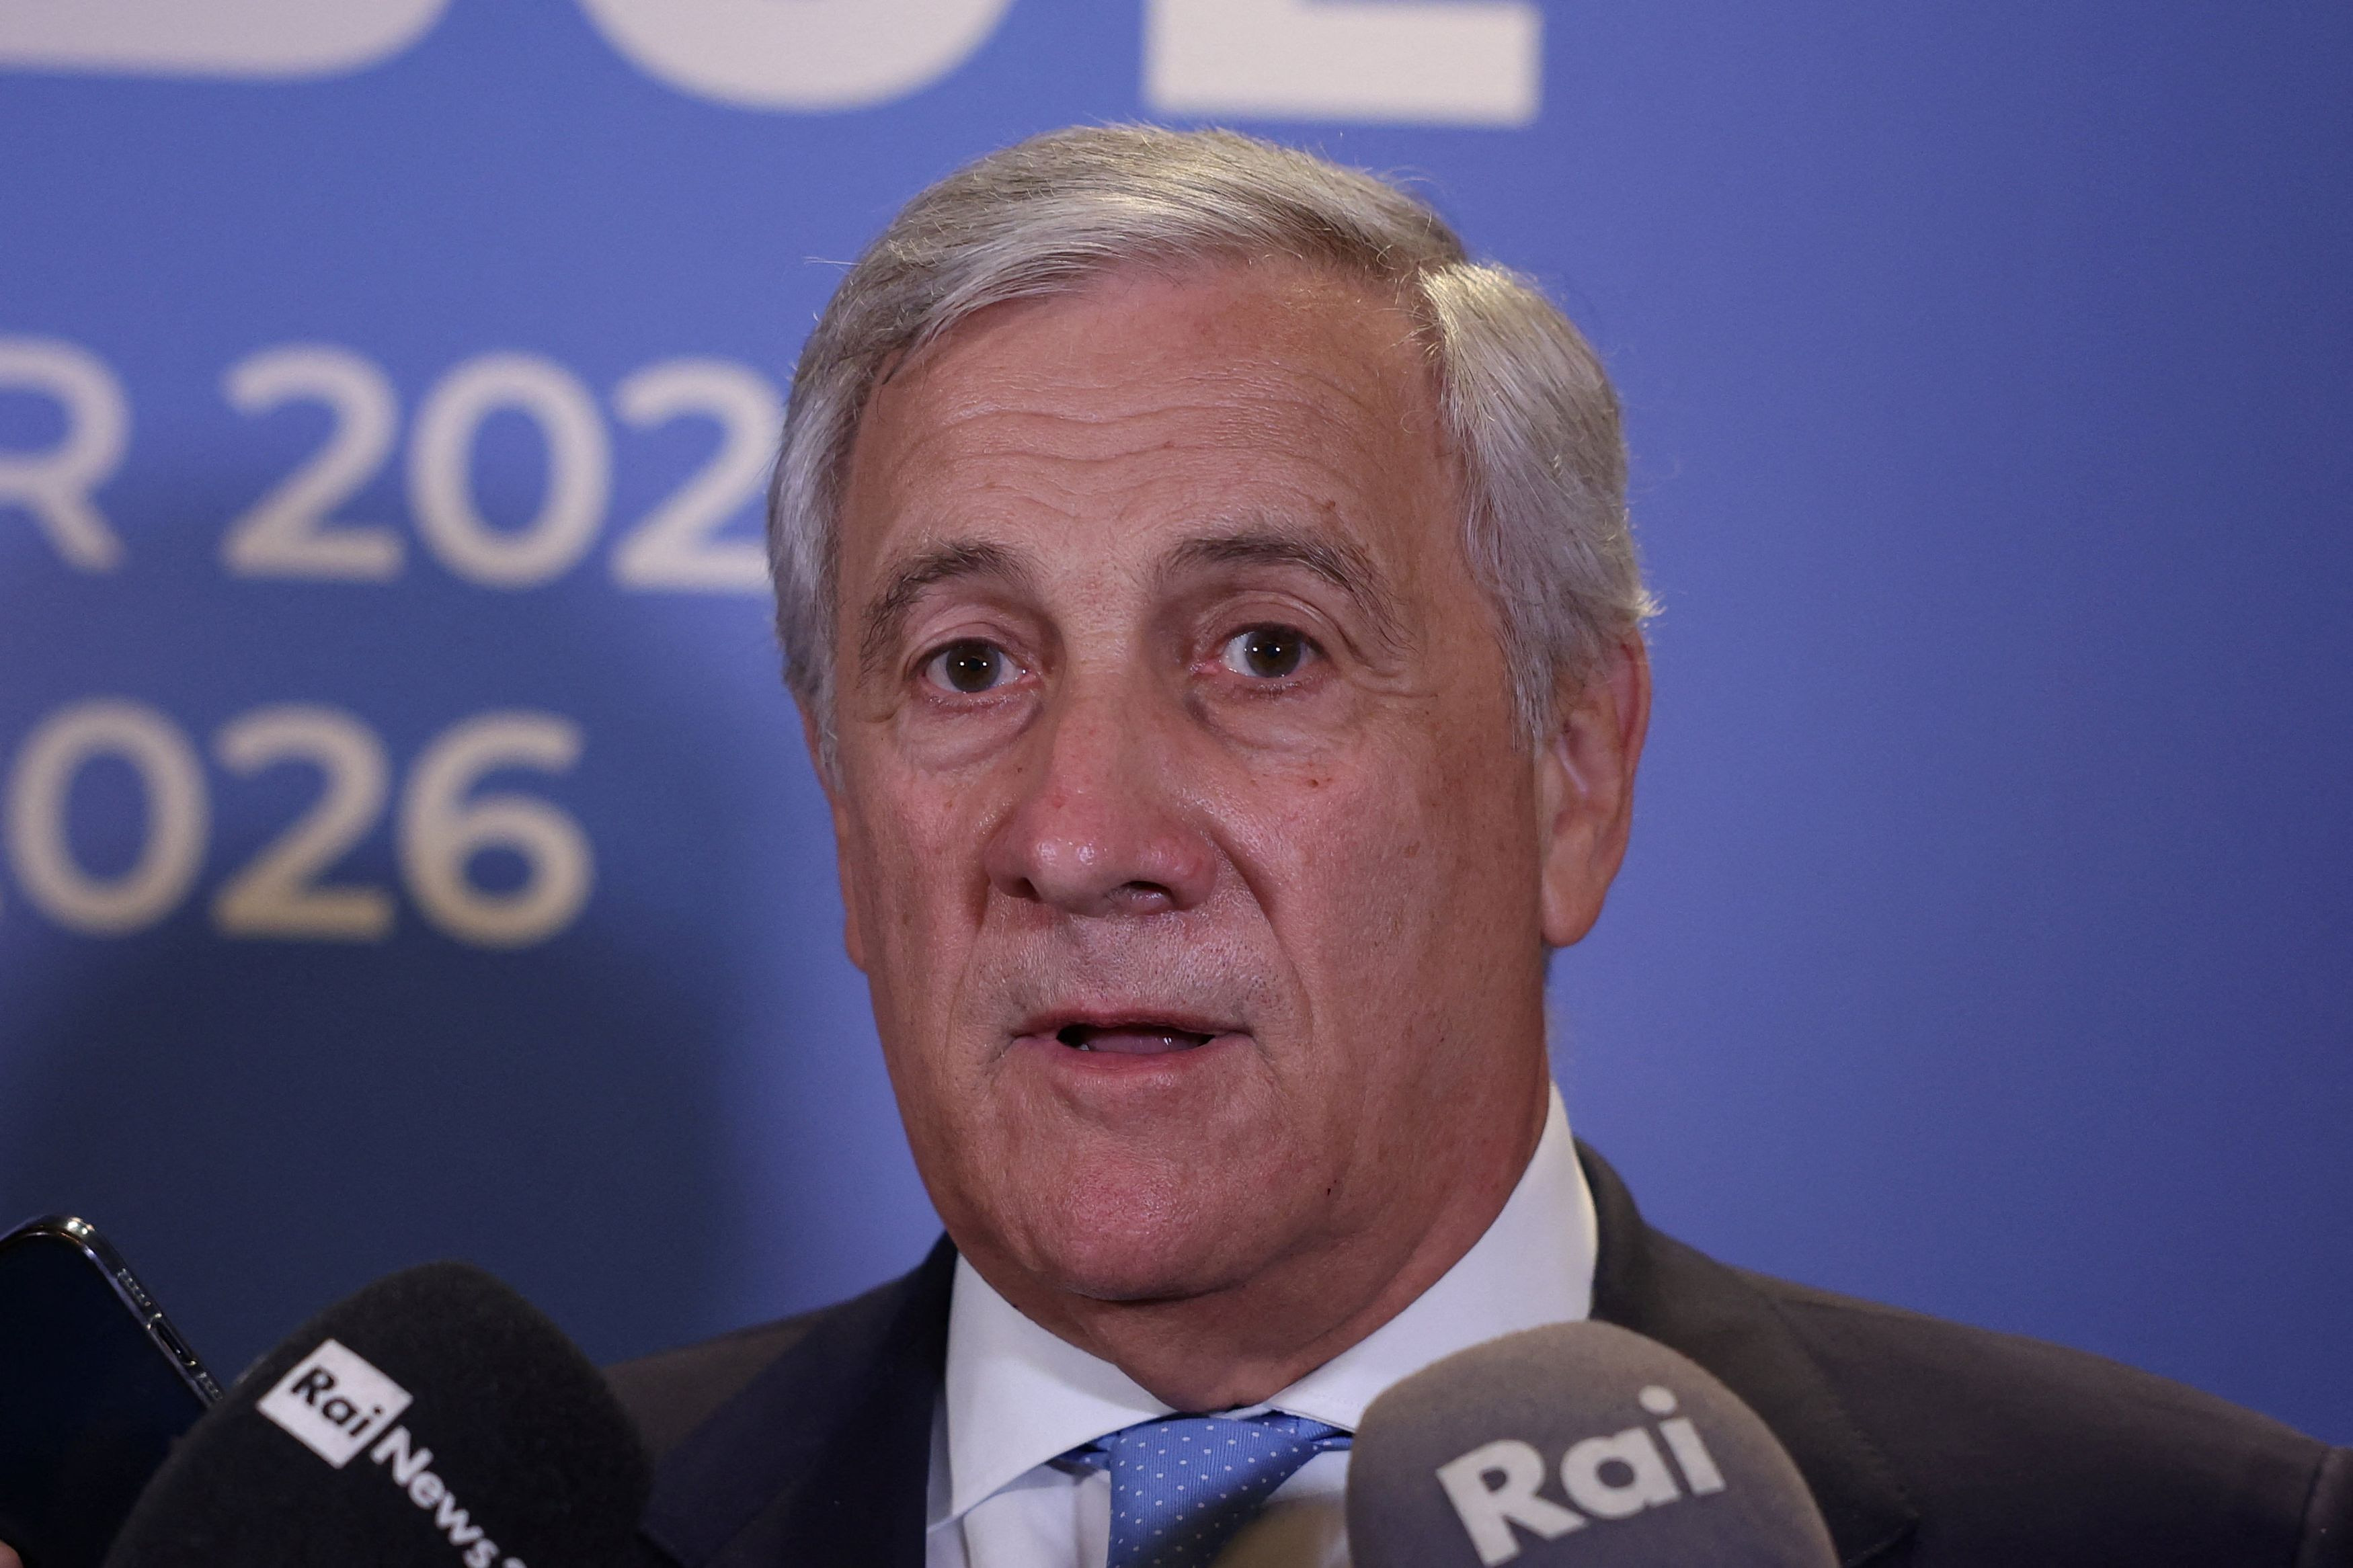
Italian Foreign Minister Antonio Tajani announced that his personal data has been leaked on the dark web, allegedly by pro-Russian hackers in retaliation for Italy's support of Ukraine. The hackers are reportedly offering money for additional information about him and his family. Prime Minister Giorgia Meloni expressed her support for Tajani, labeling the sale of confidential information as a serious concern. Screenshots revealed Tajani's inclusion on a list of 18 individuals deemed 'enemies of the Russian Federation,' which also includes other officials involved in cybersecurity. Italian authorities have launched an investigation into the incident, which is part of a broader wave of cyber threats across Europe. Tajani emphasized that he will not be intimidated and will continue to work on strengthening Italy's cybersecurity measures.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (11)
Following this threat?
Track Italian Foreign Ministry in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific data was leaked?
What actions are being taken by the government?
Is this incident part of a larger trend?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Coordinated Attack On October 29, 2026, Binance suffered a large cyberattack attributed to North Korean hackers known as TraderTraitor, resulting in the theft of approximately $6.3 billion in cryptocurrency. The attackers gained initial access through social engineering tactics, including a fake job offer that led to malware…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…