 Aws.Amazon
Threat Actors Exploit EKS for Compute Hijacking and Workload Modification
Article Content

- •Threat actors exploit EKS clusters by modifying workloads and deploying cryptomining containers.
- •Initial access is gained through application-layer vulnerabilities and misconfigured Kubernetes settings.
- •AWS recommends strict access controls and monitoring to mitigate risks associated with EKS exploitation.
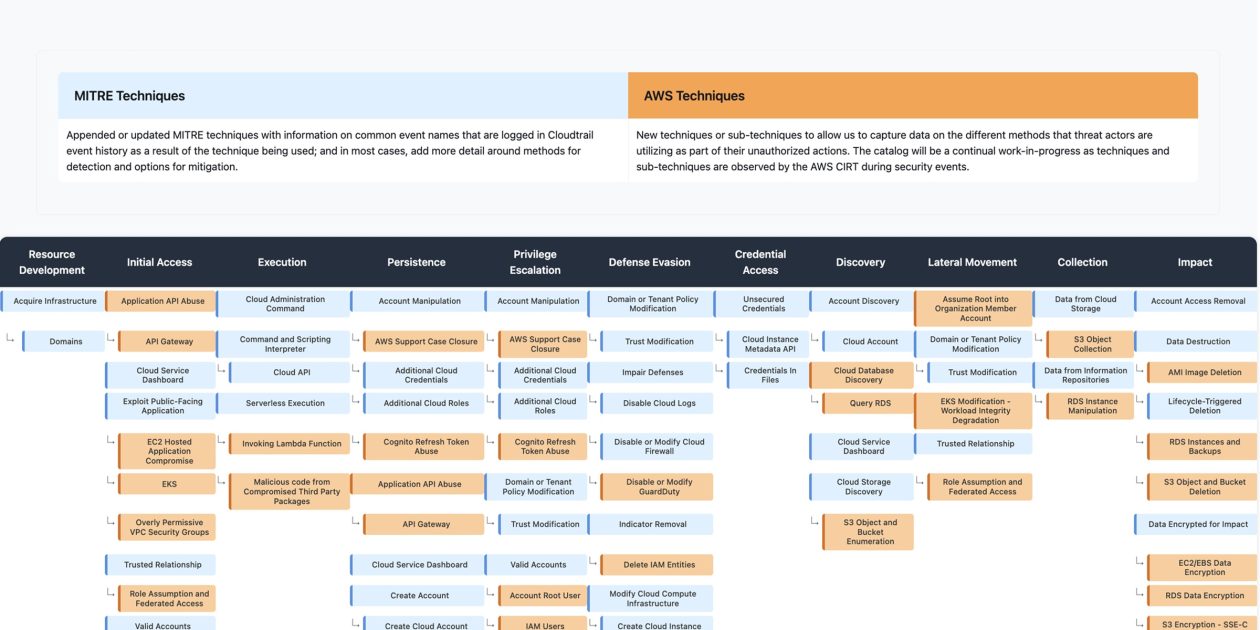
In June 2026, threat actors targeted Amazon EKS clusters by exploiting Kubernetes credentials or IAM roles to modify workloads and hijack compute resources. Attackers gained initial access through application-layer vulnerabilities, allowing them to deploy cryptomining containers and alter existing workloads. They leveraged misconfigured Kubernetes API servers and overly permissive service account tokens to escalate privileges and establish persistence. The modifications included injecting malicious code into running containers and altering cluster configurations, which could affect multiple tenants in shared environments. AWS recommends implementing strict access controls and monitoring for anomalous activities to mitigate these risks. The situation highlights the ongoing threat to cloud environments and the need for robust security measures.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track AWS in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…