
Russian Cybercriminals Launch ClickFix Campaign Targeting Hotels
Article Content
Browse articles 
Russian-linked cybercriminals are executing a ClickFix campaign aimed at European hotels and hospitality firms. Victims are receiving fake booking confirmations that deploy backdoors and infostealers onto their computers.
Ask AI about this cluster
Answers cite the sources they use
Updated 201d ago How this analysis works
More articles in this cluster (2)
Following this threat?
Track ClickFix in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Russia's AI-Driven Cyber Espionage Targets Ukraine and Europe A Russian-linked hacking group, identified as GTG-20006, has utilized Anthropic's Claude AI to automate cyber espionage against over 20 organizations, primarily in Ukraine and Europe. The group targeted Ukrainian government officials, military personnel, and drone manufacturers through sophisticated phishing and…
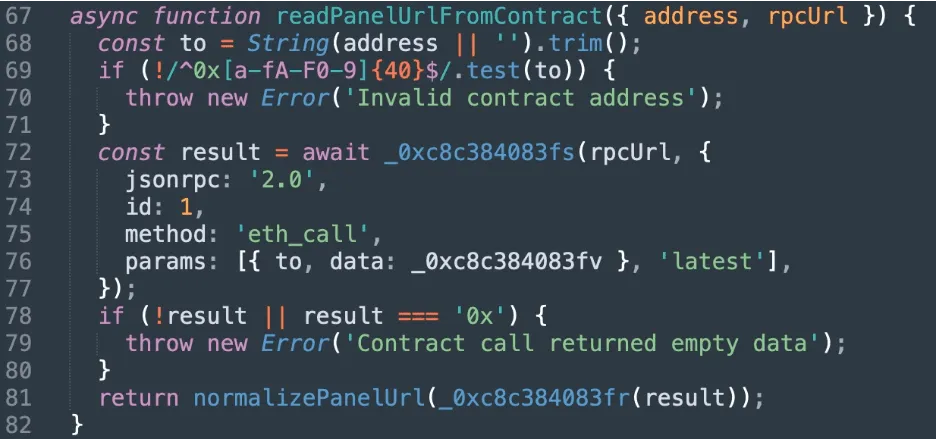 New ChainScript RAT Exploits ClickFix Lures with Blockchain C2 A newly discovered Node.js remote access trojan (RAT) named ChainScript is being deployed through ClickFix social engineering tactics, targeting Windows systems. The malware utilizes a unique command-and-control (C2) discovery method by querying a Polygon blockchain smart contract to dynamically rotate its server…