 Samsungmagazine.Eu
Samsung October 2026 Security Patch Addresses 83 Vulnerabilities
Article Content

- •Samsung's October patch fixes 83 vulnerabilities, including nine critical ones.
- •Key vulnerabilities include CVE-2026-20519 and CVE-2026-20520, both rated high severity.
- •Users can check for the patch under 'SMR Oct-2026 Release 1' in settings.
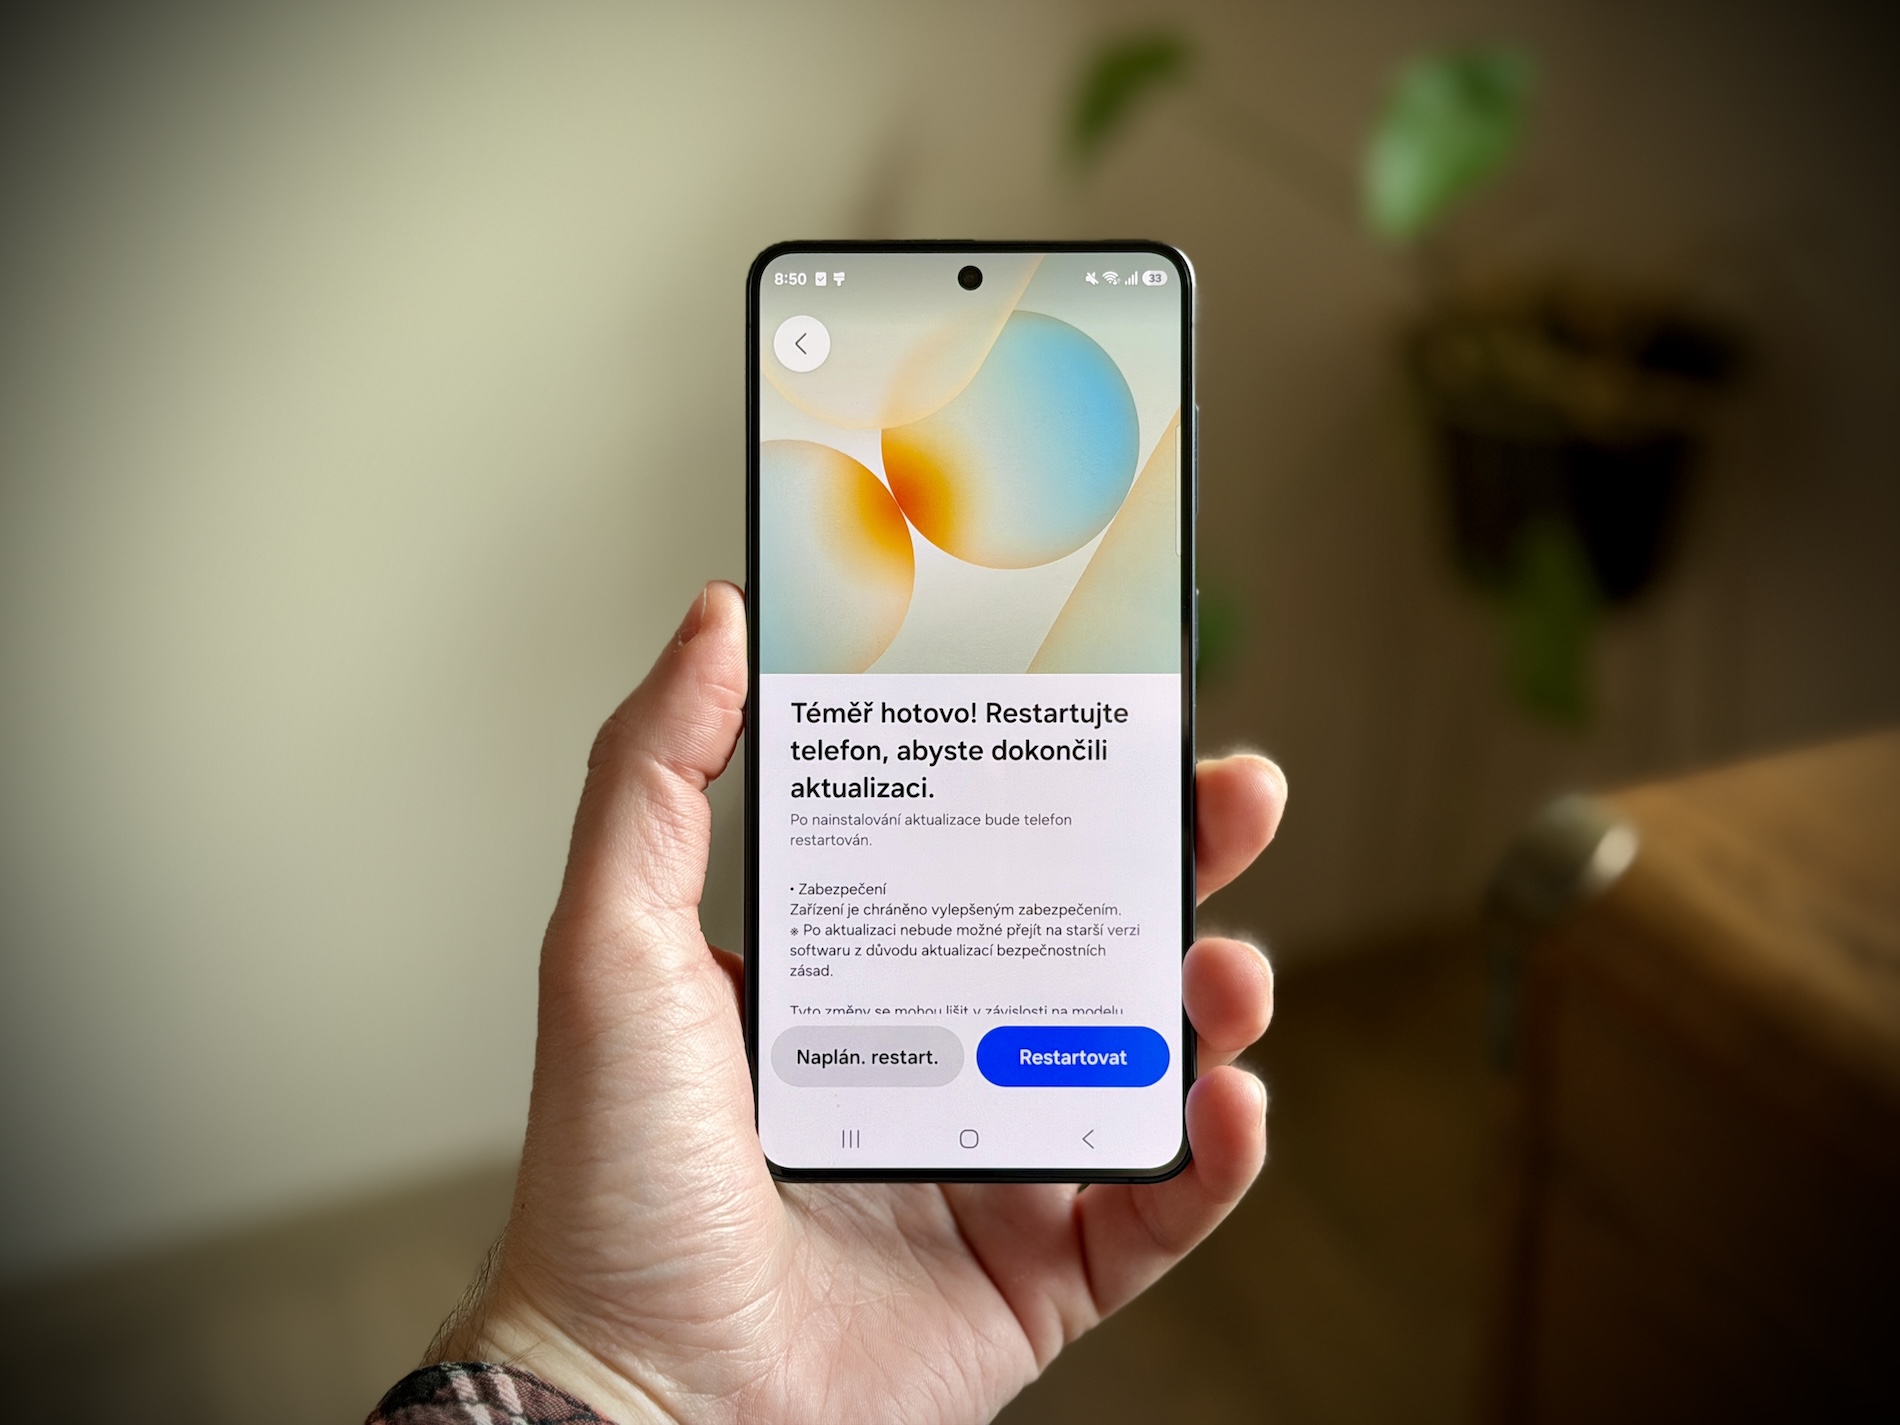
Samsung has released its October 2026 Security Maintenance Release, addressing a total of 83 vulnerabilities, including nine rated as. The vulnerabilities include CVE-2026-20519 and CVE-2026-20520, both published on October 5, 2026. Additionally, the patch includes 33 high-severity and three moderate-severity fixes. Samsung Semiconductor has added four high-severity patches for its proprietary chipsets. The vulnerabilities primarily affect devices running Android versions 14 through 17. Users can verify the patch by checking for 'SMR Oct-2026 Release 1' in their settings. The rollout will begin with flagship devices, particularly the Galaxy S lineup, before expanding to other models. Samsung has also disclosed 27 Samsung Vulnerabilities and Exposures (SVE), detailing 13 of them with six rated high severity.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track CVE-2026-20519 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which devices are affected by the vulnerabilities?
How can I check if my device is patched?
What should I do if I haven't received the update?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…