 Thehackernews
Silent Lynx Targets CIS Governments via WinRAR Exploit
Article Content

- •Silent Lynx has targeted CIS government organizations using a WinRAR exploit.
- •The campaign has been active from June 2025 to August 2026, affecting nine countries.
- •CVE-2025-8088 is actively exploited, enabling remote access via custom reverse shells.
The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating remote access. The campaigns have affected entities in nine countries, including Kazakhstan, Kyrgyzstan, and Russia, with phishing emails containing decoy documents related to diplomatic and trade matters. Silent Lynx, first reported in 2025, is believed to be linked to broader operations targeting critical infrastructure in Central Asia. Cisco Talos and Recorded Future are tracking these activities under the identifiers UAT-6275 and TAG-193. The threat actor has been active since at least 2020 and is suspected to have connections with other clusters like YoroTrooper. As of now, the exploitation of the WinRAR flaw is confirmed in the wild.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Silent Lynx, PickleShell and Fortinet in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is CVE-2025-8088?
Who is affected by these attacks?
What should organizations do to protect themselves?
Continue Reading
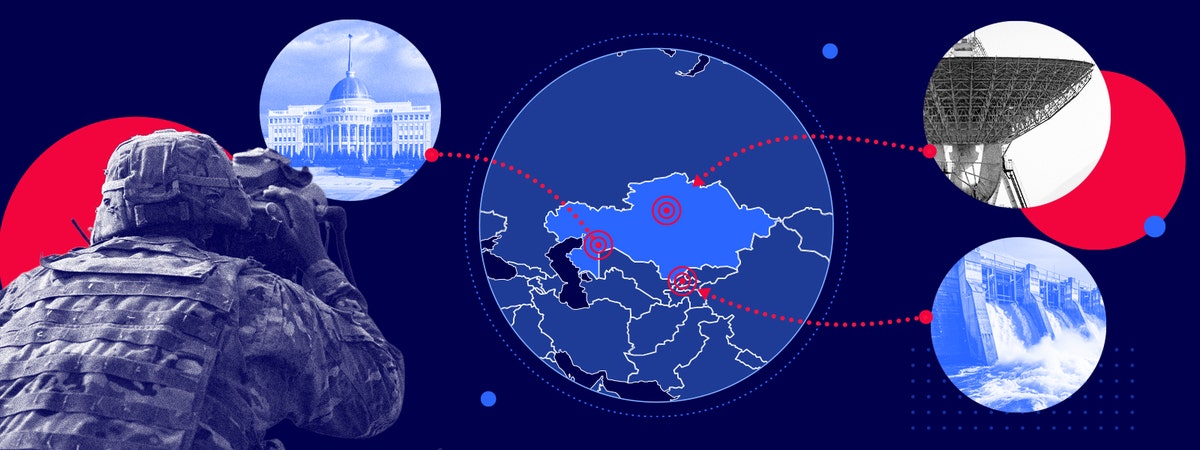 TAG-193 Targets Central Asian Governments in Espionage Campaign TAG-193 has been linked to a series of espionage operations targeting government institutions in Russia, Tajikistan, Belarus, Armenia, and Uzbekistan from early 2025 to May 2026. The group utilized spearphishing tactics, including compromised accounts and malicious documents, to gain access to sensitive information…
 Kazakhstan-Linked Hackers Target Russian Oil Refinery and Government Researchers identified a hacking group named Silent Lynx, likely based in Kazakhstan, that targeted the Orsk Oil Refinery and the Nizhny Novgorod city government in Russia. The group employed spear-phishing tactics, using seemingly important attachments to compromise their targets. The Orsk refinery had already been…