Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
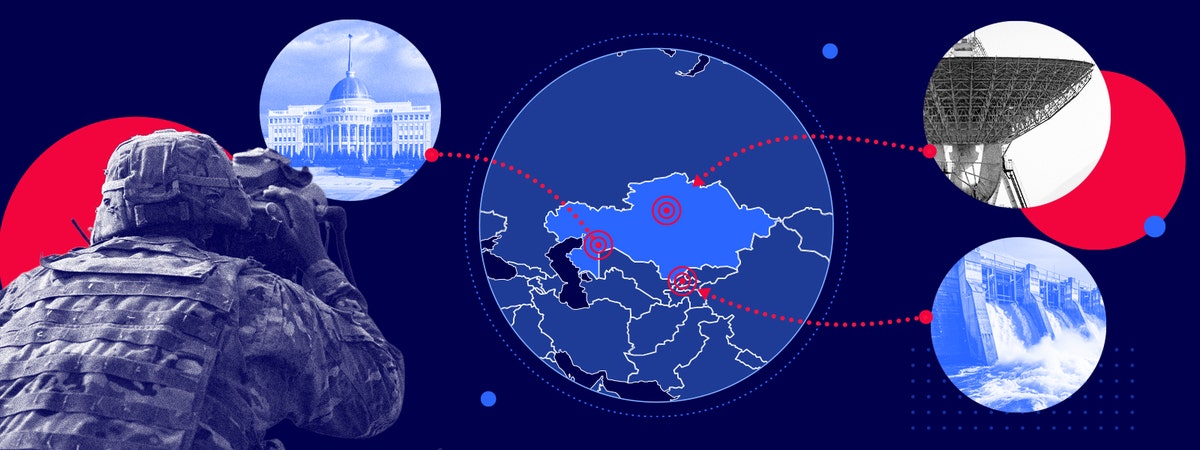
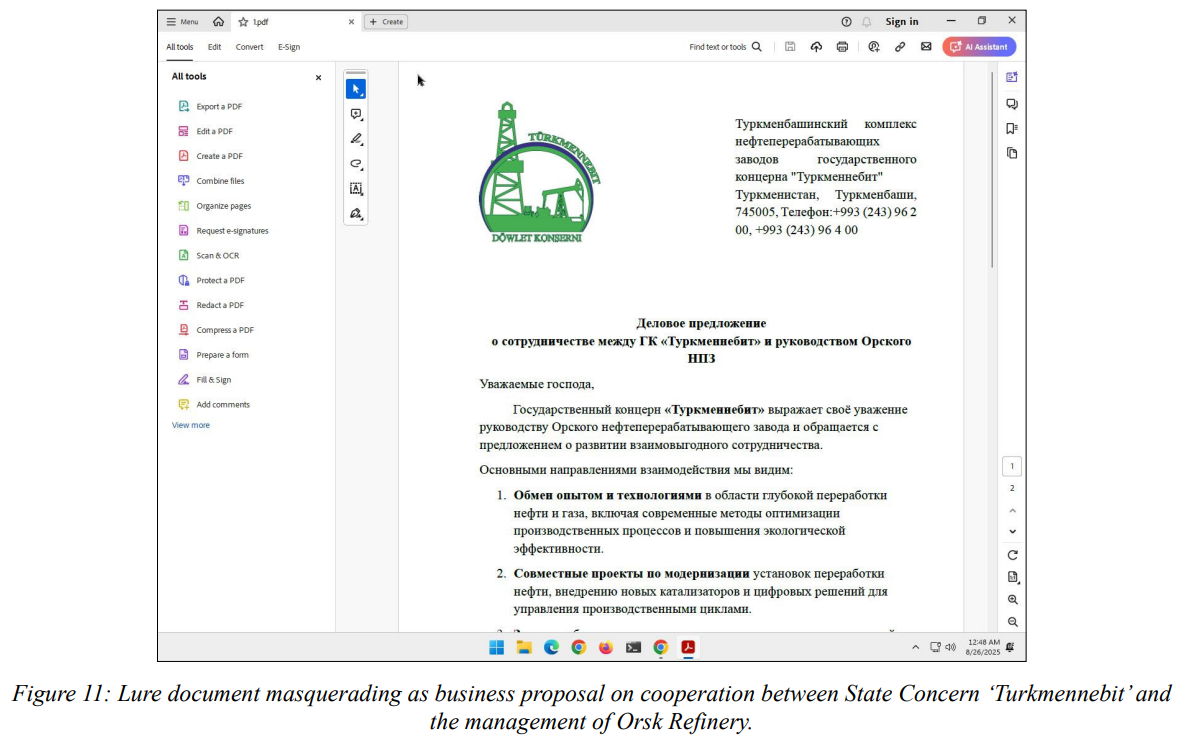
The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell,...
Gamaredon, a Russian state-backed APT group, is actively exploiting a WinRAR vulnerability (CVE-2025-8088) to deploy malware against Ukrainian government and military targets. The attack begins with a spearphishing email containing a malicious HTML Application payload known as GammaPhish, which retr...
Two Russia-aligned cyber campaigns are exploiting the WinRAR vulnerability CVE-2025-8088 against Ukrainian targets nearly a year after it was patched. The flaw, a path traversal vulnerability, allows attackers to write files outside the extraction directory using NTFS Alternate Data Streams. Victims...
A critical server-side template injection (SSTI) vulnerability in FOSSBilling, tracked as CVE-2026-28496, was disclosed on June 23, 2026. This flaw affects all versions up to 0.7.2 and allows attackers to exploit unsafe Twig template rendering, leading to full database compromise and remote code exe...