 Iol.Co.Za
South African Personal Data Sold on Dark Web Amid Rising Breaches
Article Content

- •Over 453,000 job seekers' records are being sold on the dark web.
- •The Gentlemen and LockBit are the primary ransomware groups involved.
- •The Information Regulator has received more than 8,000 breach notifications in 2026.
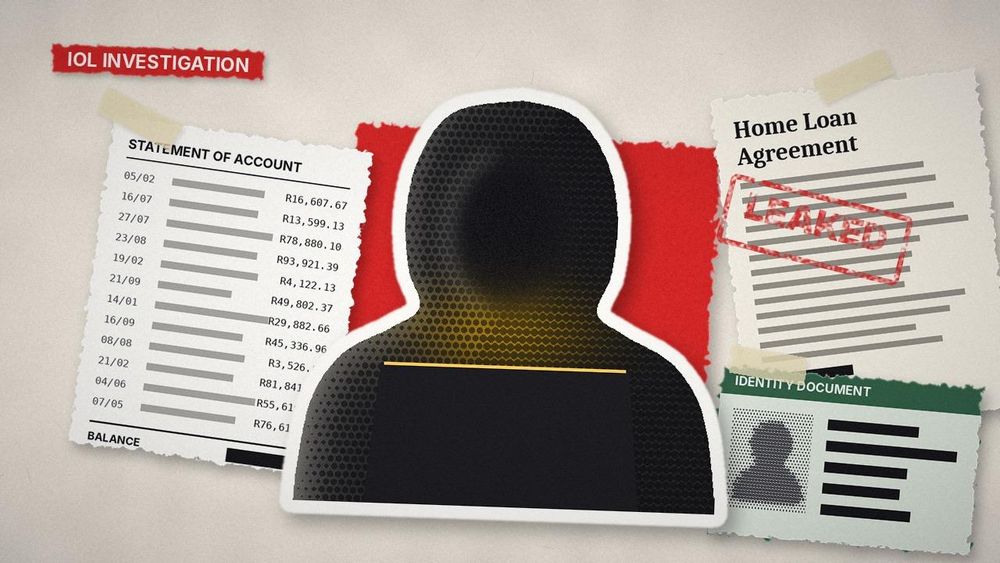
A significant amount of South African personal data, including bank statements and loan agreements, is being traded on the dark web, with one batch of 453,362 job seekers' records listed for R34,000. The Gentlemen hacking group has targeted a Toyota dealership in Mpumalanga, while LockBit has leaked confidential documents from various organizations, including a law firm and a local municipality. The Information Regulator has received over 8,000 breach notifications this year. The recent victim, Lydenburg Toyota, is currently under investigation for a ransomware incident. Cybersecurity experts warn that the lack of skilled investigators hampers efforts to track these cybercriminals. The Gentlemen has been identified as the second most active ransomware group globally this year, according to Check Point Research.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Lockbit, The Gentlemen Hacking Group and ANC in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What types of data are being sold?
How many organizations have reported breaches?
What is being done about these breaches?
Continue Reading
 SAP Exploits Surge: Days to Zero Report Highlights Critical Vulnerabilities A report from Onapsis Research Labs and Recorded Future reveals that the median time from the release of a SAP Security Note to the first public exploit has drastically decreased to 1-3 days, down from 489 days in 2021. The report analyzed over 1.2 million events and noted a 123% increase in underground discussions…
 Ransomware Groups Exploit PAN-OS Flaw, Target Critical Infrastructure Ransomware groups, including Qilin and INC, are exploiting a critical authentication bypass vulnerability (CVE-2026-0257) in Palo Alto Networks' PAN-OS GlobalProtect and Prisma Access. This flaw allows attackers to establish unauthorized VPN sessions, bypassing multifactor authentication controls. Since its disclosure…