 Security-Storage-Und-Channel-Germany.De
SAP Exploits Surge: Days to Zero Report Highlights Critical Vulnerabilities
Article Content

- •Median time to exploit SAP vulnerabilities has dropped to 1-3 days.
- •Over 30 ransomware groups are now targeting SAP systems.
- •CVE-2025-31324 was actively exploited shortly after its disclosure.
A report from Onapsis Research Labs and Recorded Future reveals that the median time from the release of a SAP Security Note to the first public exploit has drastically decreased to 1-3 days, down from 489 days in 2021. The report analyzed over 1.2 million events and noted a 123% increase in underground discussions targeting SAP applications between 2023 and 2025. The rise in ransomware groups targeting SAP systems has been significant, with 30+ distinct groups identified. A critical vulnerability, CVE-2025-31324, was within weeks of its disclosure, leading to over 1,200 exposed instances. The report emphasizes the urgent need for organizations to enhance their SAP security measures as exploitation becomes increasingly rapid and sophisticated.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Akira, SAP and CVE-2025-31324 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the significance of CVE-2025-31324?
How quickly are SAP vulnerabilities being exploited?
What should organizations do to protect against these threats?
Continue Reading
 Ransomware Attack on Paylogix Exposes Data of 41K Individuals Paylogix LLC reported a ransomware incident affecting the protected health information of 41,739 individuals. The breach occurred between November 13 and November 18, 2025, when an unauthorized third party accessed its network. Data compromised includes Social Security numbers, dates of birth, and health insurance…
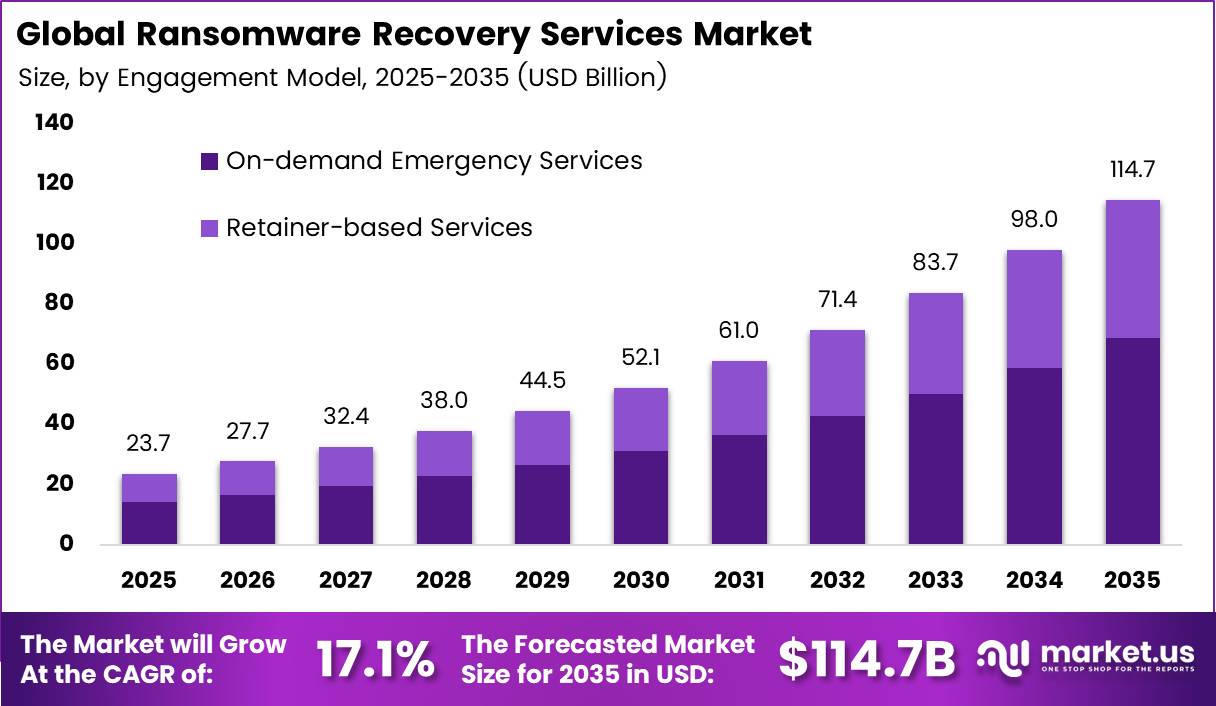 Ransomware Attacks Surge 50% in Q3 2026 Amid Rising Recovery Service Demand Ransomware attacks have increased by over 50% year-over-year, with 2,894 incidents reported in Q3 2026, up from 1,933 in Q3 2025, according to NordLayer. This surge follows the takedown of several major ransomware groups, including LockBit and RansomHub, suggesting a shift in the threat landscape. New groups like The…