 cyberstrategyinstitute.com
Surge in Vulnerability Disclosures Amidst Low Exploitation Rates
Article Content

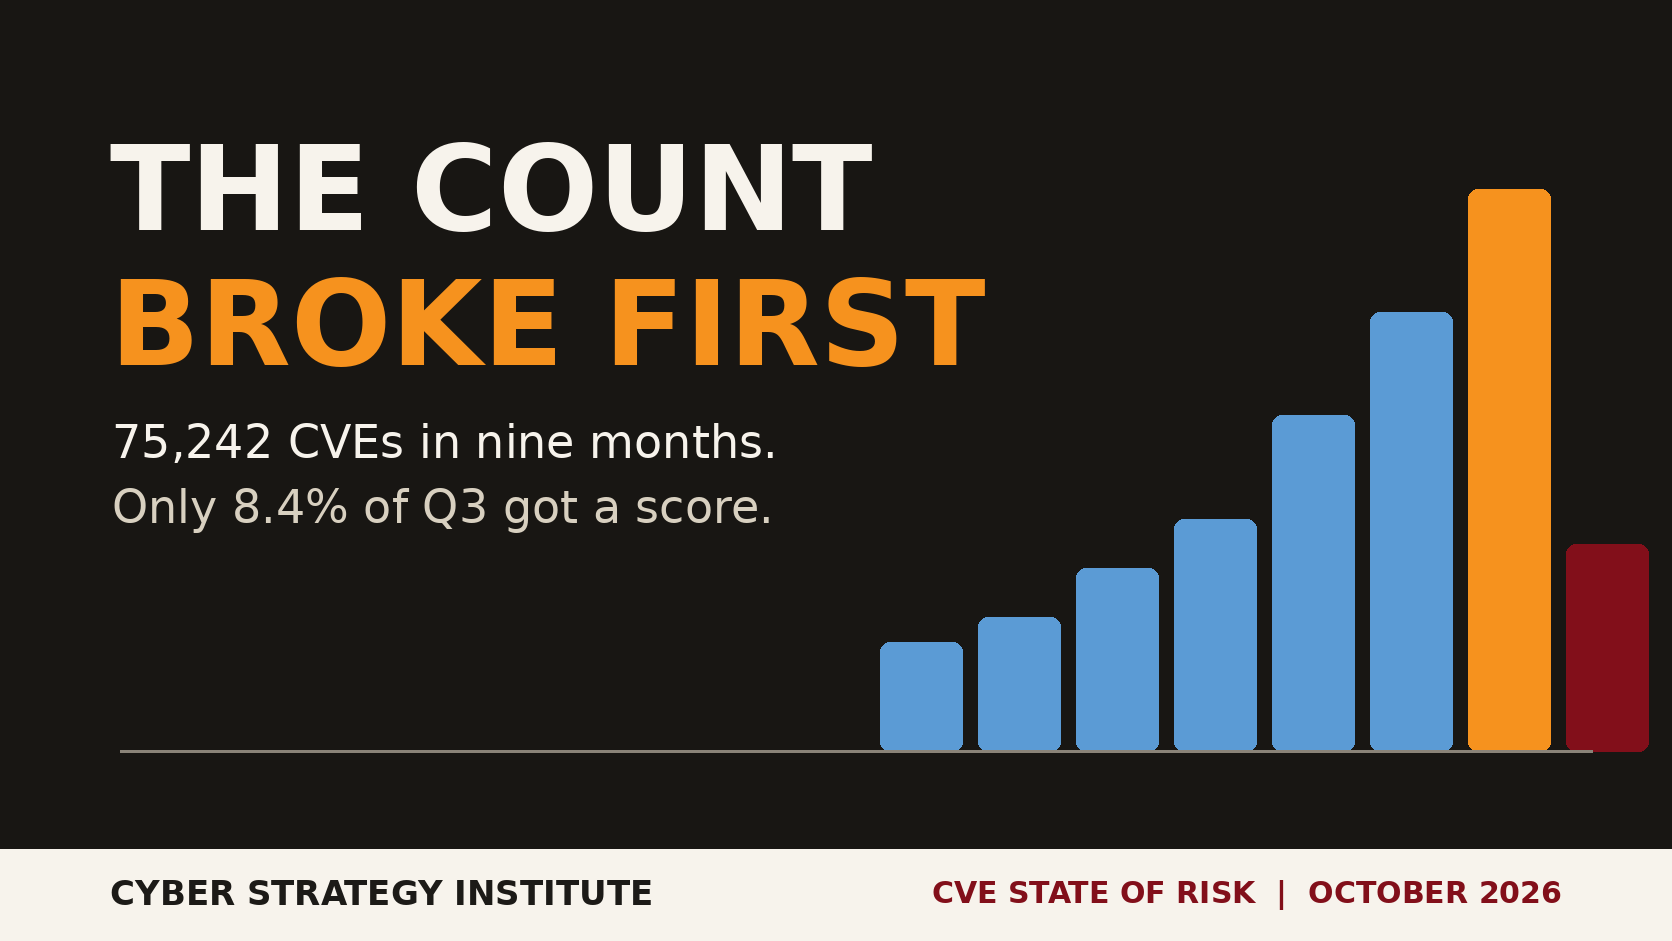
- •Vulnerability disclosures have tripled in 2026, with 83,167 CVEs published by October 19.
- •Only 696 of these vulnerabilities have been confirmed exploited, indicating a low exploitation rate.
- •CVE-2026-104935 and CVE-2026-96951 are actively exploited and listed in CISA's KEV catalog.
In 2026, vulnerability disclosures have surged, with 83,167 CVEs published by October 19, a 73% increase from 2025. However, only 696 of these vulnerabilities have been exploited, indicating a troubling ratio of one in 119. Notably, CVE-2026-104935 and CVE-2026-96951, both published on October 13, have been added to the CISA KEV list due to confirmed. The trend shows that while the number of disclosed vulnerabilities has tripled, the rate of exploitation is declining, with September's figures showing under four exploited CVEs per 1,000 published. This discrepancy raises questions about the actual risk posed by the growing number of vulnerabilities. Security teams face challenges in prioritizing which vulnerabilities to address, as many older vulnerabilities remain unexploited despite being publicly disclosed.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track CVE-2026-104935 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the CVSS scores for the recent CVEs?
How many vulnerabilities have been exploited this year?
What should organizations prioritize in their patching strategy?
Continue Reading
 Critical Vulnerabilities in AhsayCBS Allow Remote Code Execution CVE-2026-105133 and CVE-2026-105134 affect AhsayCBS, enabling attackers to bypass authentication and execute remote code. CVE-2026-105133, with a CVSS score of 7.3, allows unauthenticated access to JSON API actions. CVE-2026-105134, rated 10.0, enables path traversal in the replication receiver's file upload service…
 Critical Cisco Secure Email Gateway Vulnerability Exploited Cisco has disclosed a critical vulnerability in its Secure Email Gateway (SEG), tracked as CVE-2026-76519, which allows unauthenticated remote attackers to execute commands with root privileges. This flaw arises from improper handling of email attachments when the File Reputation service is enabled. Active…