 United24Media
Ukrainian Hackers Expose Russian Naval Secrets in Operation Poseidon
Article Content

- •Ukrainian Militant's Operation Poseidon breached Russian naval files, revealing 70 projects.
- •The leaked data includes sensitive technical documentation on submarines and naval systems.
- •The scale of the breach and the authenticity of the data remain unverified by independent sources.
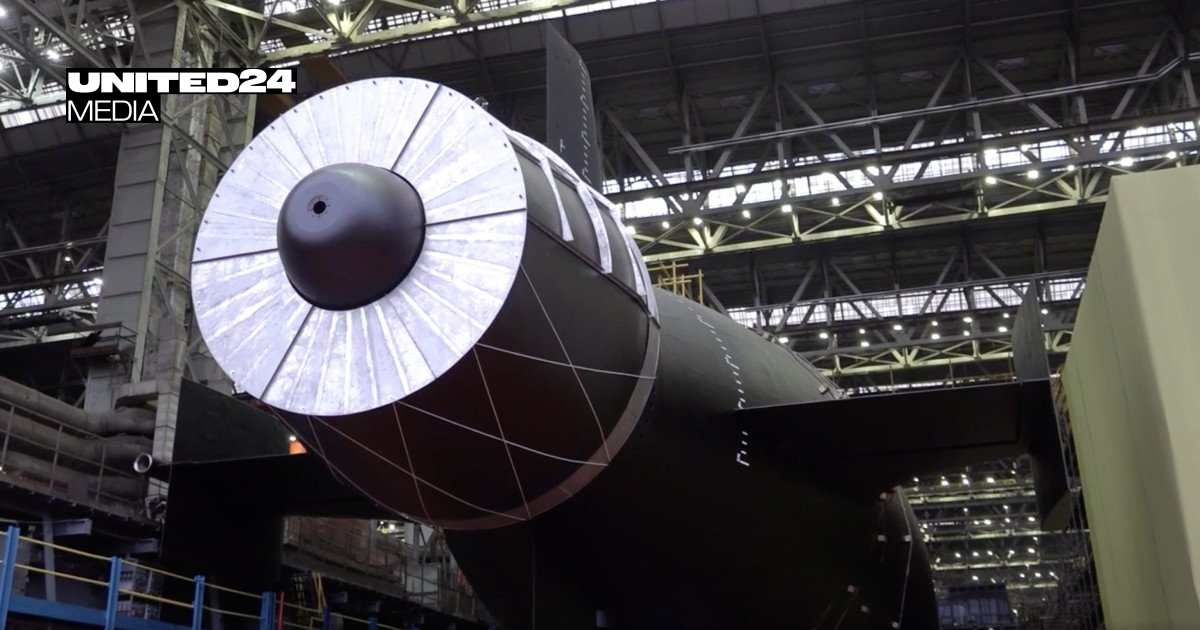
Ukrainian hackers from the group Ukrainian Militant executed a cyber operation named 'Poseidon,' breaching Russian naval files and obtaining sensitive documentation from 70 projects. The compromised data includes technical details related to submarines, warships, and various naval technologies, some marked as 'secret' and 'top secret.' The hackers claimed to have accessed information on nuclear-powered submarines, frigates, and advanced systems for underwater vehicles. The operation's scale and the authenticity of the leaked data have not been independently verified, with some documents analyzed by InformNapalm confirming only a fraction of the claims. The breach raises concerns about the operational security of Russian military and defense enterprises, as the full extent of the data obtained remains unknown. The operation follows previous significant leaks involving Russia's defense industry, indicating a pattern of targeted cyber operations against Russian military assets.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Ukrainian Militant, Poseidon and Elektropribor Central Research Institute in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…