 Theregister
US Air Force Pilots Used Malware-Laden USB Drives for Mission Planning
Article Content

- •US Air Force pilots used malware-laden USB drives for mission planning.
- •Malware is suspected to be linked to state-sponsored actors from Iran, Russia, and China.
- •No public evidence has been provided to confirm the attribution of the malware.
US Air Force pilots reportedly utilized USB drives containing malware to plan missions in Afghanistan. The malware is believed to have originated from state-sponsored actors, with potential links to Iran, Russia, and China, although no public evidence has been provided for this attribution. The incident raises concerns about the security of military operations and the potential for sensitive information to be compromised. The exact scope of the malware's impact and the number of affected systems remain unclear. The Air Force has not confirmed the details of the incident, and further investigation is ongoing.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Shai-hulud and Anthropic in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What type of malware was used?
How many pilots were affected?
What actions are being taken in response?
Continue Reading
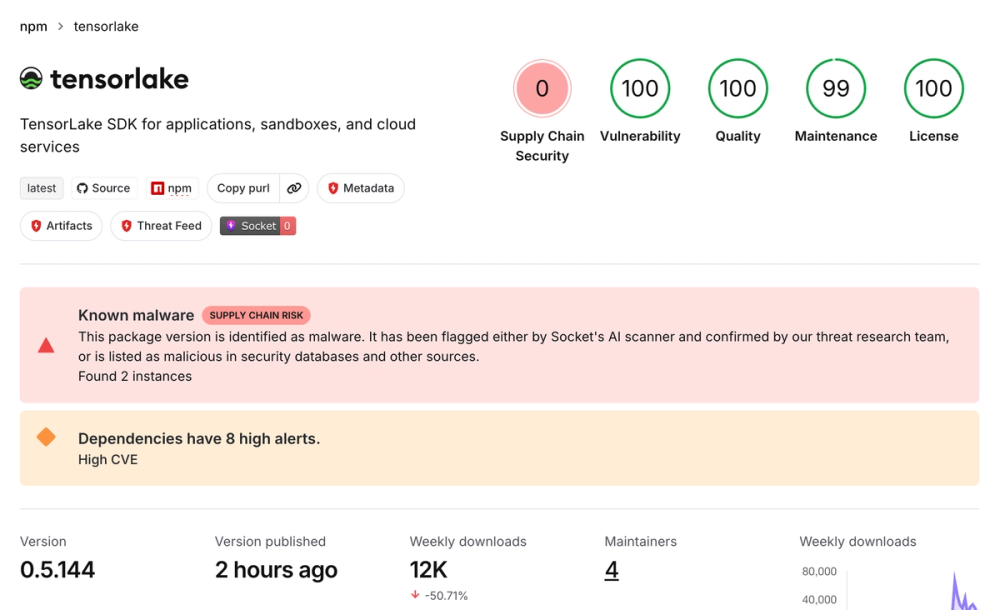 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Cisco Email Bug Exploited as Zero-Day by Unknown Actors A zero-day vulnerability in Cisco's email system has been by unknown criminals. The flaw, described as a 'make-me-root' bug, allows attackers to gain root access via email. Cisco has not disclosed specific details about the vulnerability or the affected systems. The exploit is reportedly being used in the wild…