 Kyivpost
Zaporizhzhia Nuclear Plant Faces 16th Blackout, Relying on Diesel Generators
Article Content

- •The Zaporizhzhia Nuclear Power Plant lost external power for the 16th time in 2026.
- •Backup diesel generators are now the sole power source for safety-critical systems.
- •Energoatom warns of severe risks associated with reliance on diesel generators.
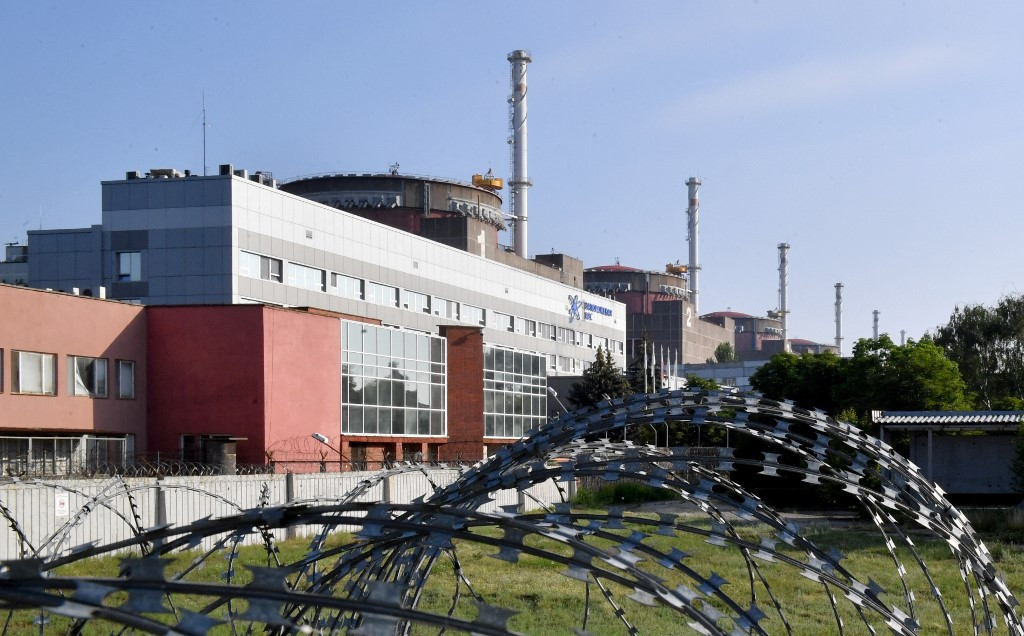
On November 8, 2026, the Zaporizhzhia Nuclear Power Plant lost its external power supply for the 16th time this year, forcing it to switch to emergency diesel generators. The disconnection occurred at 2:36 a.m. local time due to damage to the Ferosplavna-1 power line, which is critical for maintaining reactor cooling and safety systems. The Russian-installed management stated that backup generators are currently supplying power to essential equipment, and radiation levels remain reported as normal. However, Energoatom, Ukraine's state nuclear operator, warned that reliance on diesel generators poses significant risks, including potential equipment failure and cooling degradation. The ongoing conflict has led to repeated power outages, raising concerns about the plant's nuclear safety. The situation is exacerbated by declining water levels in the plant's cooling pond, which are critical for reactor safety. The incident highlights the vulnerability of nuclear facilities in conflict zones and the urgent need for restoring stable power supplies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (11)
Following this threat?
Track DTEK in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What caused the power outage?
How long can the plant operate on diesel generators?
What are the safety implications of this blackout?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…