Summary
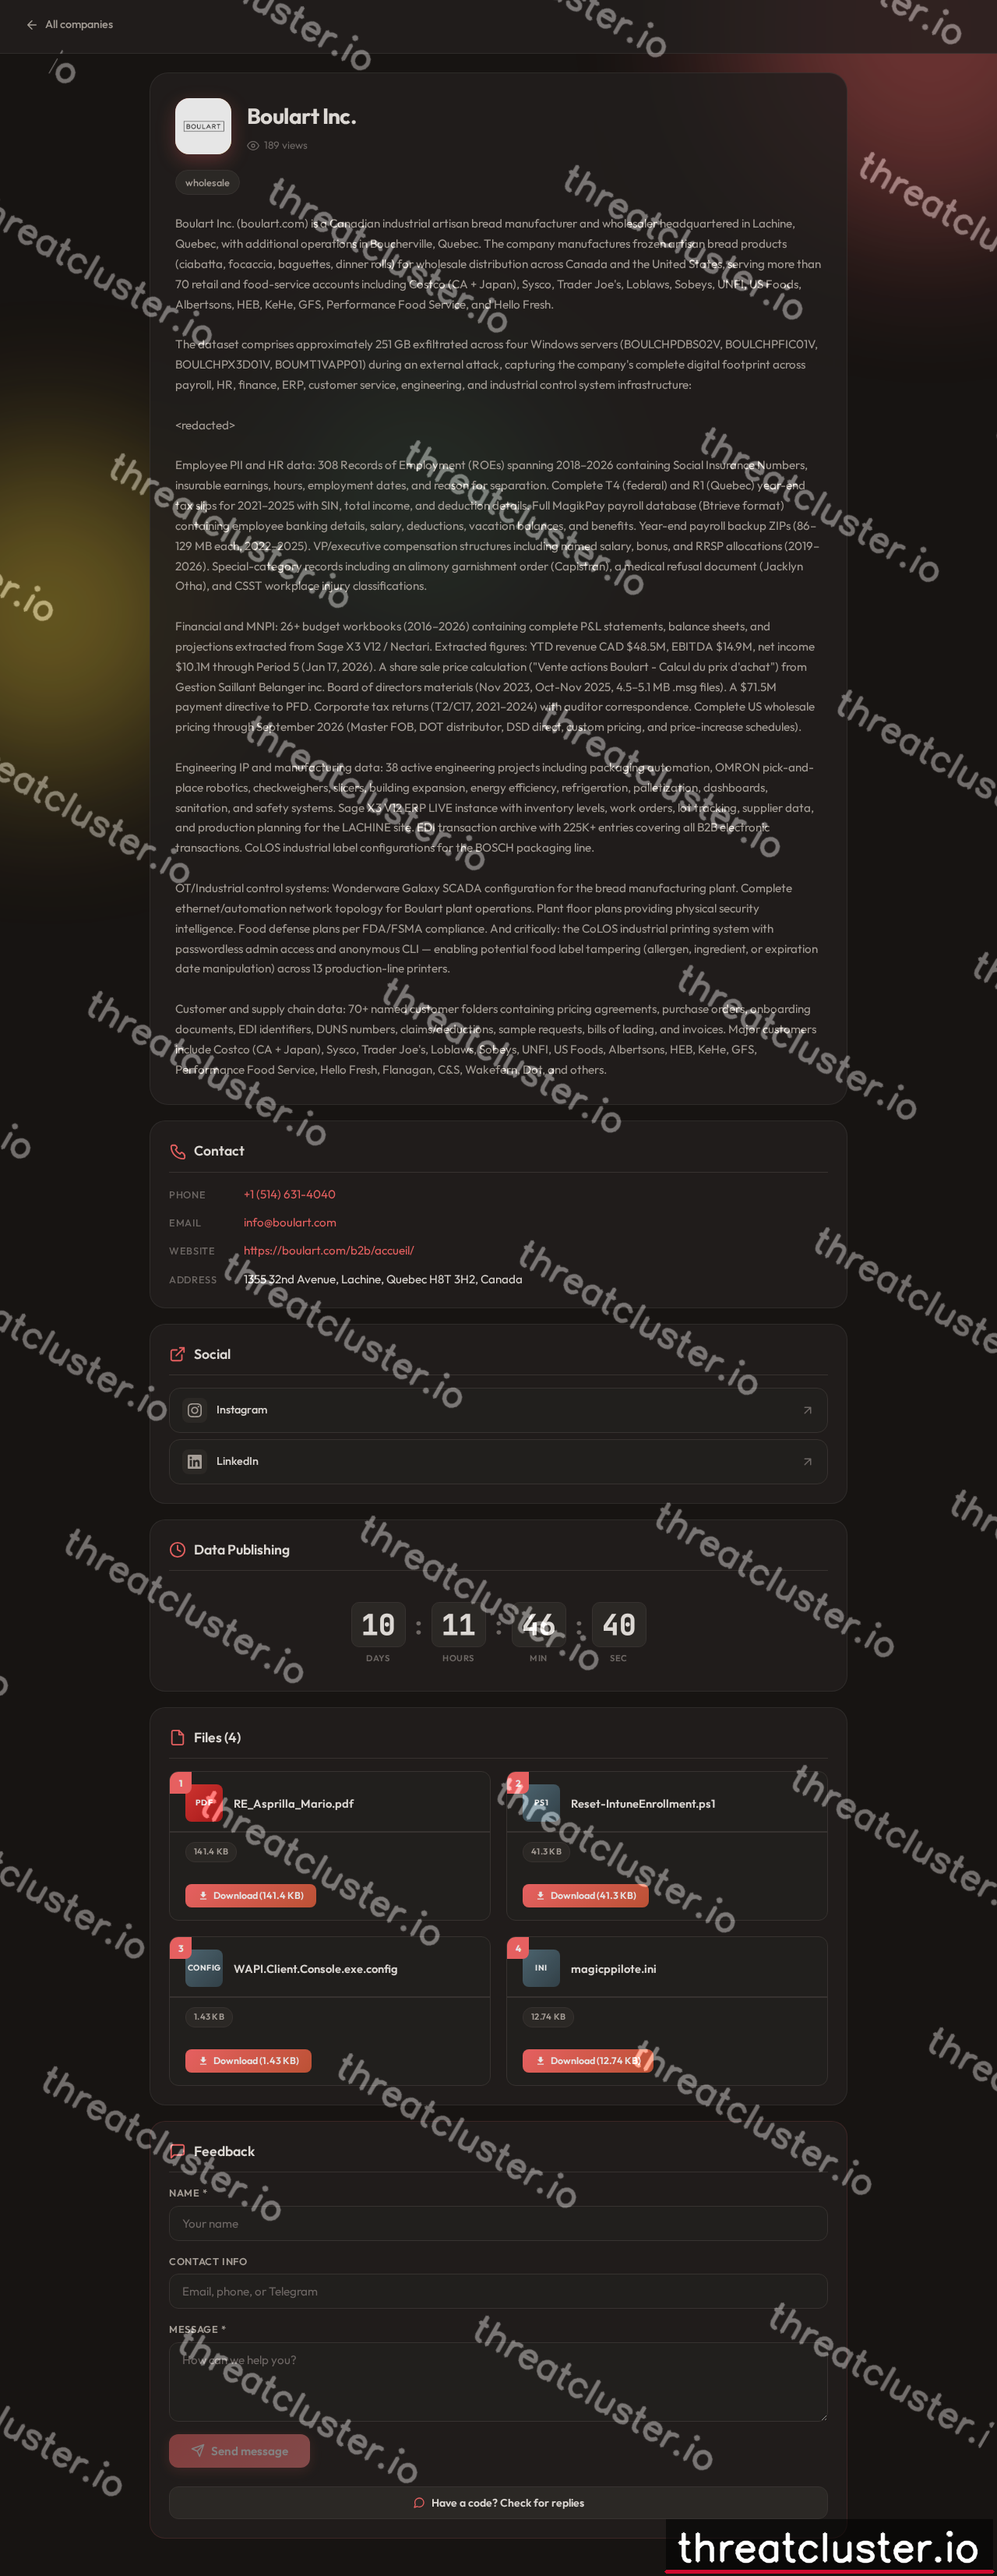
Written by ThreatClusterfrom site fields, file listing, victim profile, leak post, screenshotThe leak claims approximately 251 GB of data exfiltrated from Boulart Inc., a Canadian bakery/manufacturer, across four Windows servers during an external attack. The data categories claimed include employee PII and HR data, financial information and MNPI, engineering IP and manufacturing data, OT/ICS data, and customer and supply-chain data; sample files published include RE_Asprilla_Mario.pdf, Reset-IntuneEnrollment.ps1, WAPI.Client.Console.exe.config and magicppilote.ini. The leak page is in countdown status, with publication due in 10 days.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Is something on this page wrong? Representatives of the organisation can dispute or correct this listing. Every request and its outcome is recorded on that page.
Victim profile
- Employees
- 308
- Platforms
- Sage X3 V12 ERP Nectari CoLOS industrial label configurations Wonderware Galaxy SCADA
- People named
- Capistran Jacklyn Otha
What was taken
Boulart Inc. (boulart.com) is a Canadian industrial artisan bread manufacturer and wholesaler headquartered in Lachine, Quebec, with additional operations in Boucherville, Quebec. The dataset comprises approximately 251 GB exfiltrated across four Windows servers during an external attack, capturing the company's complete digital footprint across payroll, HR, finance, ERP, customer service, engineering, and industrial control system infrastructure.
Also stated on the leak page
Fields this group publishes that do not map to a standard column. Labels are the site's own.
- [email protected]
- Phone
- +1 (514) 631-4040
- Address
- 1355 32nd Avenue, Lachine, Quebec H8T 3H2, Canada
- Files (4)
- RE_Asprilla_Mario.pdf; Reset-IntuneEnrollment.ps1; WAPI.Client.Console.exe.config; magicppilote.ini
- Data Publishing
- 10 days
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.