Summary
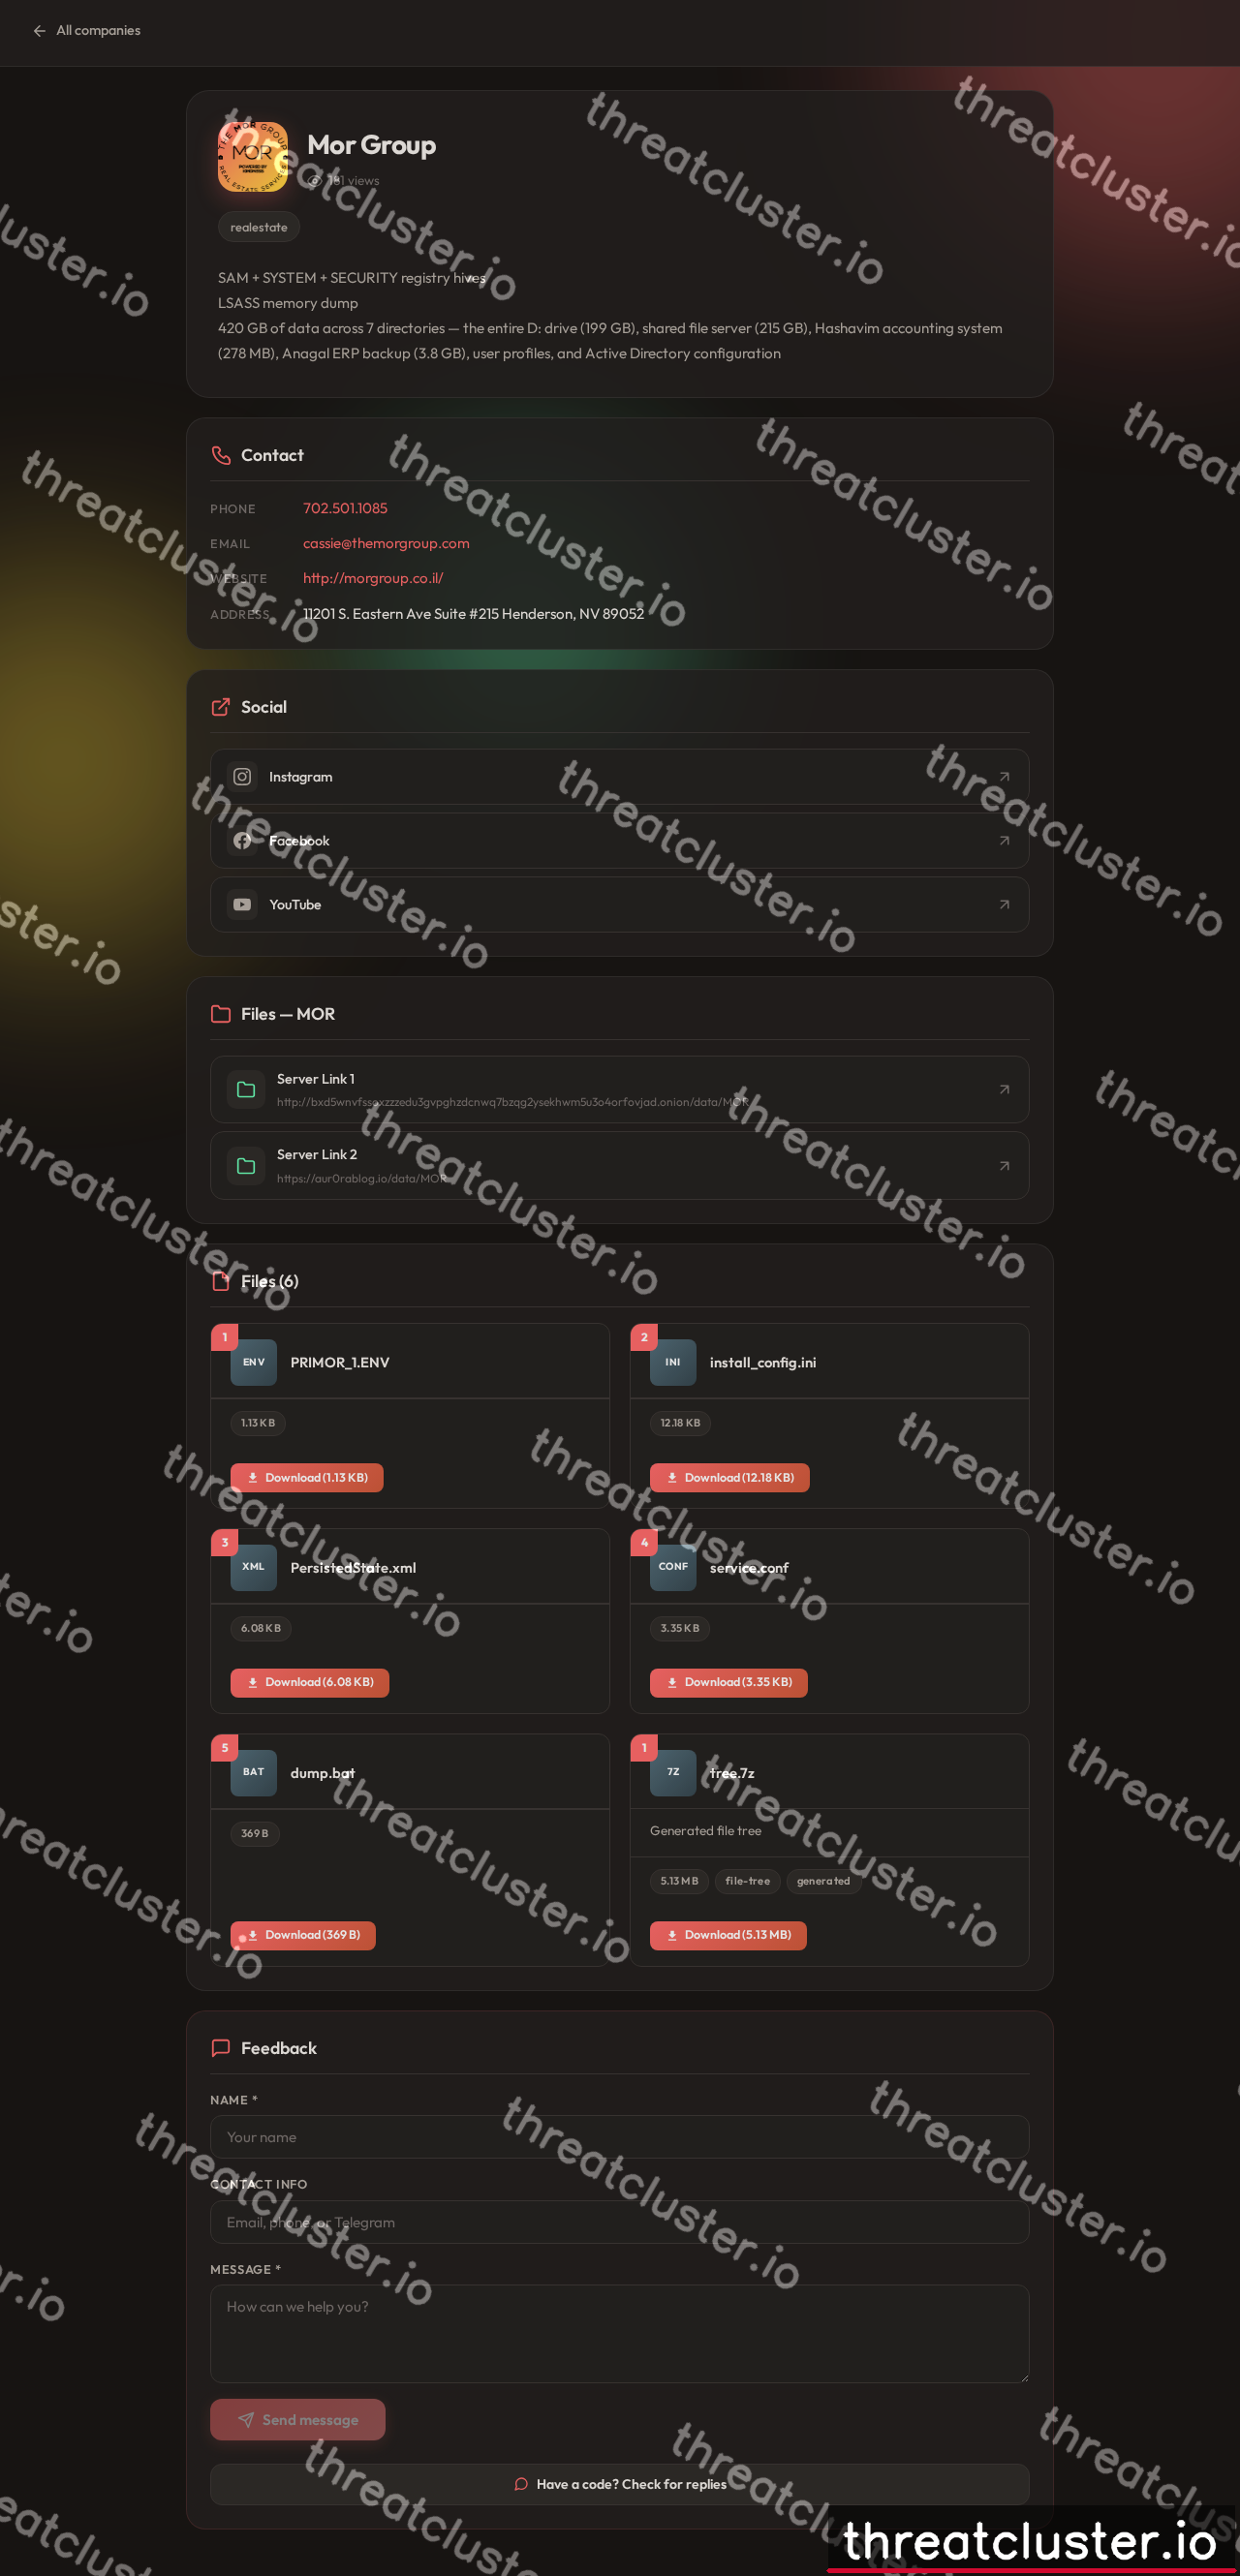
Written by ThreatClusterfrom site fields, file listing, victim profile, leak post, screenshotAurora claims Mor Group exfiltrated 420 GB of data across seven directories, including the entire D: drive (199 GB) and a shared file server (215 GB), plus Hashavim accounting data, Anagal ERP backups, user profiles, and Active Directory configuration; the set is described as including SAM, SYSTEM, and SECURITY registry hives and an LSASS memory dump. Data categories claimed include registry hives, LSASS memory dump, accounting data, ERP backups, user profiles, and Active Directory configuration; sample filenames published include PRIMOR_1.ENV, install_config.ini, PersistedState.xml, service.conf, dump.bat, and tree.7z. Mor Group is identified on the leak page with domain morgroup.co.il and is described as a real estate company; the leak post is published.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Is something on this page wrong? Representatives of the organisation can dispute or correct this listing. Every request and its outcome is recorded on that page.
What was taken
Mor Group: SAM + SYSTEM + SECURITY registry hives; LSASS memory dump; 420 GB of data across 7 directories — the entire D: drive (199 GB), shared file server (215 GB), Hashavim accounting system (278 MB), Anagal ERP backup (3.8 GB), user profiles, and Active Directory configuration.
Also stated on the leak page
Fields this group publishes that do not map to a standard column. Labels are the site's own.
- Server Link 1
- http://bxd5wnvfssoxzzzedu3gvpghzdcnwq7bzqg2ysekhwm5u3o4orfovjad.onion/data/MOR
- Server Link 2
- https://aur0rablog.io/data/MOR
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.