Summary
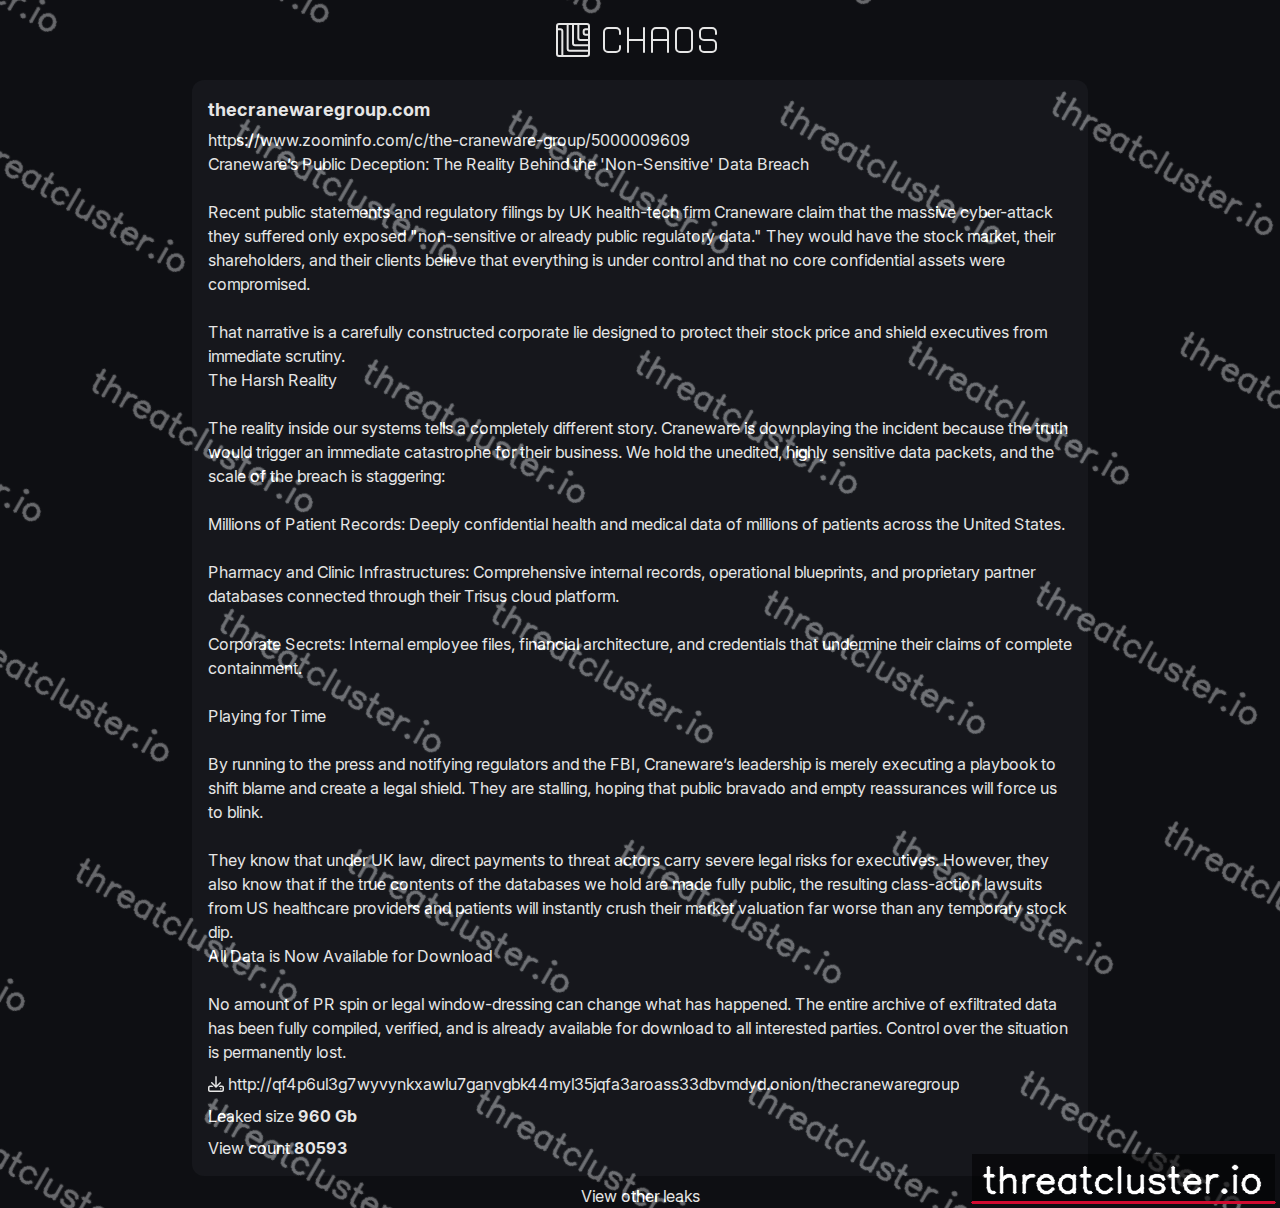
Written by ThreatClusterfrom site fields, file listing, victim profile, leak post, screenshotChaos claims to have exfiltrated 960 Gb from thecranewaregroup.com, describing the taken data as including patient records, pharmacy and clinic infrastructures, and corporate secrets. The leak page lists the victim domain as thecranewaregroup.com, a US health-tech organization that uses the Trisus cloud platform. The publication status is countdown on the leak page, and a sample of leaked data is linked via a URL on the page.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Victim profile
- Platforms
- Trisus cloud platform
What was taken
Craneware’s Public Deception: The Reality Behind the 'Non-Sensitive' Data Breach Recent public statements and regulatory filings by UK health-tech firm Craneware claim that the massive cyber-attack they suffered only exposed "non-sensitive or already public regulatory data." They would have the s…
Also stated on the leak page
Fields this group publishes that do not map to a standard column. Labels are the site's own.
- Sample of leaked data URL
- http://qf4p6ul3g7wyvynkxawlu7ganvgbk44myl35jqfa3aroass33dbvmdyd.onion/thecranewaregroup
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.