Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
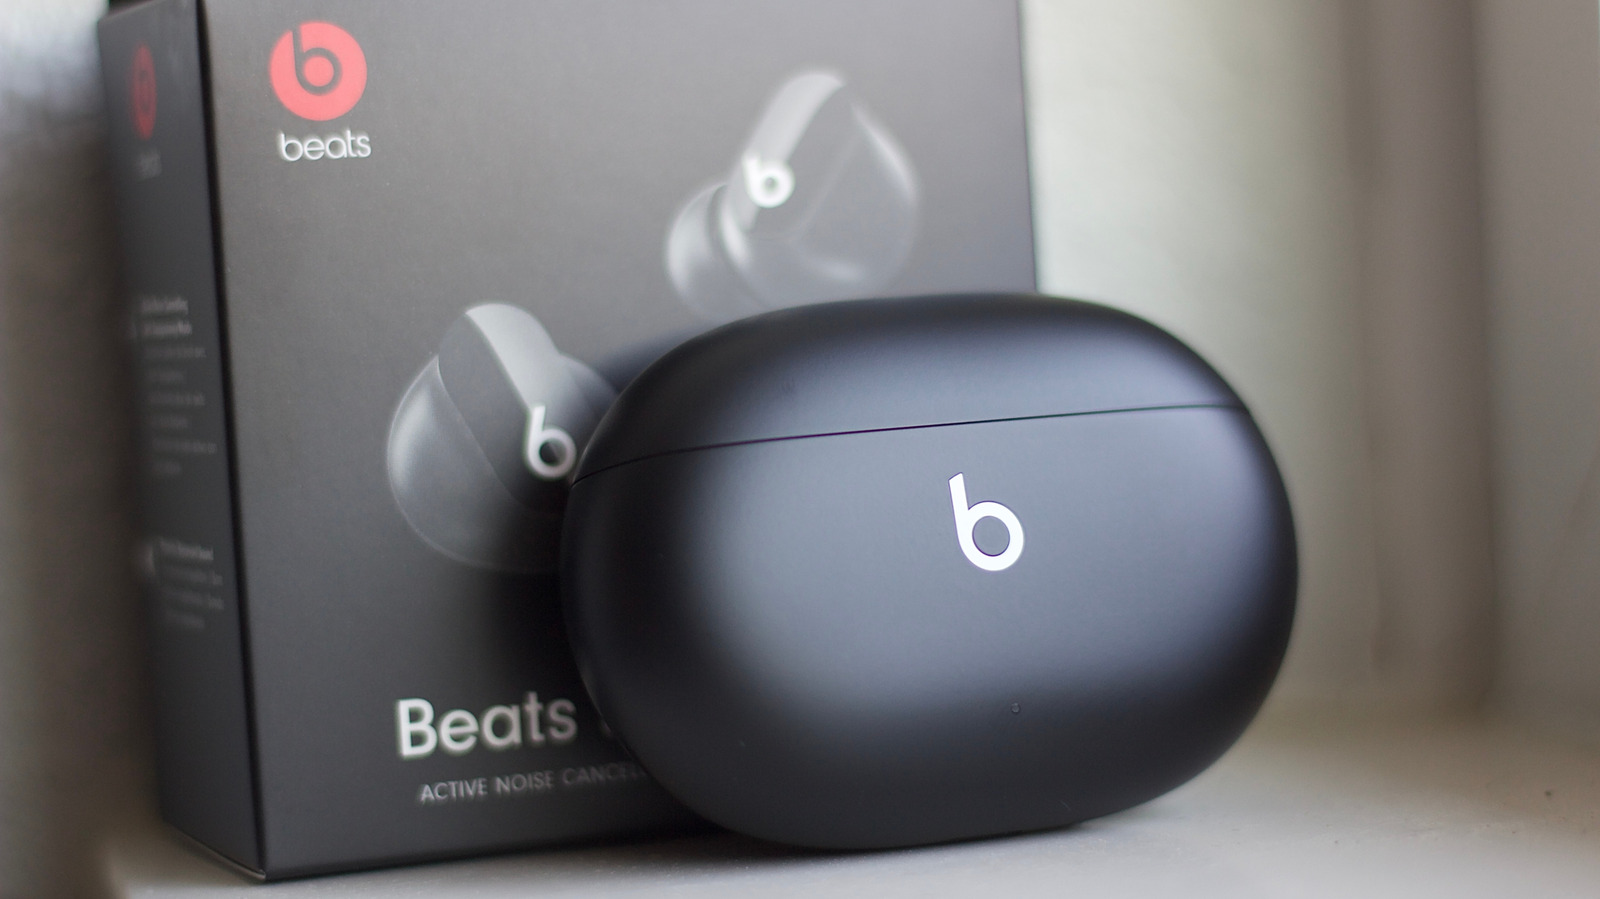
A serious security vulnerability has been discovered in Apple's Beats Studio Buds, allowing attackers within Bluetooth range to eavesdrop through the device's microphone. The flaw, identified as CVE-2025-20701, is linked to an open-source Airoha Bluetooth Audio SDK used in the earbuds. For exploitat...
Skullcandy Dime 3 wireless earbuds, specifically model S2DCW running firmware version 1.0.0.28, are affected by an unauthenticated Bluetooth pairing vulnerability, tracked as VU#859658. This flaw allows attackers within Bluetooth range to pair with the earbuds without user consent, enabling them to...
Security researchers have disclosed critical vulnerabilities in Bluetooth headphones and earbuds powered by Airoha Bluetooth System-on-Chips (SoCs). These flaws, identified as CVE-2025-20700, CVE-2025-20701, and CVE-2025-20702, could enable attackers to eavesdrop on conversations, steal sensitive da...