 Jamf
Security Flaw in Beats Studio Buds Allows Eavesdropping via Bluetooth
Article Content

- •CVE-2025-20701 allows unauthorized Bluetooth pairing with Beats Studio Buds.
- •Firmware update 1B211 released on June 16, 2026, addresses the vulnerability.
- •The flaw enables eavesdropping via the earbuds' microphone when exploited.
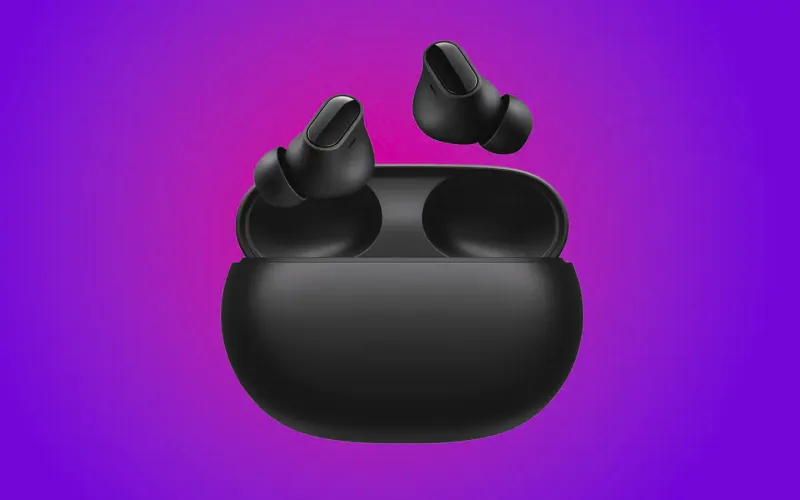
A vulnerability in Apple's Beats Studio Buds was discovered, allowing attackers to exploit an insecure Bluetooth pairing window. This flaw, identified as CVE-2025-20701, enables unauthorized pairing with the earbuds, potentially allowing eavesdropping through the device's microphone. Apple released a firmware update (1B211) on June 16, 2026, to address this issue, which affects devices actively seeking pair requests. The vulnerability was detailed in a technical writeup by Enno Rey Netzwerke (ERNW), who noted that the flaw was timing-dependent and could recur when the earbuds powered on. The issue was linked to a broader concern regarding Bluetooth security in audio devices. Users are advised to ensure their devices are updated to the latest firmware to mitigate this risk.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Apple and CVE-2022-32945 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How can I check if my Beats Studio Buds are updated?
What should I do if my earbuds are vulnerable?
Is this vulnerability actively being exploited?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Coordinated Attack On October 29, 2026, Binance suffered a large cyberattack attributed to North Korean hackers known as TraderTraitor, resulting in the theft of approximately $6.3 billion in cryptocurrency. The attackers gained initial access through social engineering tactics, including a fake job offer that led to malware…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…