Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
On September 15, 2026, CISA confirmed that ransomware gangs are actively exploiting a critical remote code execution vulnerability in VMware vCenter Server, tracked as CVE-2026-59310, which has a CVSS score of 9.8. This flaw, residing in the vCenter Syslog server, allows unauthenticated attackers wi...
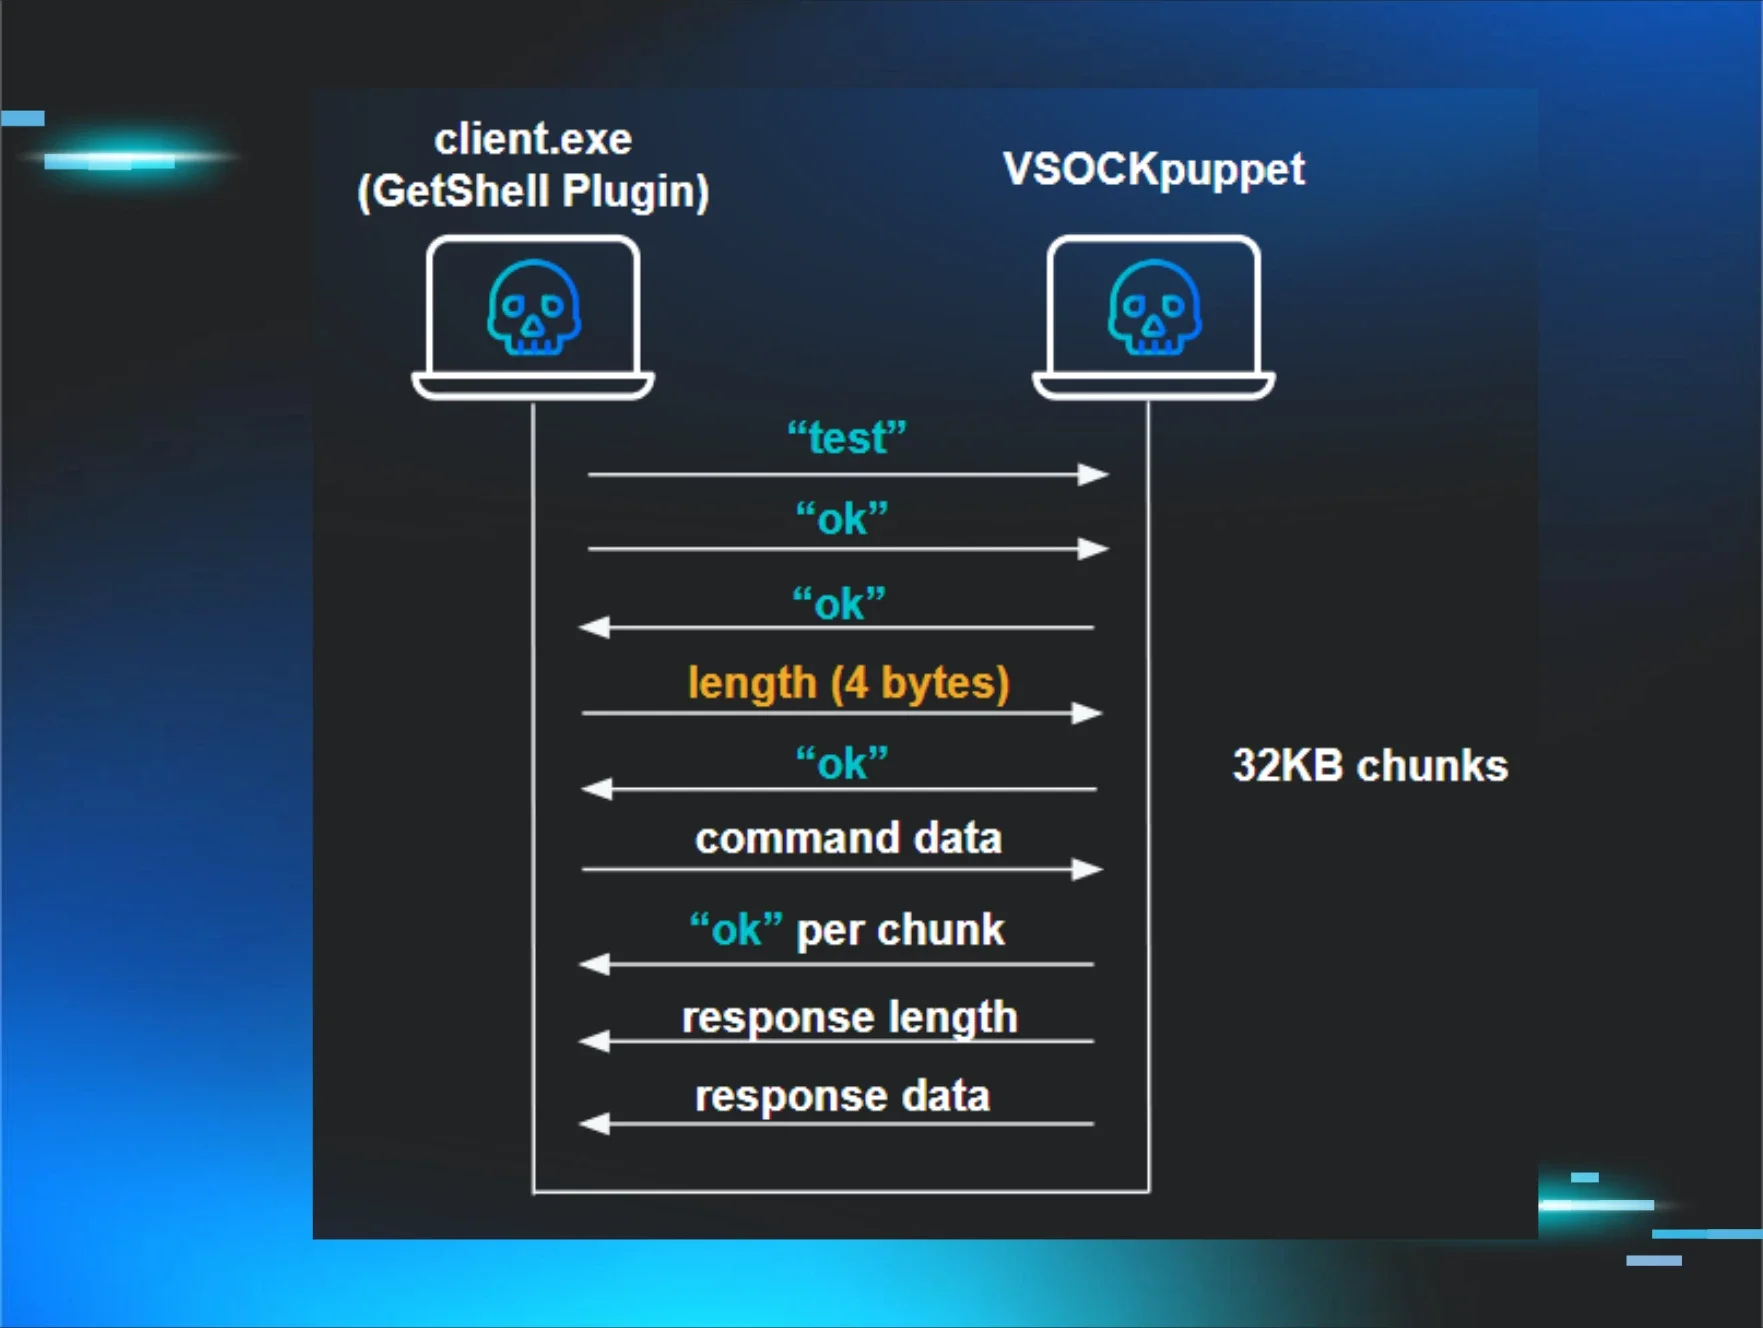
Chinese-linked cybercriminals utilized a VMware ESXi hypervisor escape kit to target the ESXi hypervisor. Researchers from Huntress reported that the toolkit was in development as early as February 2024 and was used in an intrusion observed in December 2025. The attack involved sophisticated techniq...
Chinese-linked cybercriminals utilized a VMware ESXi hypervisor escape toolkit over a year prior to the public disclosure of the vulnerabilities. Researchers at Huntress identified an intrusion in December 2025, revealing that the toolkit's development began as early as February 2024. This sophistic...
Chinese-speaking threat actors conducted attacks using a VMware ESXi exploit toolkit that leveraged three zero-day vulnerabilities, identified as CVE-2025-22224, CVE-2025-22225, and CVE-2025-22226. The initial access was gained through a compromised SonicWall VPN, allowing attackers to pivot to doma...