Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
On October 13, 2026, Ivanti disclosed a high-severity zero-day vulnerability tracked as CVE-2026-104935, affecting its Connect Secure (ICS) VPN appliances. This authentication bypass flaw allows unauthenticated attackers to execute arbitrary commands, with exploitation confirmed since at least Octob...
A vulnerability in Atlassian Data Center products, tracked as CVE-2026-21589 with a CVSS score of 9.3, was within two hours of its disclosure. The flaw allows arbitrary file access and affects multiple products, including Bitbucket, Confluence, and Jira. Exploitation activity targeting honeypot netw...
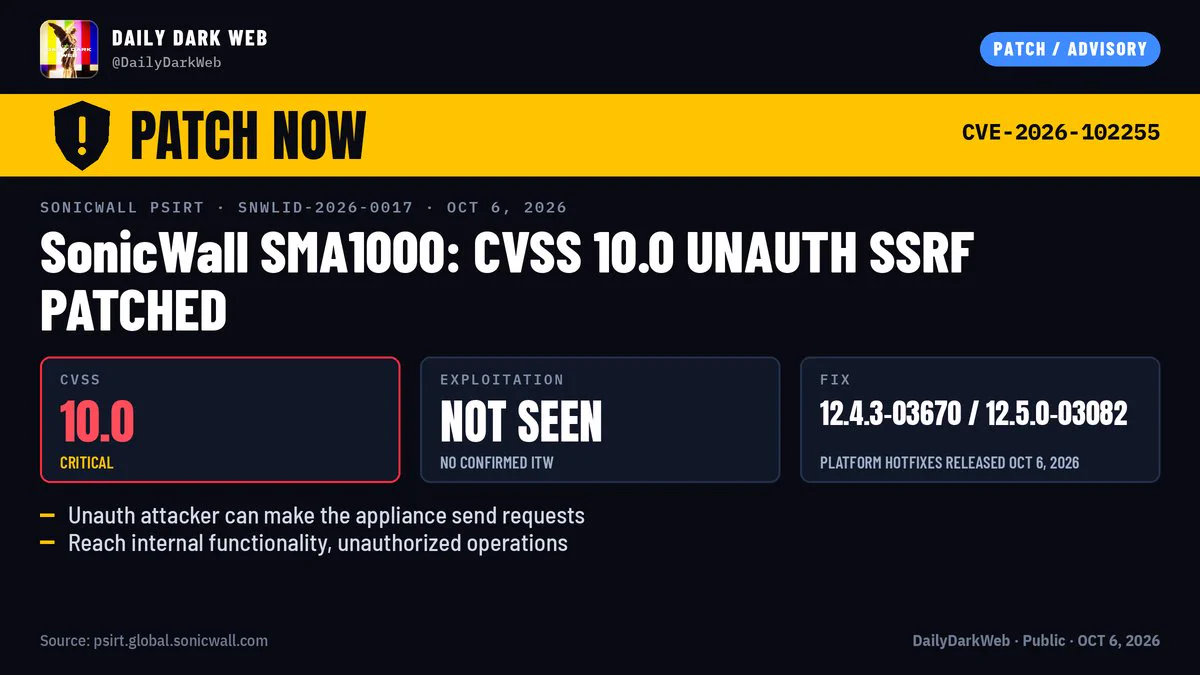
Two critical vulnerabilities, CVE-2026-85097 and CVE-2026-102255, are under active exploitation, affecting the WordPress Bricksforge plugin and SonicWall SMA 1000 appliances, respectively. The Bricksforge plugin allows unauthenticated remote code execution, while the SonicWall flaw enables server-si...
Two critical vulnerabilities have been reported in Atlassian products, CVE-2026-21589 and CVE-2026-102255. CVE-2026-21589, with a CVSS score of 9.3, was published on October 5, 2026, and its first public proof-of-concept (PoC) was released on October 7, 2026. CVE-2026-102255, published on October 7,...