Vulnerability Overview
Exploitation Activity
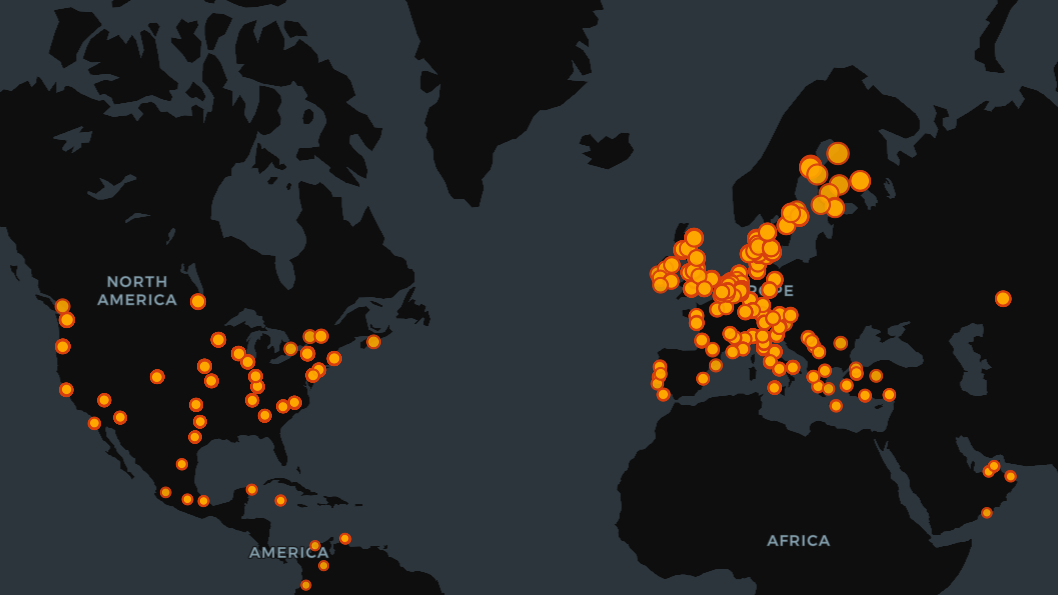
Exploitation Intelligence
Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass a...
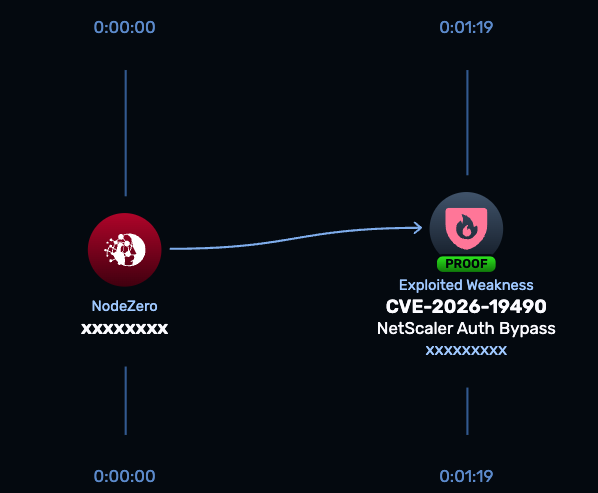
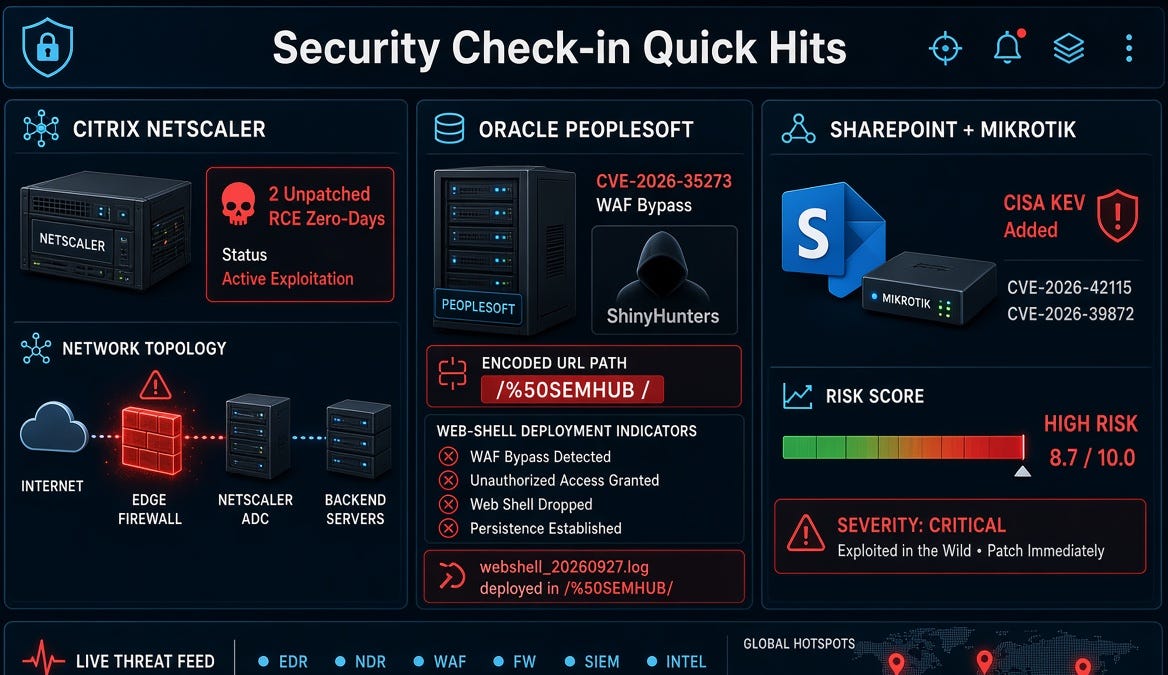
Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-20...
On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic....
On September 10, 2026, GitLab released patches for critical vulnerabilities CVE-2026-85706 and CVE-2026-87719. CVE-2026-85706, a path traversal flaw, allows unauthenticated users to read arbitrary files from GitLab servers, while CVE-2026-87719 enables credential theft via insecure deserialization....